
Introduction
In a world where remote work has become the norm, and cyberattacks grow more sophisticated by the quarter, endpoint security is no longer optional — it is the foundation of every resilient enterprise IT strategy. Whether you are a small business IT administrator securing a hybrid workforce or a Fortune 500 security architect deploying Zero Trust across thousands of endpoints, the tools you choose will define your organization’s exposure to risk.
Fortinet, founded in 2000 and headquartered in Sunnyvale, California, has grown from a firewall vendor into one of the world’s largest cybersecurity companies by revenue, serving more than 700,000 organizations across 190+ countries. Its core philosophy — a tightly integrated, platform-based approach called the Security Fabric — sets it apart in a market flooded with point solutions.
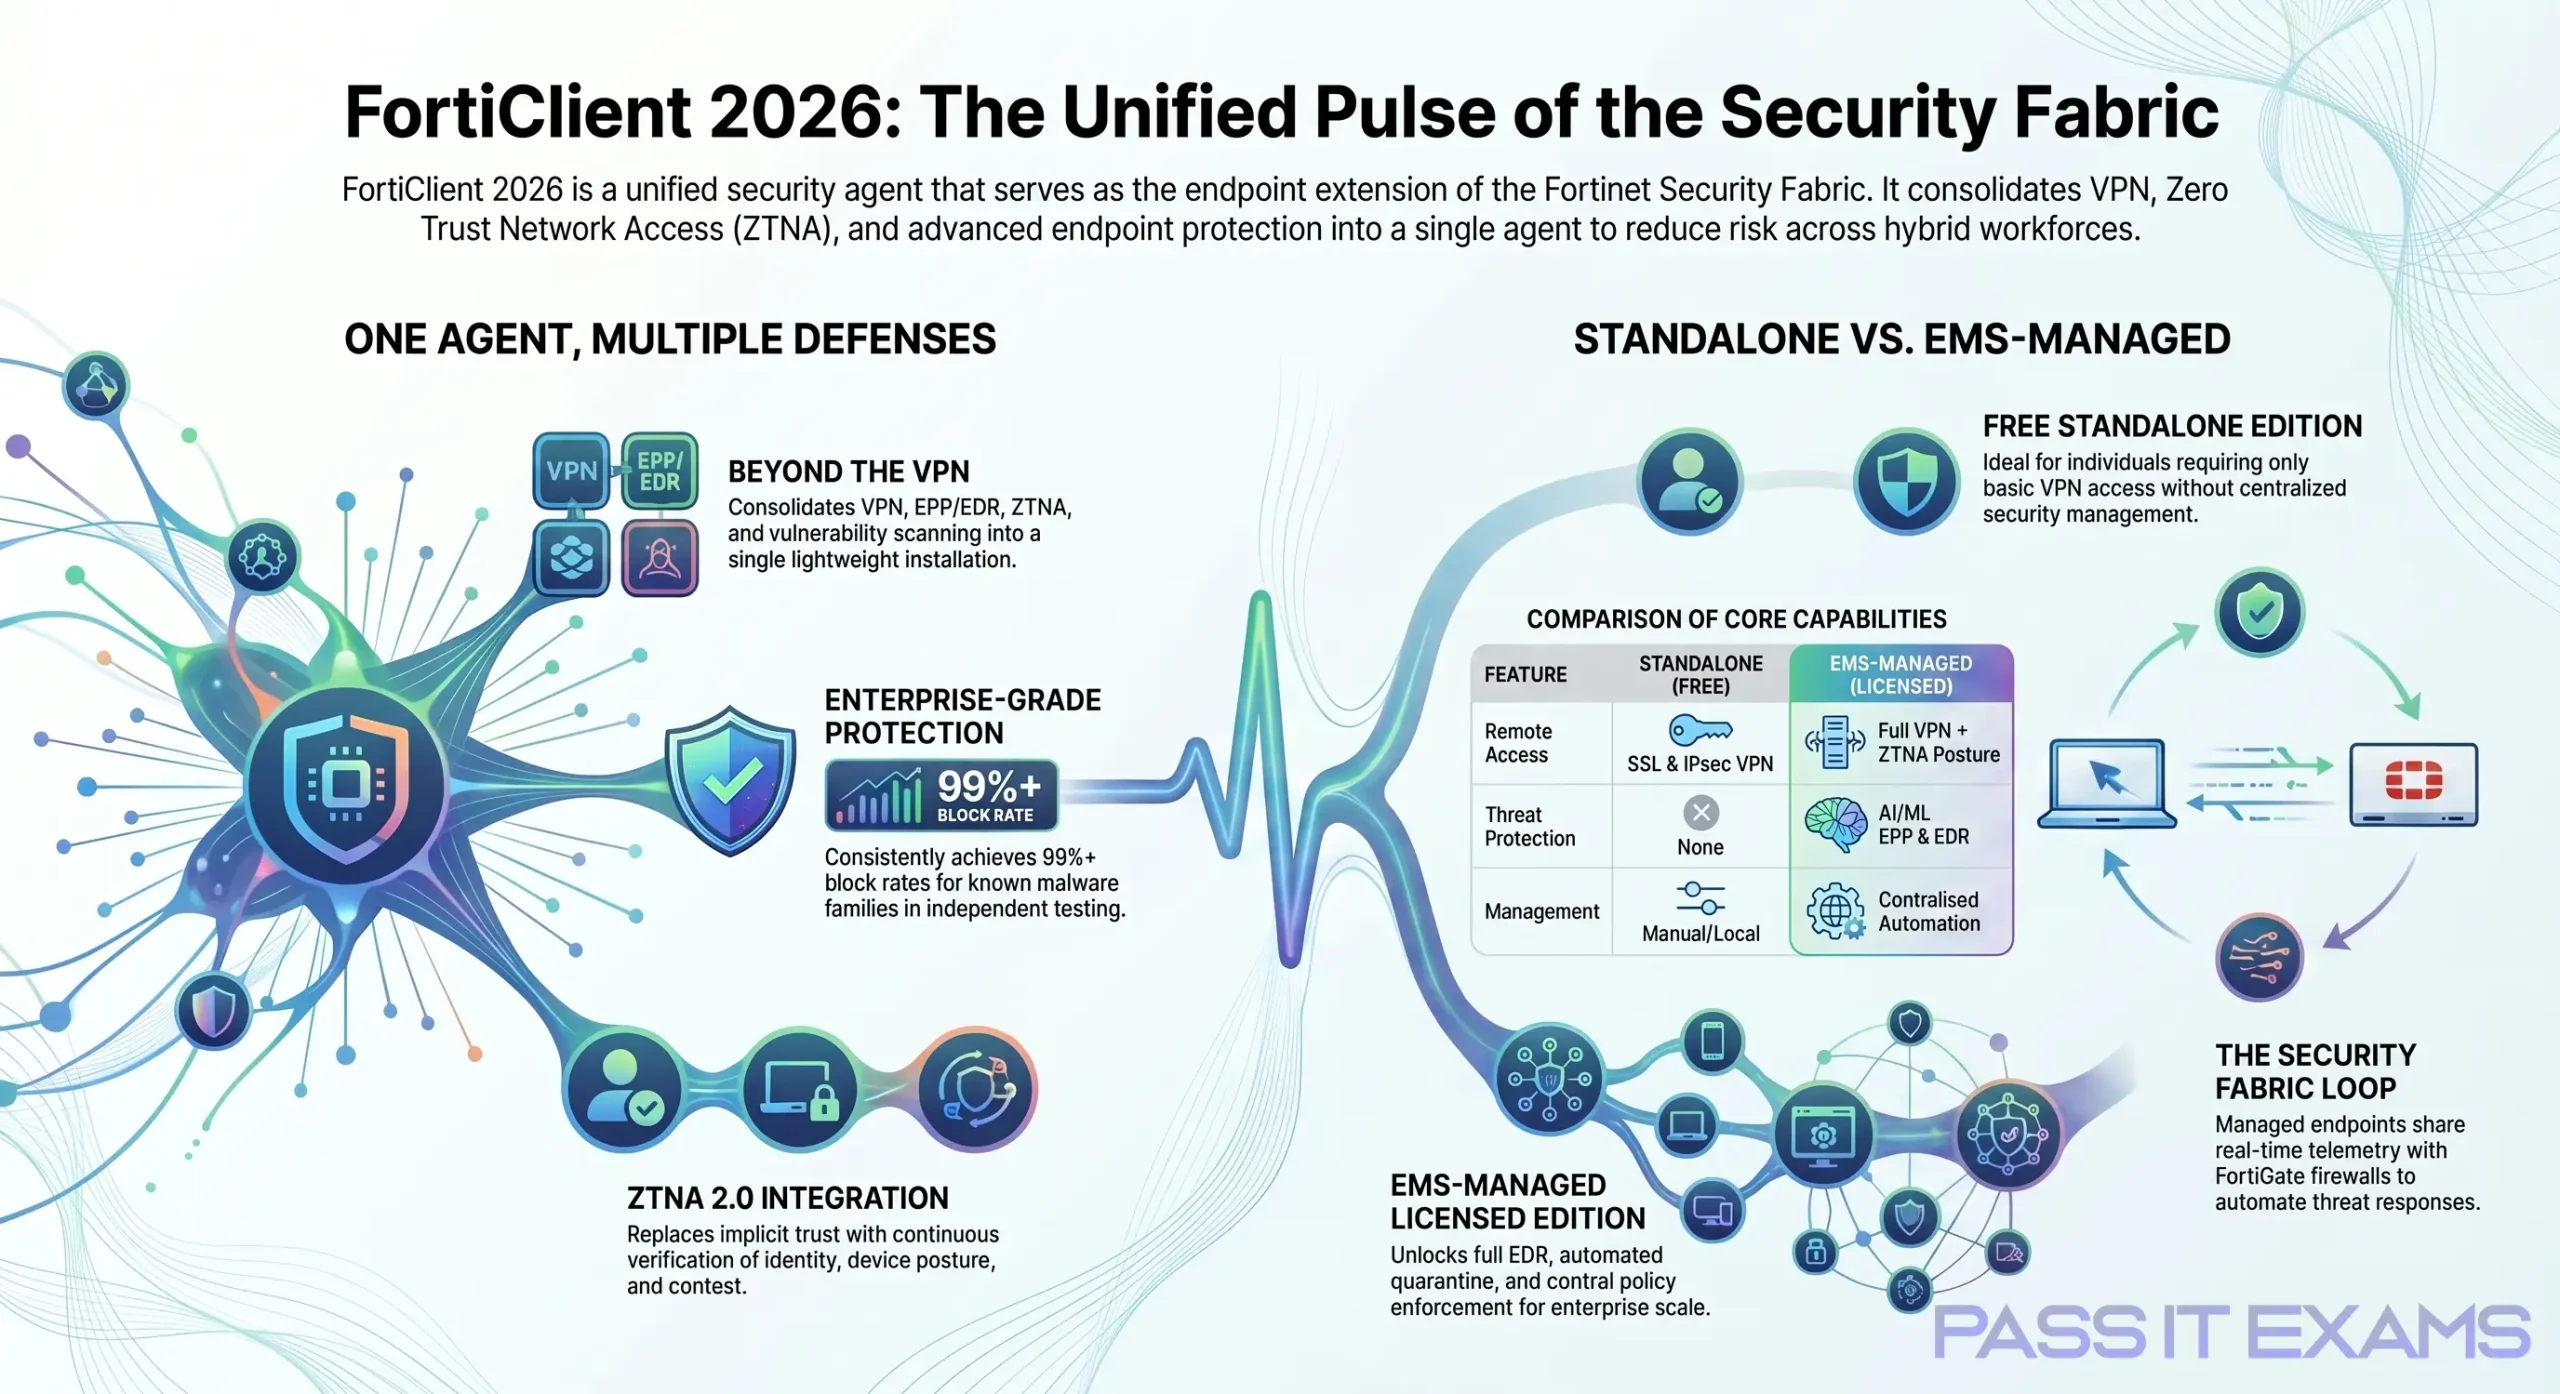
At the heart of Fortinet’s endpoint strategy sits FortiClient, a unified security agent that has evolved significantly into its 7.x generation. Far more than a simple VPN client, FortiClient in 2026 provides Zero Trust Network Access (ZTNA), endpoint protection (EPP/EDR), advanced threat prevention, web filtering, vulnerability scanning, and deep telemetry integration with the broader Security Fabric. It runs on Windows, macOS, Linux, iOS, and Android, making it one of the most versatile agents available.
The relevance of FortiClient in 2026 cannot be overstated. Remote and hybrid work arrangements have permanently expanded the attack surface. Traditional perimeter-based defenses are insufficient when employees connect from home networks, coffee shops, and airports. Ransomware, zero-day exploits, and supply-chain attacks continue to rise. Regulators worldwide increasingly mandate data protection and access controls that align with Zero Trust principles. Organizations need an endpoint agent that not only protects the device but also enforces policy, reports telemetry, and adapts access dynamically based on risk posture.
This guide is designed to be your definitive reference. Whether you are evaluating FortiClient for the first time, planning a corporate rollout, troubleshooting issues, or looking to optimize an existing deployment, every section below addresses your specific questions with accuracy grounded in official Fortinet documentation and verified practices as of June 2026.
What is Fortinet? Company & Product Portfolio Overview
Company Background and Scale
Fortinet was co-founded by brothers Ken and Michael Xie with the mission of delivering high-performance network security. Over two decades, the company expanded from network firewalls into a comprehensive cybersecurity platform. As of 2026, Fortinet:
- Serves 700,000+ customers globally across enterprise, government, telecom, and SMB sectors
- Employs over 13,000 people worldwide
- Holds a dominant market share in the network firewall and unified threat management (UTM) segments
- Maintains its own ASIC chip design (FortiASIC) for hardware-accelerated security processing
The Security Fabric Philosophy
What differentiates Fortinet from many competitors is its Security Fabric — a broad, integrated, and automated platform that connects network, endpoint, cloud, application, and security operations into a unified architecture. Rather than stitching together disparate vendor tools, the Security Fabric enables:
- Unified visibility across network, endpoint, cloud, and application layers
- Automated threat response — when a FortiClient endpoint detects a threat, the Security Fabric can quarantine the device, update firewall policies, and alert SOC analysts in near real-time
- Consistent policy enforcement regardless of where the user or device is located
- FortiOS is the underlying operating system powering most Fortinet hardware appliances, providing consistent feature sets and management
Key Products in the Fortinet Portfolio
| Product | Category | Role |
|---|---|---|
| FortiGate NGFW | Network Security | Core next-generation firewall, ZTNA gateway, SD-WAN |
| FortiClient | Endpoint Security | Unified endpoint agent (VPN, EPP, ZTNA, telemetry) |
| FortiClient EMS | Endpoint Management | Centralized management for FortiClient deployments |
| FortiAnalyzer | Analytics & Logging | Centralized log management, reporting, and forensics |
| FortiManager | Network Management | Centralized policy and configuration management for FortiGates |
| FortiSIEM | Security Operations | Security information and event management |
| FortiSOAR | Security Operations | Security orchestration, automation, and response |
| FortiSwitch | Network Infrastructure | Managed network switches integrated into the Security Fabric |
| FortiAP | Wireless | Managed wireless access points |
| FortiSASE | Cloud Security | Secure Access Service Edge delivered from the cloud |
| FortiWeb | Application Security | Web application firewall |
| FortiMail | Email Security | Email gateway with anti-phishing and sandboxing |
| FortiSandbox | Advanced Threat Protection | Dynamic malware analysis |
Where FortiClient Fits
FortiClient acts as the endpoint extension of the Security Fabric. Every laptop, desktop, or mobile device running FortiClient becomes a visible, managed, and policy-enforced node within the broader Fortinet ecosystem. When FortiClient is managed by FortiClient EMS (Endpoint Management Server), it shares posture data and telemetry with FortiGate firewalls, FortiAnalyzer, and FortiSIEM, creating a closed-loop security system in which endpoint activity directly informs network-level policy decisions.

What is FortiClient? Deep Dive
Overview: A Unified Endpoint Security Agent
FortiClient is Fortinet’s unified endpoint security agent, designed to deliver multiple security functions through a single lightweight installation. According to Fortinet’s official documentation, FortiClient’s core mission is to:
- Provide secure remote access (SSL VPN, IPsec VPN, ZTNA)
- Enforce endpoint protection (antivirus, anti-malware, anti-exploit)
- Deliver advanced threat prevention (behavioral detection, sandboxing)
- Perform compliance and vulnerability assessment
- Feed telemetry back to the Security Fabric for coordinated response
This consolidation is a key selling point: instead of deploying a separate VPN client, antivirus agent, and compliance checker, organizations can manage everything through a single agent and management console.
FortiClient Editions: Free vs. Full Licensed
A critical distinction for any evaluator is the difference between the free and licensed versions of FortiClient.
FortiClient Free Edition
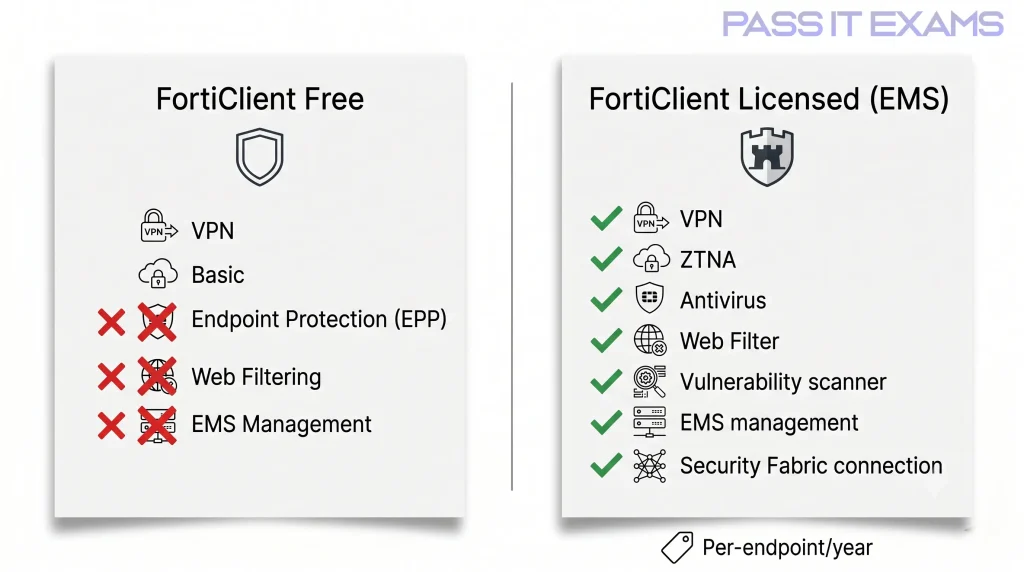
The free version of FortiClient is available directly from Fortinet’s website (fortinet.com) at no cost. It includes:
- SSL VPN connectivity to FortiGate appliances
- IPsec VPN connectivity
- Basic ZTNA connection capabilities
- Two-factor authentication support
- Basic web filtering (limited)
Important limitation: The free edition does not include EMS management, endpoint protection platform (EPP) features, advanced threat prevention, vulnerability scanning, or telemetry for Security Fabric integration. It is suitable for individuals or very small deployments needing only secure remote access.
FortiClient Licensed Edition (EPP/ZTNA)
The full licensed version of FortiClient, managed via FortiClient EMS, unlocks the complete feature set. Licensing is typically per-endpoint per-year and is purchased through Fortinet or its authorized partners. Features include all free-edition capabilities plus:
- Full Endpoint Protection Platform (EPP): real-time antivirus, anti-malware, anti-exploit
- Advanced Persistent Threat (APT) prevention via FortiSandbox integration
- Endpoint Detection and Response (EDR) capabilities
- Web filtering with full category controls
- Application firewall and application control
- Vulnerability scanning and patch management integration
- Device compliance verification (posture checking for ZTNA)
- Security Fabric telemetry and automated quarantine
- Central management via FortiClient EMS
Key Features in 2026 (FortiClient 7.x Series)
The FortiClient 7.x series, current as of mid-2026, includes significant enhancements over previous generations. Here is a feature-by-feature breakdown:
Secure Remote Access
- SSL VPN: Full-tunnel and split-tunnel modes. Supports certificate-based and multi-factor authentication. Integrates with FortiToken, LDAP, RADIUS, and SAML identity providers.
- IPsec VPN: IKEv1 and IKEv2 support with hardware-accelerated performance on compatible devices.
- Always-On VPN: Ensures the endpoint is never unprotected — VPN automatically reconnects if the connection drops, enforced via EMS policy.
- ZTNA (Zero Trust Network Access): Provides application-level access rather than network-level access. Users authenticate per application, and access is granted based on identity, device posture, and context. Eliminates implicit trust.
Endpoint Protection Platform (EPP)
- Real-time antivirus and anti-malware: Signature-based and heuristic detection engines, updated via FortiGuard threat intelligence services.
- Anti-exploit protection: Memory and behavior-based detection of exploitation techniques, including fileless malware.
- Ransomware protection: Behavioral monitoring for encryption patterns; can automatically roll back file changes in certain configurations.
Advanced Threat Prevention
- FortiSandbox integration: Suspicious files are submitted to FortiSandbox (on-premises or cloud) for dynamic behavioral analysis. Verdicts feed back into the endpoint policy automatically.
- AI/ML-enhanced detection: FortiClient 7.x leverages machine learning models trained on Fortinet’s global FortiGuard threat intelligence (processing billions of events daily) to detect novel threats without signatures.
- Inline CASB (Cloud Access Security Broker): Shadow IT detection and control over SaaS application usage.
Web Filtering and Application Control
- Web content filtering: 75+ URL categories with granular allow/block/warn controls. Enforced both on-network and off-network (critical for remote workers).
- DNS filtering: Blocks malicious domains at the DNS resolution level, an early defense layer against phishing and C2 communications.
- Application firewall: Layer-7 visibility and control over application traffic, preventing unauthorized application use.
- Application signatures: Over 3,000+ application signatures for accurate classification.
Vulnerability Management
- Vulnerability scanning: Periodically scans installed software for known CVEs and reports to EMS.
- Patch management integration: Can integrate with patch management tools; EMS can enforce that unpatched endpoints are quarantined or restricted.
- OS compliance checking: Verifies that endpoints meet minimum OS patch levels as a condition for ZTNA access.
Security Fabric Telemetry
- Device registration: Endpoints register with FortiGate and EMS, providing identity-to-IP mapping visible across the Fabric.
- Incident correlation: Endpoint events are correlated with network events in FortiAnalyzer, enabling investigation across both layers.
- Automated quarantine: If FortiAnalyzer or FortiSIEM detects a threat, the Security Fabric can trigger FortiClient to quarantine the endpoint — isolating it from the network while retaining management access for remediation.
SASE Integration
FortiClient serves as the agent for FortiSASE, Fortinet’s cloud-delivered Secure Access Service Edge platform. When integrated with FortiSASE, FortiClient tunnels all traffic (or split-tunneled traffic) through Fortinet’s cloud security points of presence (PoPs) globally, applying web filtering, CASB, ZTNA, and threat prevention in the cloud — ideal for organizations with distributed workforces that cannot route all traffic through an on-premises FortiGate.
Key Use Cases & Benefits
Use Case 1: Secure Remote Access with Always-On VPN
The most immediate use case for FortiClient is providing secure, encrypted access for remote and hybrid workers. With Always-On VPN, the endpoint is continuously protected regardless of network location. Key configurations include:
- Auto-connect on logon: VPN establishes before Windows login, ensuring the endpoint is never on an unprotected network.
- Split tunneling: Only corporate traffic routes through the VPN; internet traffic exits locally, reducing bandwidth burden on corporate infrastructure.
- Full tunneling: All traffic routes through the corporate FortiGate, enabling full inspection and web filtering for every connection.
According to Fortinet’s documentation, Always-On VPN combined with EMS-enforced compliance checking ensures that only healthy, policy-compliant devices can maintain VPN sessions — a critical control for regulated industries.
Use Case 2: Corporate Endpoint Security and Compliance
For organizations that need to demonstrate regulatory compliance (HIPAA, PCI DSS, GDPR, ISO 27001, NIST CSF), FortiClient’s vulnerability scanning, patch status reporting, and device compliance enforcement capabilities provide audit-ready evidence. EMS generates reports showing:
- Percentage of endpoints meeting compliance baseline
- Software inventory across the fleet
- Vulnerability exposure by CVE severity
- Security event history per endpoint
Use Case 3: Zero Trust Network Access (ZTNA 2.0)
ZTNA is the most strategically significant evolution in FortiClient’s feature set. Unlike VPN — which grants broad network access once authenticated — ZTNA grants access to specific applications based on continuous verification of:
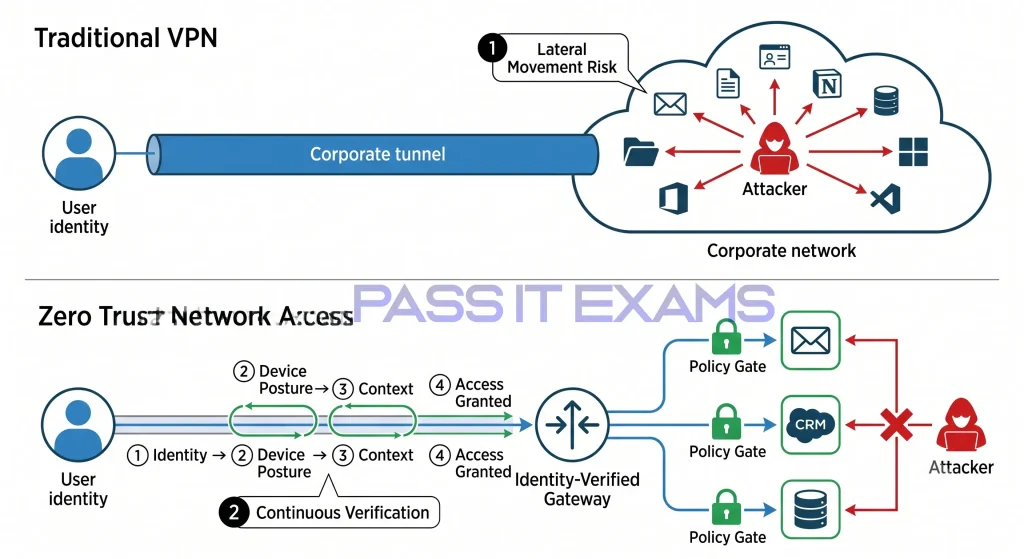
- User identity (via LDAP, SAML, MFA)
- Device posture (OS patch level, AV status, disk encryption status)
- Contextual factors (time of day, location, risk score)
FortiClient 7.x supports ZTNA as a universal ZTNA model, meaning the same policy framework applies whether the user is off-premises (connecting remotely) or on-premises (connecting via LAN). This eliminates the two-tier security model where on-premises users were implicitly trusted.
Use Case 4: Seamless Security Fabric Integration
For organizations already running FortiGate firewalls, the value of FortiClient’s integration is extremely high. Benefits include:
- Single-pane-of-glass visibility: Endpoint events appear alongside network events in FortiAnalyzer dashboards
- Unified policy management: Security policies reference user and device identity from FortiClient, not just IP addresses
- Automated incident response: A malware detection on an endpoint can automatically trigger a FortiGate policy change to block C2 traffic
- Reduced tool sprawl: Organizations can replace separate endpoint AV, VPN, and vulnerability management tools with a single FortiClient deployment
Quantifiable Benefits
Where official Fortinet data and third-party validation (such as NSS Labs and SE Labs testing) support it:
- FortiClient’s combined threat prevention (AV + behavioral + sandboxing) consistently achieves 99%+ block rates in independent tests for known malware families
- ZTNA deployments have been documented to reduce the blast radius of credential theft incidents, since compromised credentials cannot grant broad network access
- Consolidated endpoint management through EMS has been reported by enterprise customers to reduce endpoint management overhead versus managing multiple point-product agents
Standalone vs. EMS-Managed FortiClient
One of the most important architectural decisions when deploying FortiClient is whether to run it standalone (without EMS) or with centralized management through FortiClient EMS (Endpoint Management Server).

| Feature / Capability | Standalone FortiClient | EMS-Managed FortiClient |
|---|---|---|
| VPN (SSL & IPsec) | Full support | Full support + centralized profiles |
| ZTNA | Basic (limited posture) | Full ZTNA with posture tagging |
| Antivirus / Anti-malware | Not available (free) | Full EPP |
| Advanced Threat Prevention | Not available | With FortiSandbox integration |
| Web Filtering | Limited (free only) | Full category control |
| Application Control | Not available | Full control |
| Vulnerability Scanning | Not available | With reporting to EMS |
| Centralized Policy Deployment | Manual per-device | Automated, role-based |
| Device Compliance Enforcement | Not enforced | Enforced via posture tags |
| Security Fabric Telemetry | Minimal | Full bidirectional telemetry |
| FortiSandbox Integration | Not available | On-premises or cloud |
| Automated Quarantine | Not available | Fabric-triggered quarantine |
| Software Inventory Reporting | Not available | Centralized asset inventory |
| Mass Deployment (MSI/MDM) | Manual scripting required | Native EMS deployment tools |
| Licensing Model | Free (VPN only) | Per-endpoint subscription |
| Scalability | 1–50 endpoints (practical) | Unlimited (EMS scales to 100,000+) |
| Ideal Use Case | Individual users, VPN-only needs | Enterprise and mid-market deployments |
| Management Console | Local device UI only | EMS web console + FortiGate integration |
| Update Management | Manual or Windows Update | Centralized via EMS |
| Reporting & Dashboards | None | Rich dashboards, compliance reports |
When to Choose Standalone
Standalone FortiClient is appropriate when:
- You need a VPN-only solution for a small number of users (under 20–30)
- You are an individual user connecting to a corporate FortiGate remotely
- Your organization already has a separate, mature EPP solution and only needs the FortiClient VPN module
- Budget constraints prevent licensing at this time
When to Choose EMS-Managed
EMS-managed deployment is the right choice when:
- You need to enforce the security policy consistently across 20+ endpoints
- ZTNA is a requirement (EMS is required for full ZTNA posture checking)
- Your organization has compliance reporting requirements
- You want to integrate FortiClient into a broader Security Fabric with FortiGate and FortiAnalyzer
- Automated response and quarantine capabilities are needed
System Requirements & Compatibility
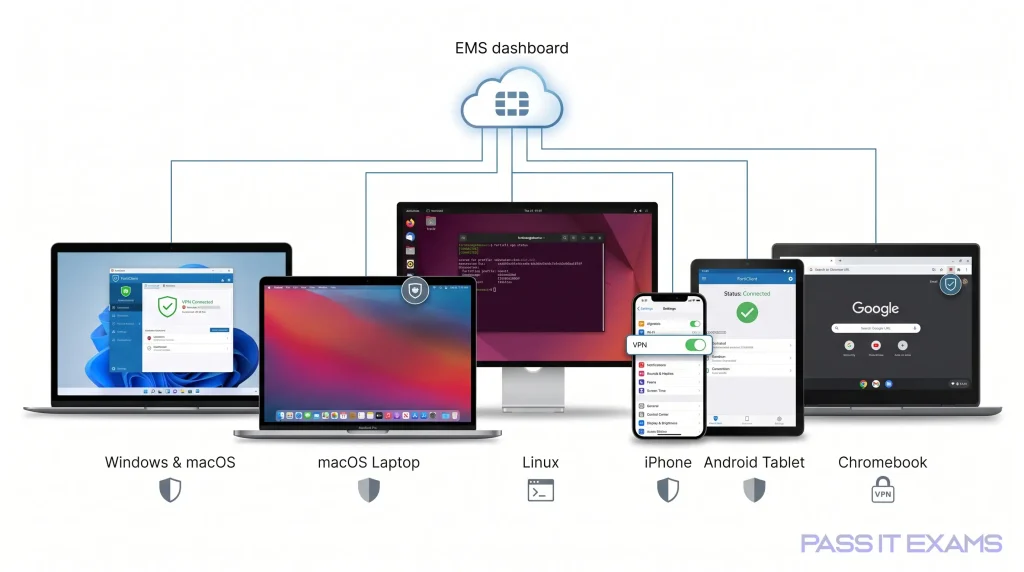
Supported Platforms (FortiClient 7.x)
According to Fortinet’s official release notes for the 7.x series:
Windows
- Windows 11 (64-bit): All editions except Home (which lacks Group Policy support for enterprise deployment)
- Windows 10 (64-bit): Versions 21H2 and later recommended
- Windows Server 2019 / 2022: Supported for server-side deployments (limited feature set — no GUI in some configurations)
- Minimum RAM: 2 GB (4 GB recommended for full EPP features)
- Minimum Disk: 600 MB free space
- Processor: x86-64 compatible; 1 GHz or faster
macOS
- macOS Ventura (13.x), Sonoma (14.x), and Sequoia (15.x)
- Apple Silicon (M1/M2/M3) natively supported via universal binary
- System Extensions: Required for web filtering and network monitoring; users must approve during installation
- Minimum RAM: 4 GB
Linux
- Ubuntu 20.04 LTS, 22.04 LTS (64-bit)
- Red Hat Enterprise Linux 8.x, 9.x
- CentOS 8 (note: CentOS 8 reached end-of-life; RHEL or Stream preferred)
- Linux support is primarily for VPN and ZTNA; EPP feature availability varies by distribution
iOS
- iOS 15.0 or later
- Features: SSL VPN, IPsec VPN, ZTNA (limited), web filtering (via VPN profile)
- Managed deployment via Apple Business Manager/MDM
Android
- Android 9.0 (Pie) or later
- Features: SSL VPN, IPsec VPN, ZTNA (limited), web filtering
- Managed deployment via Android Enterprise / MDM
Browser Compatibility
For the EMS management console web interface:
- Google Chrome (latest stable)
- Mozilla Firefox (latest stable)
- Microsoft Edge (Chromium-based, latest stable)
- Internet Explorer is not supported
Known Limitations
- FortiClient on Linux does not support the full EPP feature set; endpoint protection features are primarily available on Windows and macOS
- iOS and Android clients have limited ZTNA posture checking compared to desktop platforms — device certificates and basic health checks are supported, but deep OS inspection is constrained by mobile platform sandbox restrictions
- Windows ARM (e.g., Snapdragon X Elite devices) support varies; check Fortinet’s release notes for specific build compatibility
- Virtualized environments: FortiClient functions in VMs (VMware, Hyper-V), but some behavioral detection features may have reduced efficacy due to hypervisor abstraction
How to Get Started
Step 1: Download FortiClient Safely
Always download FortiClient exclusively from official Fortinet sources. Third-party download sites may distribute modified, outdated, or malicious versions.
Official download locations:
- FortiClient (free): https://www.fortinet.com/products/endpoint-security/forticlient
- FortiClient (licensed/EMS-managed): Via your Fortinet customer portal at https://support.fortinet.com or through your authorized Fortinet partner
- Fortinet Documentation Portal: https://docs.fortinet.com — always verify the version-specific documentation before deploying
⚠️ Security Warning: Never install FortiClient from unofficial sources, torrents, or software aggregator sites. Verify the SHA-256 hash of your downloaded installer against Fortinet’s published checksums in the support portal.
Step 2: Choose Your Installation Path
Individual / Standalone Installation
For individuals or small deployments not using EMS:
- Download the appropriate installer for your OS from the official site
- Run the installer as Administrator (Windows) or with elevated privileges (macOS/Linux)
- Accept the license agreement and choose your installation components
- On Windows, allow the FortiClient System Extension if prompted by Windows Defender SmartScreen
- On macOS, approve System Extensions and Full Disk Access in System Settings > Privacy & Security
- Launch FortiClient and configure your VPN connection using your organization’s FortiGate hostname and credentials
Enterprise / EMS-Managed Deployment
For enterprise deployments managed via EMS, the process involves:
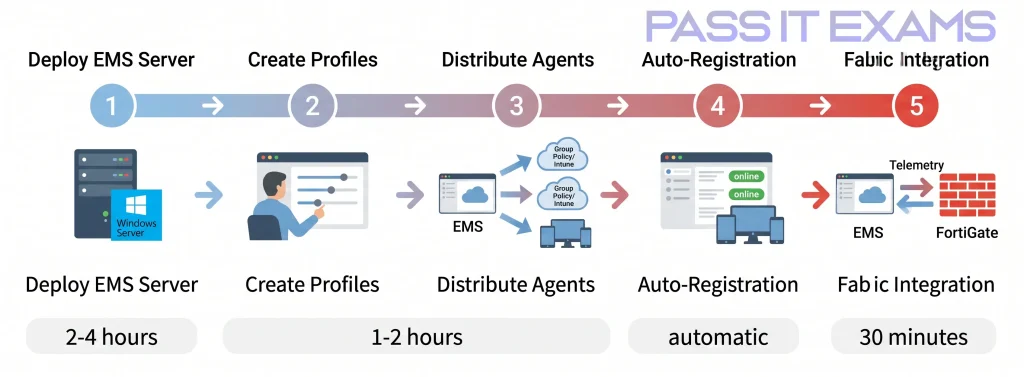
- Deploy FortiClient EMS on a Windows Server (physical or virtual)
- Generate deployment packages in EMS that pre-configure the agent with endpoint profiles
- Distribute installers via Group Policy, SCCM/Intune, or EMS’s built-in deployment tool
- Endpoints auto-register with EMS upon installation, inheriting their assigned security profile
- Configure FortiGate integration in EMS to enable Security Fabric telemetry
Step 3: First-Time Configuration and Profile Setup
After installation, basic configuration includes:
- VPN Profile: Enter your organization’s FortiGate SSL VPN gateway (hostname or IP), authentication method (username/password, certificate, SAML), and realm
- Multi-Factor Authentication: Configure FortiToken (hardware or mobile), TOTP, or push notification MFA if required by your organization
- Auto-connect settings: If using Always-On VPN, configure trusted network detection so VPN activates only on untrusted networks
- Software update settings: Ensure FortiGuard signature updates are enabled and scheduled (recommended: every 4 hours minimum)
Advanced Topics
Deep Security Fabric Integration with FortiGate
When FortiClient EMS is registered with FortiGate via the Security Fabric connector, the integration unlocks several capabilities not available with standalone deployments:
- Dynamic Address Groups: FortiGate can reference EMS-defined endpoint tags (e.g., “compliant,” “at-risk,” “quarantined”) in firewall policies. This means policy enforcement automatically adapts to endpoint state — a device flagged by FortiClient as infected is instantly restricted at the network level without manual administrator intervention.
- User-Device Correlation: FortiGate maps IP addresses to specific users and devices using FortiClient registration data, enabling user-based rather than IP-based firewall policies. This is critical in DHCP environments where IP addresses change frequently.
- ZTNA Access Proxy: FortiGate 7.x serves as the ZTNA access proxy. FortiClient sends a device certificate and posture tags to FortiGate, which grants or denies per-application access based on ZTNA rules. No VPN tunnel to the full network is required.
Centralized Management with FortiClient EMS
FortiClient EMS (Endpoint Management Server) is the nerve center of enterprise FortiClient deployments. Key management capabilities include:
Deployment and Profile Management
- Create endpoint profiles that define which FortiClient features are active and how they are configured
- Assign profiles by user group, AD organizational unit, or device category
- Push configuration changes to thousands of endpoints simultaneously
- Monitor deployment status and identify endpoints that have missed updates or are out of compliance
Policy Enforcement
- Define compliance rules (e.g., “endpoint must have AV enabled, OS patches applied within 30 days, disk encryption active”)
- Assign compliance tags that FortiGate consumes for dynamic policy enforcement
- Configure automatic remediation actions (show warning, restrict access, quarantine) for non-compliant devices
Reporting and Visibility
- Real-time dashboard showing endpoint count, compliance posture, active threats, and vulnerability exposure
- Per-endpoint drill-down showing software inventory, active connections, security events, and policy assignment
- Scheduled and on-demand compliance reports exportable as PDF or CSV
- Integration with FortiAnalyzer for cross-correlation with network-level events
Performance Optimization Tips
One of the most common concerns about endpoint security agents is performance impact. Here are evidence-based optimization strategies for FortiClient:
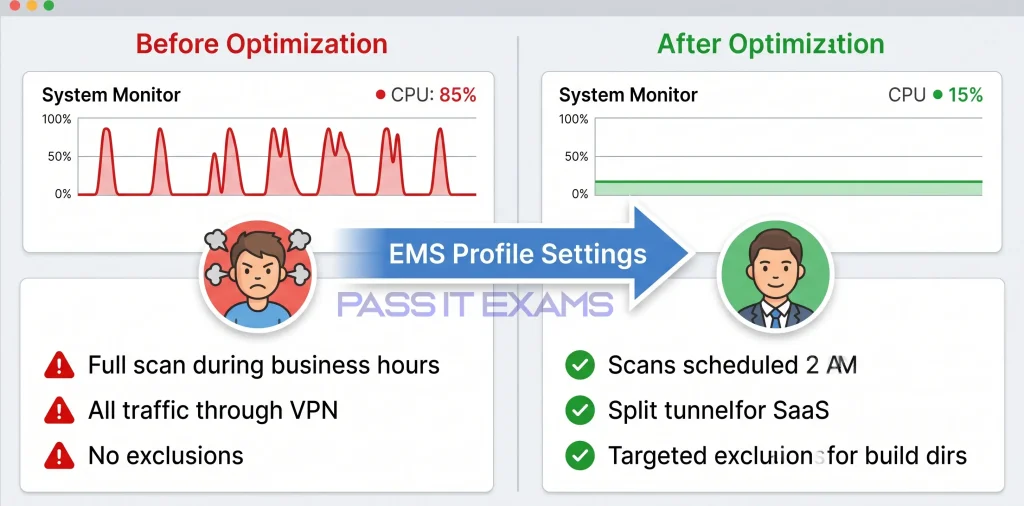
- Exclusions: Configure scan exclusions for known-safe directories with high I/O (e.g., software build directories, database data directories). Document all exclusions and review them quarterly. Over-exclusion creates security gaps; under-exclusion creates performance issues.
- Scheduled Scans: Schedule full disk scans during off-hours (overnight or weekends) rather than during business hours. Real-time protection handles ongoing threats; full scans are primarily for discovering dormant threats.
- FortiSandbox Timeout Configuration: If FortiSandbox integration causes delays when opening documents, review timeout settings in EMS. A 10–15 second sandbox verdict timeout is typically acceptable; longer timeouts may frustrate users.
- VPN Split Tunneling: In performance-sensitive environments, configure split tunneling so only corporate-destined traffic routes through the VPN. This significantly reduces VPN gateway load and improves user experience for cloud-based SaaS applications.
- EMS Communication Frequency: The default EMS heartbeat interval is sufficient for most deployments. Reducing the heartbeat interval below default values increases network and EMS server load without a significant security benefit.
Troubleshooting Common Issues
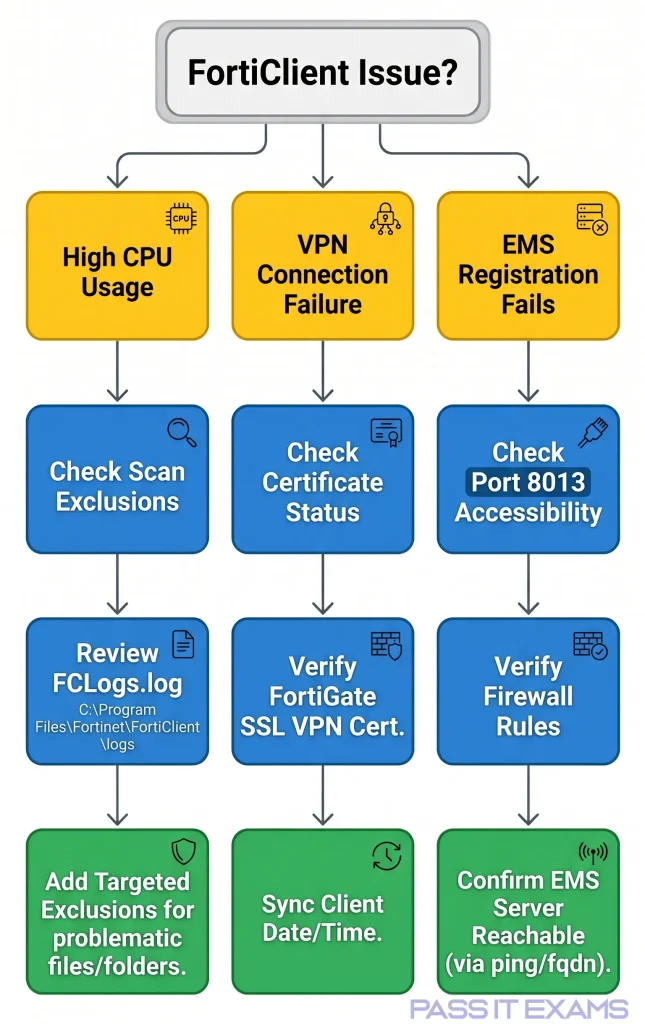
| Issue | Likely Cause | Resolution |
|---|---|---|
| High CPU usage | Real-time scan on high-I/O process | Add targeted exclusions; review FortiClient log for scanning activity |
| VPN connection failure | Certificate mismatch or expired cert | Verify FortiGate certificate is valid; check client date/time sync |
| VPN connects, but no traffic | Split tunnel misconfiguration or DNS issue | Review the routing table; verify the DNS server in the VPN profile |
| EMS registration failure | Firewall blocking EMS port (8013) | Ensure TCP 8013 is open between the endpoint and EMS |
| Signature update failure | Proxy or firewall blocking FortiGuard | Allow FortiGuard update servers through proxy; check license validity |
| ZTNA access denied unexpectedly | Device posture non-compliant | Check EMS compliance tags; review which posture rule is failing |
| macOS System Extension blocked | MDM policy or the user not approving | Pre-approve via MDM (Apple Configuration Profile) before deployment |
| FortiClient crashes on startup | Corrupted installation or conflict | Uninstall using FortiClientTools, clean the registry, and reinstall |
For persistent issues, Fortinet’s support portal at support.fortinet.com provides access to the Technical Assistance Center (TAC) and a searchable knowledge base.
Notable 2026 Enhancements and Known Issues
FortiClient 7.x in 2026 introduced or matured several capabilities:
- Improved AI/ML models for behavioral detection, with lower false-positive rates compared to 7.0.x
- Enhanced ZTNA posture checks, including integration with Microsoft Intune and Jamf compliance status
- SASE agent improvements for FortiSASE PoP selection intelligence and reduced latency
- Inline CASB enhancements with broader SaaS application coverage
⚠️ Patching Advisory: As with any security software, always run the latest stable release of FortiClient and FortiClient EMS. Check Fortinet’s PSIRT (Product Security Incident Response Team) advisories regularly at https://www.fortinet.com/corporate/about-us/psirt. Critical vulnerabilities in endpoint agents are actively targeted by sophisticated adversaries. Never defer security patches.
Pros, Cons & Real-World Considerations
Strengths
- Tight Security Fabric Integration: For organizations already using FortiGate firewalls, FortiClient’s integration value is unmatched. The bidirectional telemetry, dynamic policy enforcement, and unified visibility across endpoint and network layers are difficult to replicate with competing products.
- Single-Agent Consolidation: Replacing a separate VPN client, antivirus, web filter, and vulnerability scanner with a single agent simplifies the end-user experience, reduces potential conflicts between agents, and reduces overall software licensing complexity.
- Strong ZTNA Capabilities: Fortinet’s ZTNA implementation is mature and aligns with zero trust principles in practical, deployable ways. The integration of EMS posture tags with the FortiGate access proxy provides a robust alternative to legacy VPN.
- Cross-Platform Coverage: Support for Windows, macOS, Linux, iOS, and Android from a single management platform (EMS) is operationally valuable for mixed-OS environments.
- Comprehensive Threat Intelligence: FortiGuard Labs, Fortinet’s threat intelligence organization, provides one of the largest and most frequently updated threat intelligence feeds in the industry, benefiting all FortiClient detection capabilities.
Weaknesses and Honest Criticisms
- Resource Usage on Endpoints: Some users and administrators report that FortiClient’s full EPP stack (AV + behavioral monitoring + web filtering) consumes more RAM and CPU than lighter-weight alternatives, particularly on older hardware. Organizations with aging endpoint fleets should benchmark before wide deployment.
- EMS Management Learning Curve: FortiClient EMS is powerful but complex. Administrators new to the platform report a significant learning curve for configuring ZTNA, compliance rules, and Fabric integration correctly. Fortinet’s documentation is comprehensive but dense. Factor training time into deployment planning.
- Licensing Complexity: Fortinet’s licensing model has multiple SKUs (FortiClient EPP, ZTNA, Chromebook, etc.) that can be confusing to navigate, particularly for organizations that require different feature sets across device types. Work with a Fortinet-certified partner to design the right licensing structure.
- Occasional Stability Issues: Enterprise-scale FortiClient deployments occasionally encounter bugs in new releases — particularly in the first minor release following a major version increment. Best practice is to wait for the first or second maintenance release (e.g., 7.x.1 rather than 7.x.0) before deploying to production at scale.
- macOS Friction: macOS endpoint deployment requires user-approved System Extensions and Full Disk Access, which can be disruptive if not pre-approved via MDM. Organizations without an MDM platform will face user interaction requirements during deployment.
Security Considerations
- Always enable tamper protection in EMS to prevent users from disabling FortiClient
- Ensure FortiGuard signature updates are verified as current; an AV agent with stale signatures provides a false sense of security
- Regularly review and audit scan exclusions — exclusions that were legitimate at deployment time may no longer be appropriate
- Consider enabling disk encryption enforcement as a compliance rule in EMS — FortiClient can verify BitLocker (Windows) or FileVault (macOS) status
Alternatives to FortiClient
FortiClient is an excellent solution within a Fortinet-centric environment, but it is not the only option. Here is a balanced comparison:
| Solution | Vendor | Best Suited For | Key Differentiator vs. FortiClient |
|---|---|---|---|
| Cisco AnyConnect / Secure Client | Cisco | Cisco-heavy enterprises | Deep integration with Cisco ISE and DNAC; mature VPN |
| Palo Alto GlobalProtect | Palo Alto Networks | Palo Alto NGFW environments | Tight NGFW integration; strong ZTNA via Prisma Access |
| Microsoft Defender for Endpoint | Microsoft | Microsoft 365 environments | Native M365/Entra integration; no added agent needed on Windows |
| CrowdStrike Falcon | CrowdStrike | Organizations prioritizing EDR/XDR | Industry-leading EDR; superior threat hunting; cloud-native |
| SentinelOne | SentinelOne | Autonomous response requirements | Strongest autonomous AI-driven response capabilities |
| Check Point Harmony Endpoint | Check Point | Check Point NGFW, users | Tight integration with the Check Point ecosystem |
When FortiClient Makes Sense vs. Alternatives
Choose FortiClient when:
- Your organization uses FortiGate firewalls and values Security Fabric integration
- You want to consolidate VPN, EPP, and ZTNA into a single agent
- You need a cost-effective, integrated endpoint solution within the Fortinet ecosystem
- You require cross-platform support from a single management console
Consider alternatives when:
- Your organization is heavily invested in a non-Fortinet network infrastructure (Cisco, Palo Alto)
- You need best-of-breed EDR/XDR capabilities, and Security Fabric integration is not a priority — CrowdStrike or SentinelOne would be stronger choices
- Your organization is entirely Microsoft 365/Azure-centric — Microsoft Defender for Endpoint offers deep native integration at potentially lower incremental cost
Conclusion & Best Practices
FortiClient in 2026 represents one of the most mature and feature-complete unified endpoint security agents available. Its strength lies not in any single feature but in how effectively it integrates with Fortinet’s Security Fabric — transforming each endpoint from an isolated security domain into an active, telemetry-reporting node in a coordinated defense system.
For organizations already operating a Fortinet environment, deploying FortiClient with EMS is a clear strategic choice. The integration depth, ZTNA capabilities, and consolidated management provide a compelling total cost-of-ownership advantage over assembling equivalent capabilities from multiple point solutions.
Best Practices
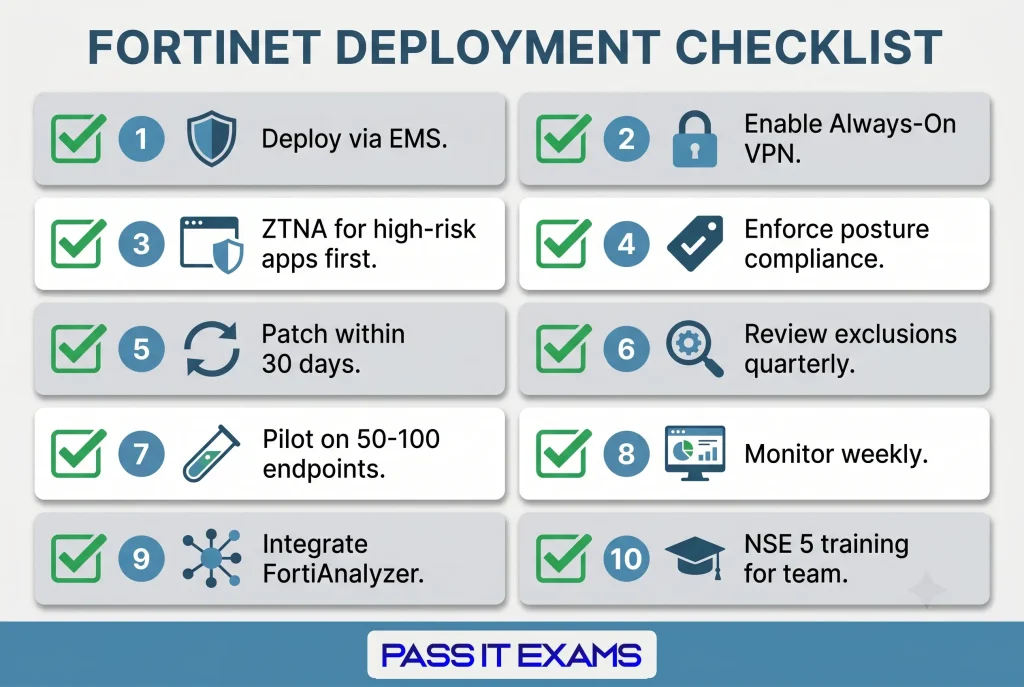
- Always deploy via EMS for any deployment beyond simple individual VPN use
- Enable Always-On VPN to eliminate unprotected network exposure windows
- Implement ZTNA progressively — start with your highest-risk applications before expanding to all apps
- Enforce device compliance via EMS posture tags and FortiGate dynamic policies
- Keep FortiClient and EMS updated — patch within 30 days of stable release; patch critical PSIRT advisories within 72 hours
- Review exclusions quarterly — exclusions are the most common source of AV evasion in enterprise environments
- Test before wide deployment — always pilot new FortiClient versions on 50–100 endpoints before organization-wide rollout
- Monitor EMS dashboards weekly — compliance drift happens gradually; early detection prevents breaches
- Integrate with FortiAnalyzer for cross-layer threat investigation capabilities
- Train your IT team — invest in Fortinet NSE (Network Security Expert) training, particularly NSE 5 for FortiClient EMS administration
Frequently Asked Questions
What is the difference between the free and paid versions of FortiClient?
The free version of FortiClient provides SSL VPN and IPsec VPN connectivity, basic ZTNA connection support, and two-factor authentication. It does not include endpoint protection (antivirus, anti-malware), advanced threat prevention, web filtering (full), application control, vulnerability scanning, or Security Fabric telemetry. The paid (licensed) version, managed via FortiClient EMS, unlocks the complete feature set. Licensing is per-endpoint, per-year, and must be purchased through Fortinet or an authorized partner. If you only need VPN functionality, the free version is suitable; for enterprise security, the licensed version is required.
Is FortiClient safe to install?
Yes, FortiClient downloaded from official Fortinet sources (fortinet.com or the Fortinet support portal) is safe. Fortinet is a publicly traded company (NASDAQ: FTNT) with a well-documented security track record. Like any security software, FortiClient requires significant OS-level permissions (System Extensions on macOS, kernel-level access on Windows) to perform its functions. These are expected and necessary. Ensure you download only from official sources and verify file hashes when possible.
How do I completely uninstall FortiClient?
Standard uninstallation via Windows Add/Remove Programs or macOS drag-to-trash may leave residual files, registry entries, and drivers. For a complete removal:
- Windows: Use the FortiClientTools utility (available from Fortinet’s support portal), which performs a clean removal of all drivers, registry keys, and configuration files. After running FortiClientTools, reboot before reinstalling.
- macOS: Use the uninstaller packaged with FortiClient (available in the Applications folder as “Uninstall FortiClient”). Alternatively, use the forticlient_uninstall command-line tool. A reboot is recommended after uninstallation.
- Linux: Use the package manager to install it (apt remove forticlient or rpm -e forticlient, depending on the distribution).
What is ZTNA, and how does it differ from a VPN?
VPN (Virtual Private Network) grants the authenticated user access to the entire corporate network segment to which they connect. Once inside, lateral movement to other systems is possible. ZTNA (Zero Trust Network Access) grants access only to the specific application the user is authorized to reach, based on continuous verification of identity, device posture, and context. ZTNA never places the user “on the network” — each application is individually proxied. This significantly limits the blast radius of credential compromise: a stolen password can only reach the applications that the user is explicitly authorized for, not the entire network.
What is FortiClient EMS, and do I need it?
FortiClient EMS (Endpoint Management Server) is Fortinet’s on-premises management server for FortiClient deployments. It provides centralized policy configuration, deployment automation, compliance monitoring, reporting, and Security Fabric integration. You need EMS if you have more than a handful of endpoints, need endpoint protection (EPP) features, want to enforce ZTNA with posture checks, or need compliance reporting. EMS is a Windows Server application with its own system requirements (a minimum of 4-core CPU, 8 GB of RAM, and 100 GB of disk space for up to 5,000 endpoints).
Does FortiClient impact system performance?
FortiClient does consume system resources, as any active endpoint security agent does. The impact is generally acceptable on modern hardware (over the last 3–5 years). Specific scenarios that may cause a noticeable impact include: intensive file I/O workloads (software compilation, large-file operations) where real-time scanning adds latency; older hardware with less than 4 GB of RAM; and laptop battery life (background scanning processes consume CPU cycles). Performance can be optimized through targeted scan exclusions, off-hours scheduling of full scans, and VPN split tunneling.
What ports does FortiClient use for VPN and EMS communication?
Key ports include:
- SSL VPN: TCP 443 (HTTPS), UDP 10443 (DTLS for performance)
- IPsec VPN: UDP 500 (IKE), UDP 4500 (NAT traversal), ESP (IP Protocol 50)
- EMS Communication: TCP 8013 (FortiClient to EMS), TCP 443 (EMS web console)
- FortiGuard Updates: TCP 443 and UDP 8888 to FortiGuard distribution network
Ensure these ports are open on any intermediate firewalls between endpoints and the respective servers.
Can FortiClient work with non-Fortinet firewalls?
The SSL VPN and IPsec VPN functionality of FortiClient is FortiGate-specific — it is designed to connect to FortiGate appliances and cannot be used as a generic VPN client for third-party VPN concentrators. The ZTNA functionality also requires a FortiGate access proxy. If you need to connect to a non-Fortinet VPN, you will need a different VPN client. However, FortiClient’s EPP features (antivirus, web filtering, vulnerability scanning) function independently of the VPN module and do not require FortiGate.
How does FortiClient handle FortiSandbox integration?
When FortiSandbox integration is enabled in EMS, FortiClient intercepts files being written to disk (downloads, email attachments, USB transfers) and submits unknown or suspicious files to FortiSandbox for dynamic analysis. FortiSandbox executes the file in a controlled environment, observes behavior, and returns a verdict (clean or malicious) to FortiClient, typically within seconds to minutes. If the file is malicious, FortiClient blocks it and generates an alert. FortiSandbox can be deployed on-premises (as a physical or virtual appliance) or consumed as a cloud service (FortiSandbox Cloud).
How do I update FortiClient?
- Standalone (free): FortiClient checks for updates automatically; new versions are available from the Fortinet website. You can trigger a manual update check within the FortiClient UI under Settings > Updates.
- EMS-managed: EMS administrators control update rollout. Administrators can configure automatic updates, staged rollouts (deploying to a test group first), or manual approval before deployment. EMS provides visibility into which endpoints are running which version.
- Signature updates (AV/IPS/web filter categories) are updated independently of the software version, typically every 4 hours by default via the FortiGuard distribution network.
What licensing is required for ZTNA?
FortiClient ZTNA requires the FortiClient ZTNA license (separate from the EPP license) and FortiClient EMS. Additionally, the FortiGate serving as the ZTNA access proxy must have an appropriate FortiGate license (included in standard FortiGate subscription). Some configurations also require a FortiGate-VM or a hardware FortiGate with adequate capacity for the expected number of concurrent ZTNA sessions. Consult Fortinet’s licensing team or your partner for exact SKU requirements.
Can FortiClient be deployed on Chromebooks?
Yes. Fortinet offers a FortiClient Chrome Extension for Chromebook deployments, available through the Google Workspace Admin console. This provides SSL VPN connectivity and basic web filtering. The Chrome extension has more limited capabilities compared to the full Windows or macOS agents — EPP features are not available. EMS can manage the Chrome extension deployment and basic policies.
What is the FortiClient log location for troubleshooting?
- Windows: C:\Program Files\Fortinet\FortiClient\logs\ — key files include FCLogs.log and event-specific logs
- macOS: /Library/Application Support/Fortinet/FortiClient/logs/
- Linux: /var/log/forticlient/
For VPN-specific troubleshooting, enable debug logging in the FortiClient VPN settings before reproducing the issue, then collect logs. For TAC cases, Fortinet support may request a full diagnostic bundle generated via FortiClientTools.
Is FortiClient FIPS-compliant?
FortiClient supports FIPS 140-2-validated cryptographic modules for VPN operations, which is relevant to U.S. federal government deployments requiring FIPS compliance. FIPS mode can be enabled in FortiClient and enforces FIPS-approved algorithms for all cryptographic operations. Check the documentation for the specific FortiClient version for the relevant FIPS certification status, as certifications are version-specific.
How do I configure FortiClient for a split-tunnel VPN?
Split tunneling in FortiClient VPN is configured on the FortiGate side, not on the FortiClient side. On FortiGate, under the SSL VPN portal configuration, administrators define which subnets are routed through the tunnel and which traffic exits locally. The FortiClient receives this routing configuration as part of the VPN session establishment. For EMS-managed deployments, VPN tunnel configuration is defined in the endpoint profile in EMS and pushed to all managed clients. Common split-tunnel configurations exclude Office 365, Google Workspace, and other cloud SaaS traffic from the VPN to reduce gateway bandwidth load.
