
FortiClient is one of the most widely deployed endpoint security solutions in enterprise environments worldwide. Whether your IT department requires it for a remote access VPN or you’re an administrator rolling it out across hundreds of machines, getting the installation right the first time saves hours of troubleshooting. This guide walks you through every method, on every major platform, so you can install FortiClient confidently and correctly.
What Is FortiClient?
FortiClient is Fortinet’s unified endpoint security agent. It combines several security capabilities into a single, lightweight client:
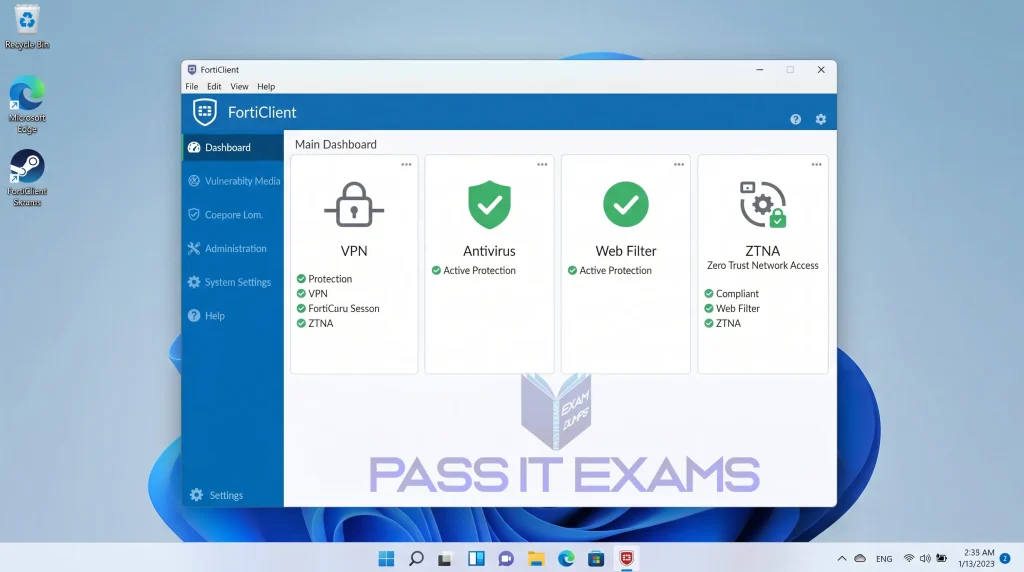
- SSL and IPsec VPN – Secure remote access to corporate networks via FortiGate firewalls
- Zero Trust Network Access (ZTNA) – Identity- and posture-based access control
- Endpoint Protection – Antivirus, anti-malware, and real-time threat detection
- Web Filtering – Category-based URL filtering enforced at the endpoint
- Application Firewall – Control and visibility over installed applications
- Vulnerability Scanning – Detection of unpatched software and OS weaknesses
Why Do Users Install It?
- Corporate requirement: IT departments deploy FortiClient so employees can VPN into company resources securely
- Remote work: Workers accessing internal systems from home or while traveling
- Compliance: Organizations requiring endpoint posture checks before granting network access
- Personal security: Home users who subscribe to Fortinet’s cloud-based security services
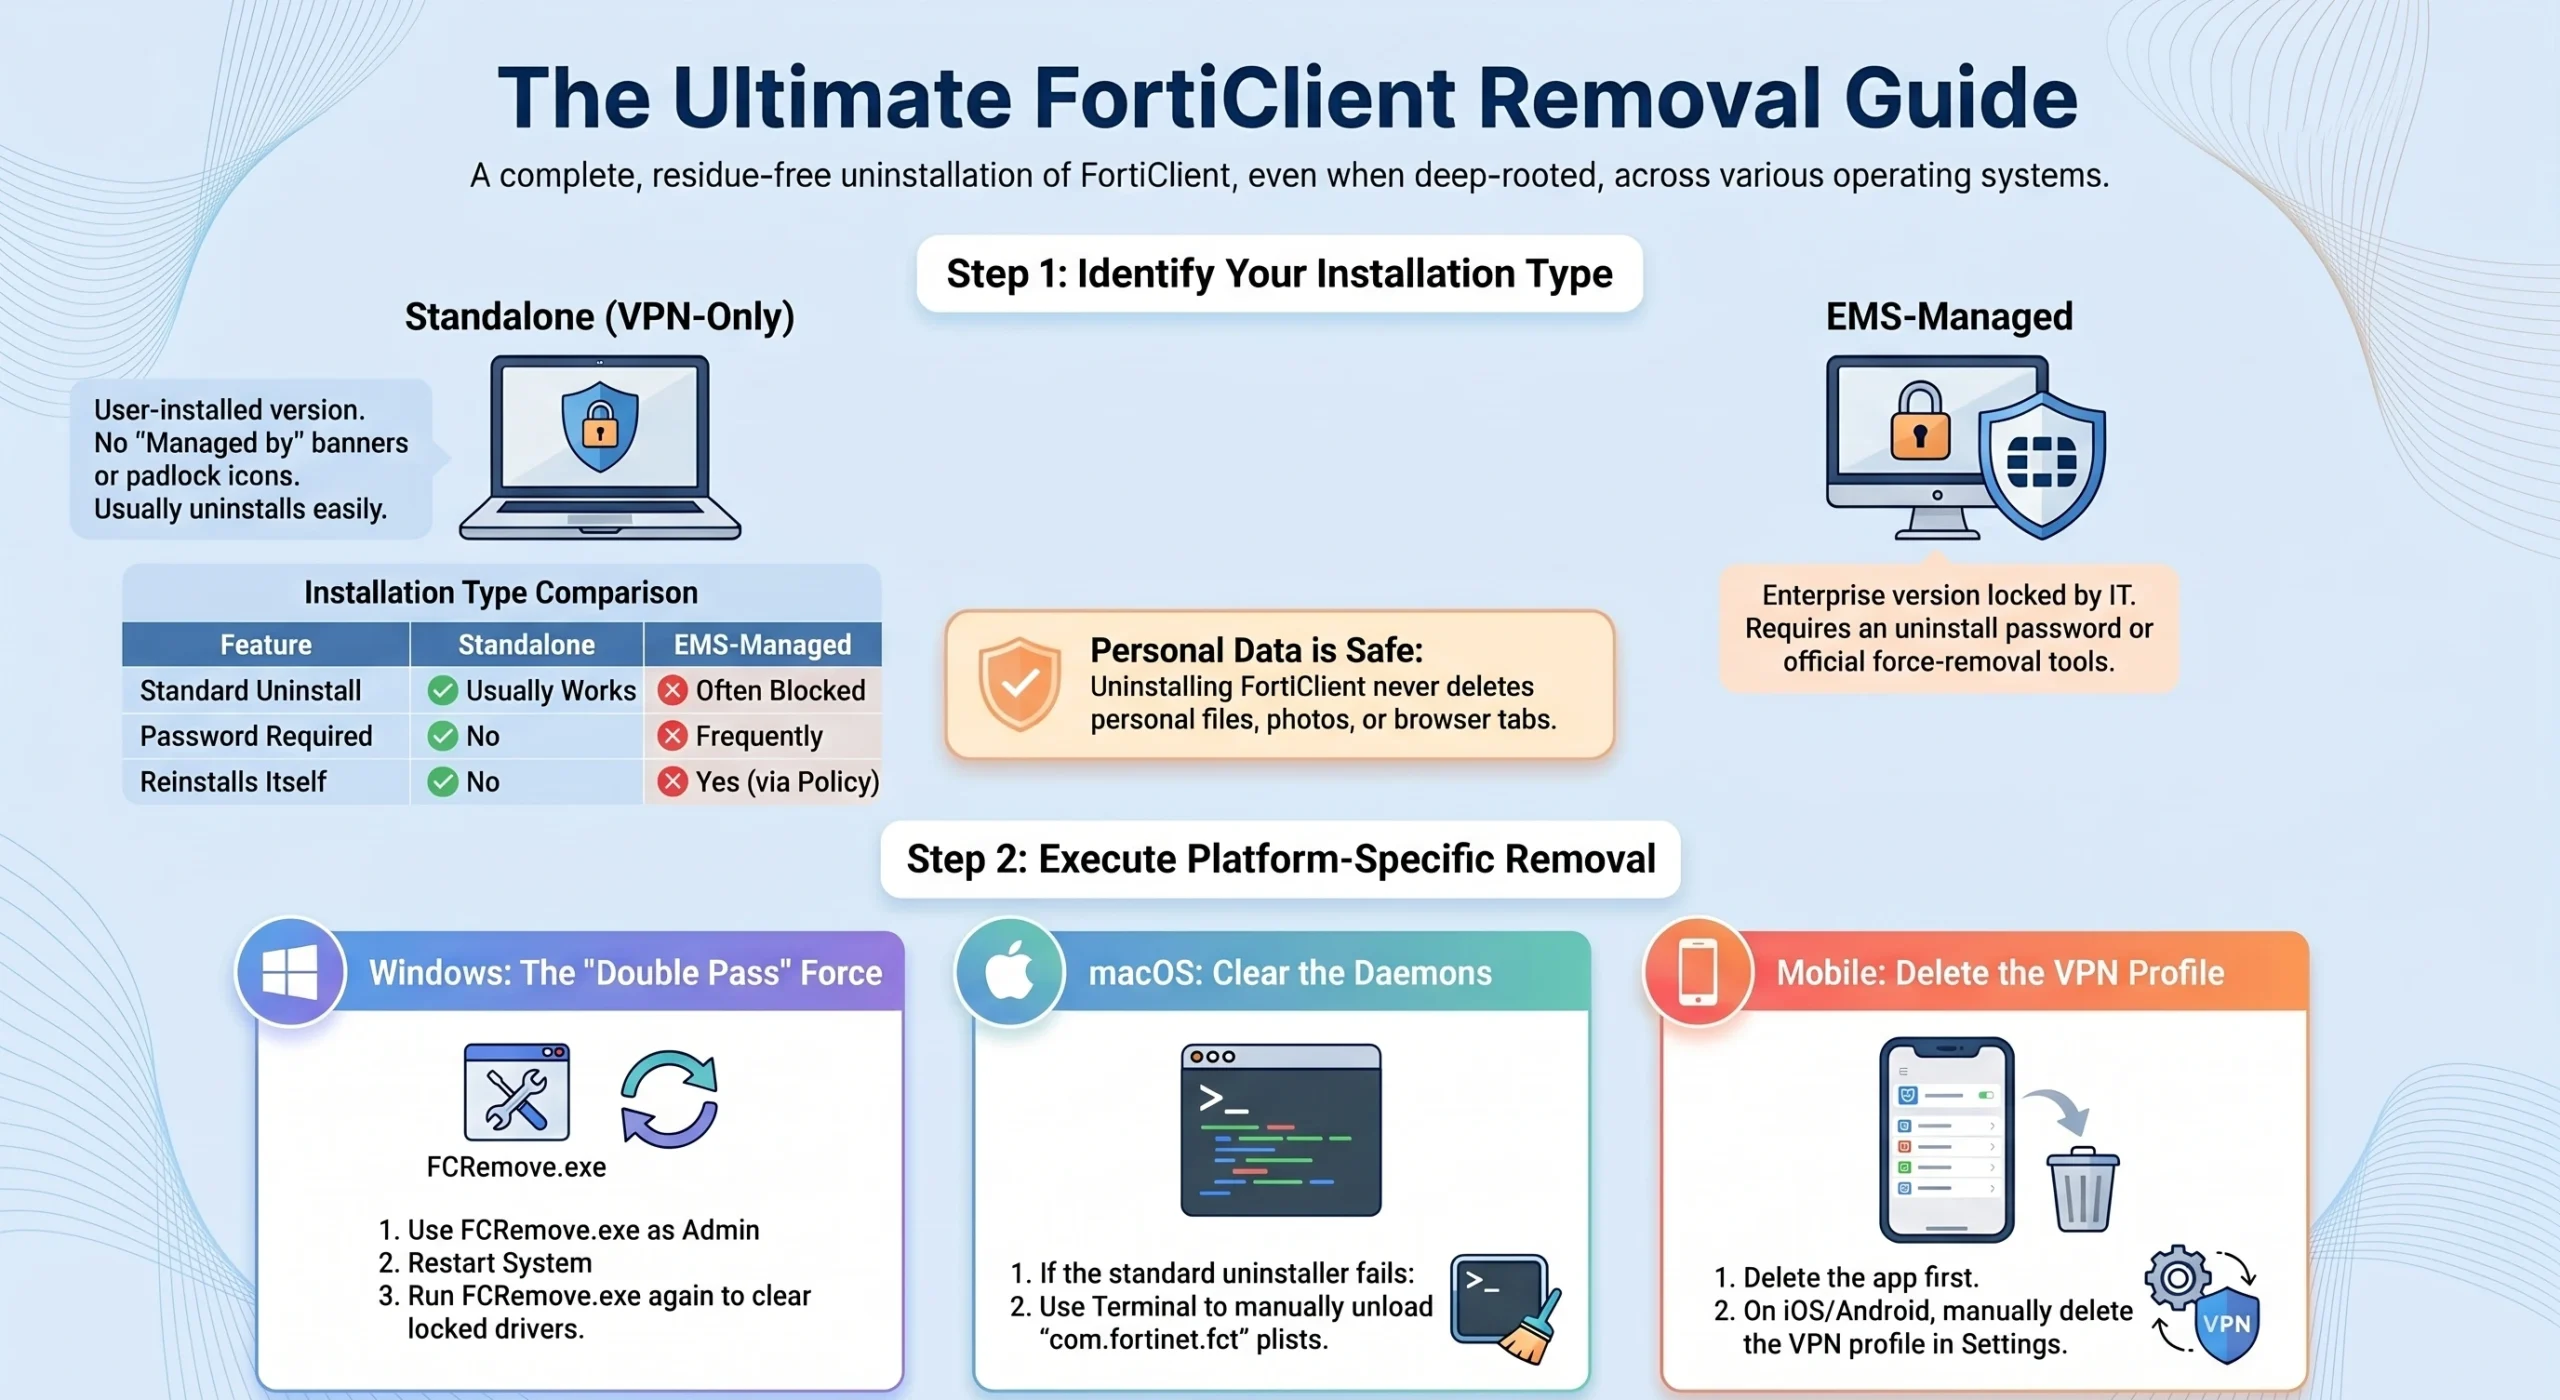
Struggling to remove FortiClient from your device? step-by-step uninstallation guide !
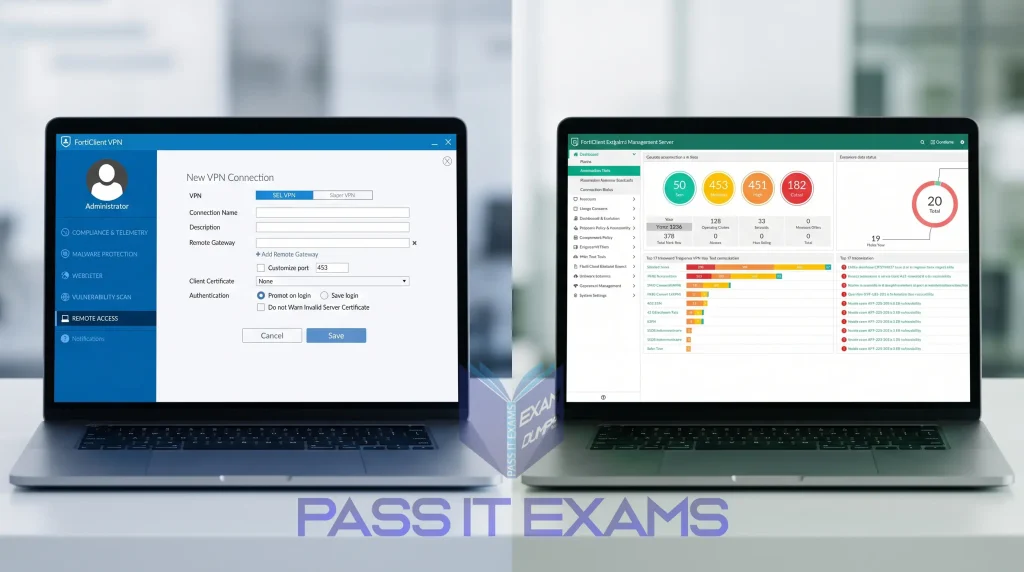
Standalone vs. EMS-Managed FortiClient
Understanding this distinction before you start is critical:
| Feature | Standalone (Free) | EMS-Managed |
|---|---|---|
| VPN connectivity | Full support | Full support |
| Antivirus / Web Filter | Not included | Included |
| Central management | Local only | Via FortiClient EMS |
| Policy enforcement | Manual | Automatic from EMS |
| ZTNA support | Limited | Full support |
| License required | Free | Requires an EMS license |
| Best for | Home users / VPN-only | Enterprises / IT admins |
The free standalone version is VPN-only. Full endpoint protection features (antivirus, web filtering, vulnerability scanning) require a FortiClient EMS (Endpoint Management Server) license and central management.
Prerequisites and Preparation
System Requirements
Before downloading anything, confirm your system meets the minimum requirements:
| Requirement | Windows | macOS | Linux |
|---|---|---|---|
| Supported OS versions | Windows 10 (64-bit), Windows 11, Windows Server 2016/2019/2022 | macOS 12 Monterey, 13 Ventura, 14 Sonoma, 15 Sequoia | Ubuntu 20.04/22.04/24.04, RHEL 7/8/9, CentOS 7/8 |
| RAM | 4 GB minimum (8 GB recommended) | 4 GB minimum | 2 GB minimum |
| Disk space | 600 MB free | 600 MB free | 400 MB free |
| Architecture | 64-bit only | Apple Silicon (M-series) & Intel | 64-bit only |
| Admin rights | Required | Required | Required (sudo) |
| Internet | Required during install | Required during install | Required for packages |
Note on FortiClient 7.x: Fortinet’s current major release line is FortiClient 7.x (7.2 and 7.4 as of 2026). Always match your FortiClient version to your organization’s FortiGate or EMS server version. Mismatched versions can cause connection failures.
Where to Safely Download FortiClient
⚠️ WARNING: Only download FortiClient from Fortinet’s official website. Third-party sites distributing “FortiClient” installers have been documented as distributing malware. There is no legitimate reason to download it anywhere else.
Official download locations:
- FortiClient VPN (free standalone): https://www.fortinet.com/support/product-downloads
- Full FortiClient (licensed): Requires login to the Fortinet Support Portal at https://support.fortinet.com
- Enterprise deployments: Your IT administrator will typically provide an EMS enrollment link or a pre-packaged installer
Navigate to Product Downloads → FortiClient and select your operating system. Choose the correct version that matches your organization’s or FortiGate gateway’s requirements.
Pre-Installation Checklist
Before running the installer:
- Temporarily disable other VPN clients (Cisco AnyConnect, GlobalProtect, OpenVPN, etc.) , running two VPN agents simultaneously causes driver conflicts
- Temporarily disable third-party antivirus (Norton, McAfee, Malwarebytes, etc.) until FortiClient finishes installing, then re-enable
- Close all running applications, especially browsers and Outlook
- Ensure you have administrator privileges on the machine
- Verify your internet connection is stable , the installer September need to download additional components
- Note your FortiGate/VPN server address if you plan to configure VPN immediately after install
Installing FortiClient on Windows
Standalone VPN-Only Installation (Most Common for Home Users)
Here’s the easiest path most users succeed with:
- Download the installer. Go to https://www.fortinet.com/support/product-downloads, select FortiClient VPN, choose Windows, and download the .exe installer.
- Run the installer as Administrator. Right-click the downloaded .exe file → Run as administrator. Click Yes on the UAC prompt.
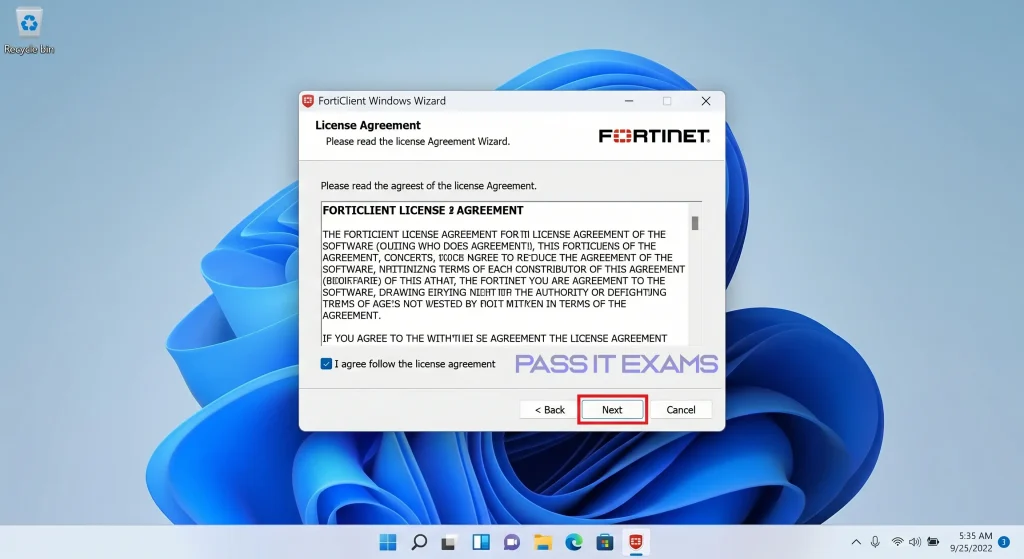
- Accept the License Agreement. Read and accept the End User License Agreement, then click Next.
- Choose installation type
- Select VPN only for the free standalone version
- If your IT team provided a full installer, you September see additional feature checkboxes (Antivirus, Web Filter, etc.)
- Select installation directory. The default path is C:\Program Files\Fortinet\FortiClient. Unless you have a specific reason to change it, leave this as-is.
- Click Install. The installer will copy files, install drivers (including the VPN adapter), and register services. This typically takes 2–5 minutes.
- Restart your computer when prompted. FortiClient installs kernel-level drivers that require a reboot to activate properly. Do not skip this step.
- Launch FortiClient. After the restart, FortiClient will appear in the system tray and on your desktop. Open it and proceed to post-installation setup.
Silent / Command-Line Installation (For IT Admins)
For mass deployment via Group Policy, SCCM, Intune, or scripts, use the MSI package (download from the Fortinet Support Portal) with msiexec:
Basic silent install
msiexec /i FortiClientSetup_7.4.x.msi /quiet /norestart
Silent install with logging
msiexec /i FortiClientSetup_7.4.x.msi /quiet /norestart /log C:\Logs\forticlient_install.log
Silent install with feature selection (VPN only)
msiexec /i FortiClientSetup_7.4.x.msi /quiet /norestart ADDLOCAL=”vpn”
Silent install with all features
msiexec /i FortiClientSetup_7.4.x.msi /quiet /norestart ADDLOCAL=”ALL”
msiexec /x FortiClientSetup_7.4.x.msi /quiet /norestart
Useful MSI switches:
| Switch | Description |
|---|---|
| /quiet | Silent install, no UI |
| /norestart | Suppress automatic reboot |
| /log <path> | Write the install log to the specified path |
| ADDLOCAL=”vpn” | Install the VPN component only |
| ADDLOCAL=”ALL” | Install all available components |
| REBOOT=ReallySuppress | Forcefully prevent reboot (use with caution) |
Tip: Always test your silent install command on a single machine before deploying to your fleet. Check the install log for any errors
Custom Installation , Feature Selection
When running the full (non-VPN-only) installer, you September be presented with component options:
- VPN – Required for all remote access
- Endpoint Detection & Response (EDR) – Advanced threat hunting
- Anti-Malware / Antivirus – Real-time file scanning
- Web Filter – Browser-level URL filtering
- Application Firewall – Network traffic control
- Vulnerability Scan – Scheduled patch gap detection
- Single Sign-On – SAML/AD integration
Select only what you need. Unnecessary components add memory footprint and startup time.
Installing FortiClient on macOS
macOS installations have additional permission steps that trip up many users. Follow these carefully.

Step-by-Step macOS Installation
- Download the DMG installer. Go to the official Fortinet downloads page, select macOS, and download the .dmg file.
- Open the DMG and run the installer. Double-click the .dmg to mount it, then double-click the .pkg installer inside.
- Authenticate with your admin password. macOS will prompt for your administrator credentials. Enter them and click Install Software.
- Allow the System Extension (CRITICAL STEP). During or after installation, you will see a notification:
“System Extension Blocked , A program tried to load a new system extension.”- Open System Settings → Privacy & Security
- Scroll to the Security section
- Click Allow next to the Fortinet message
- You September need to authenticate again with Touch ID or your password
- Open System Settings → Privacy & Security
- ⚠️ Without allowing the system extension, FortiClient VPN will not function. This is the #1 cause of VPN failure on macOS.
- Grant VPN Configuration permission. When FortiClient first launches, macOS will ask:
“FortiClient would like to add VPN configurations.”
Click Allow. - Grant Full Disk Access (if required by your org). For full antivirus functionality (EMS-managed only):
- Go to System Settings → Privacy & Security → Full Disk Access
- Click the + button and add FortiClient from your Applications folder
- Restart your Mac. A restart ensures all kernel extensions and system modifications take effect.
- Verify the installation. Open FortiClient from your Applications folder. The dashboard should load without errors.
macOS-Specific Troubleshooting
- Problem: VPN connects, but traffic doesn’t route correctly. Fix: Check System Settings → VPN , ensure FortiClient’s VPN profile is listed and active
- Problem: “System Extension Blocked” keeps reappearing. Fix: If you’re on Apple Silicon (M1/M2/M3), ensure you’re running the Universal or ARM-native build of FortiClient, not an Intel-only (Rosetta) version
- Problem: FortiClient crashes on launch after macOS upgrade. Fix: Reinstall FortiClient after major macOS updates. System extension signatures change between major OS versions.
Installing FortiClient on Linux
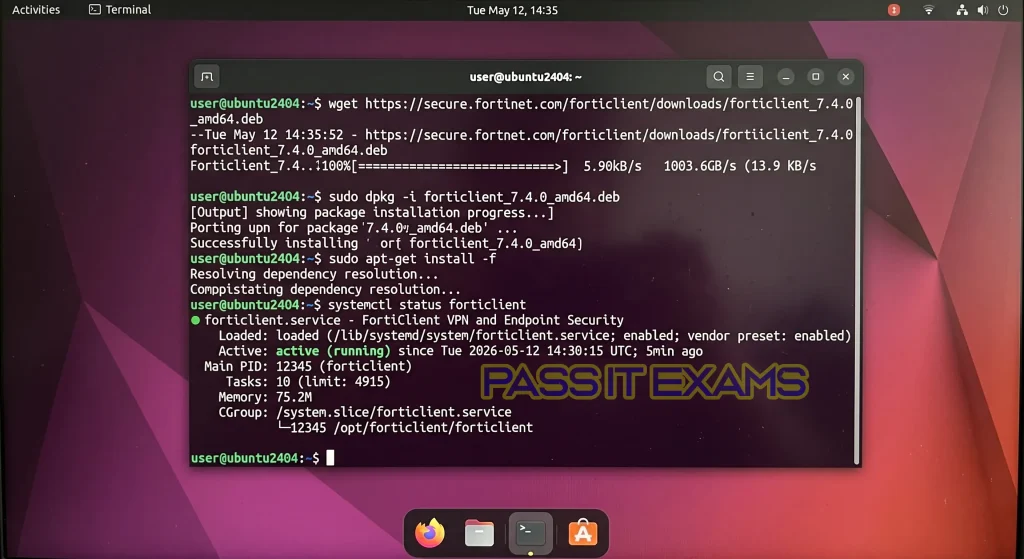
Linux installation is package-based. Fortinet provides .deb packages for Debian/Ubuntu systems and .rpm packages for Red Hat/CentOS/RHEL/Fedora systems.
Supported Distributions (FortiClient 7.x)
- Ubuntu 20.04 LTS, 22.04 LTS, 24.04 LTS
- Debian 10, 11, 12
- Red Hat Enterprise Linux 7, 8, 9
- CentOS 7, 8
- Fedora (select versions , check release notes)
Installation on Ubuntu/Debian (DEB)
# Step 1: Download the .deb package from Fortinet Support Portal
# (Replace filename with your downloaded version)
# Step 2: Install the package
sudo dpkg -i forticlient_7.4.x_amd64.deb
# Step 3: If dependency errors appear, fix them
sudo apt-get install -f
# Step 4: Start the FortiClient service
sudo systemctl start forticlient
# Step 5: Enable FortiClient to start on boot
sudo systemctl enable forticlient
# Step 6: Verify the service is running
sudo systemctl status forticlient
Installation on RHEL/CentOS/Fedora (RPM)
# Step 1: Download the .rpm package from Fortinet Support Portal
# Step 2: Install the package
sudo rpm -ivh forticlient_7.4.x.x86_64.rpm
# Alternative using dnf (RHEL 8+/Fedora)
sudo dnf install forticlient_7.4.x.x86_64.rpm
# Step 3: Start the FortiClient service
sudo systemctl start forticlient
# Step 4: Enable on boot
sudo systemctl enable forticlient
# Step 5: Check status
sudo systemctl status forticlient
Post-Install Linux Setup
Once the service is running, launch the FortiClient GUI:
# Launch GUI (if installed)
forticlient
# Or via application menu in GNOME/KDE
CLI-only VPN connection (useful for headless servers):
# Connect to VPN
sudo forticlientsslvpn/64bit/forticlientsslvpn –server vpn.yourcompany.com:443 –vpnuser yourusername
# You’ll be prompted for your password
Note: The Linux version of FortiClient focuses primarily on VPN and ZTNA. Full endpoint protection (antivirus and web filter) is available only on Windows and macOS clients.
EMS-Managed (Enterprise) Deployment
If your organization uses FortiClient EMS (Endpoint Management Server), your installation experience differs from that of the standalone path.
How EMS Enrollment Works
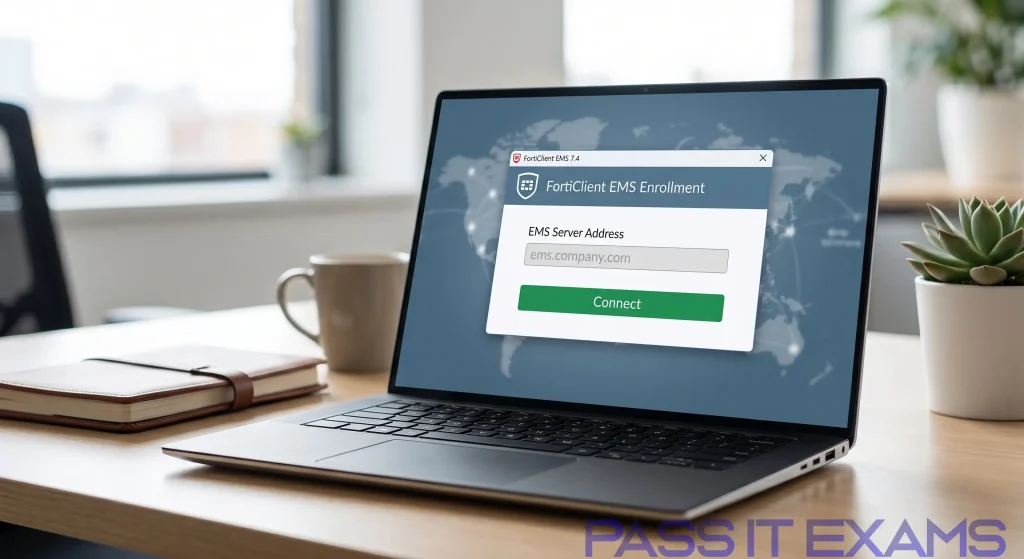
- Your IT admin provides an enrollment URL , typically something like https://ems.yourcompany.com or a one-time invitation link
- Install FortiClient using any method above (standard installer, silent MSI, or pre-packaged EMS installer)
- Open FortiClient and click Zero Trust Telemetry or Connect to EMS (wording varies by version)
- Enter the EMS server address or invitation code provided by IT
- FortiClient registers with EMS and automatically downloads your organization’s security profile, VPN configurations, and policies
What Changes Under EMS Management
- VPN profiles are auto-deployed , you won’t manually type server addresses
- Policies are enforced , your IT team can lock settings so users can’t disable protection
- Compliance checks run automatically , if your device fails a posture check, access September be restricted
- Updates are centrally managed , your admin can push FortiClient updates without user action
- Telemetry is sent to EMS , your organization has visibility into your endpoint’s security posture
⚠️ Corporate policy reminder: If you’re using a company-issued device, only install FortiClient if your IT department instructs you to. Do not enroll a personal device in a corporate EMS without understanding the data access implications.
Post-Installation Setup and Verification
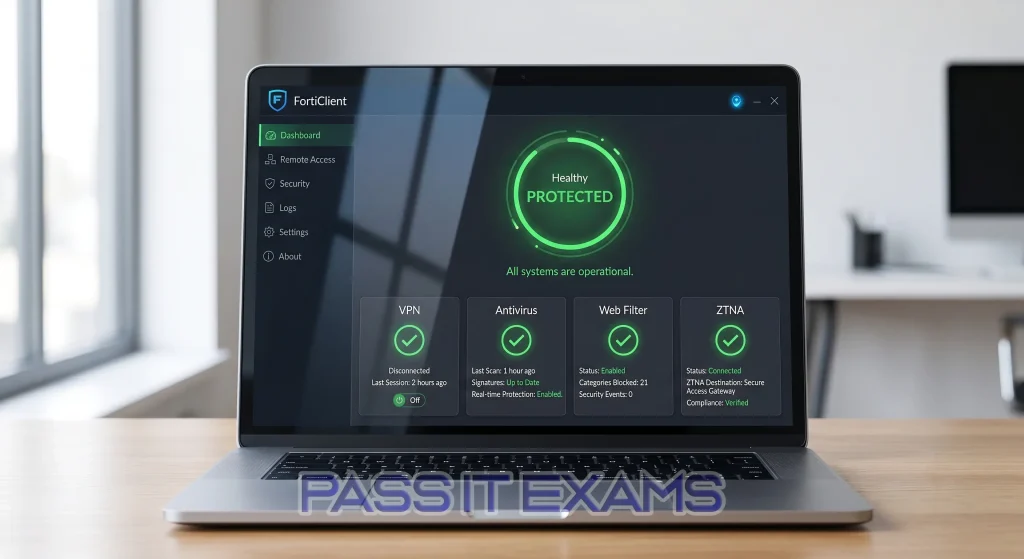
First-Time Launch
- Open FortiClient from the Start Menu, dock, or Applications folder
- Accept any additional prompts for telemetry or usage data (optional)
- The dashboard will show your security status , green indicators mean the installation is healthy
Connecting to VPN
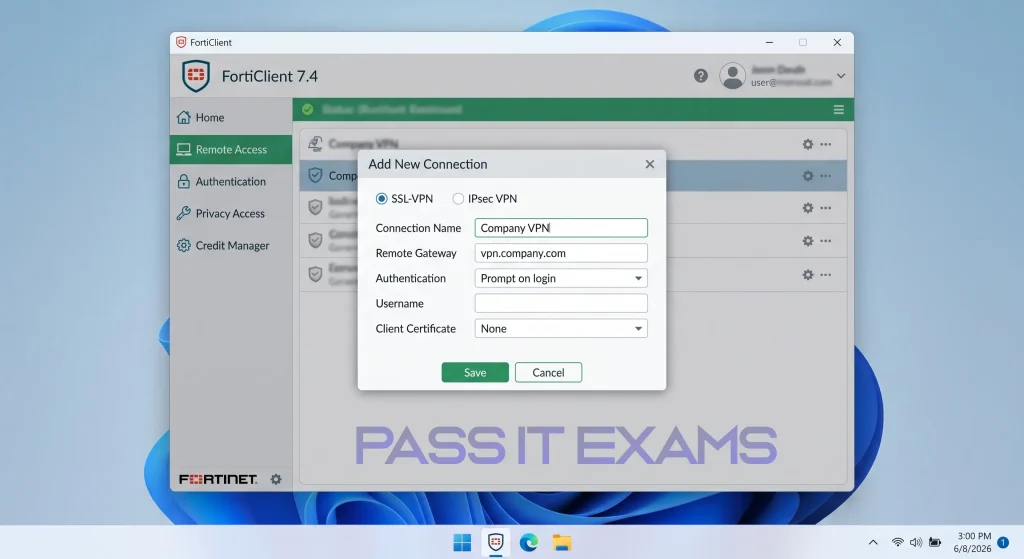
For standalone (manual) VPN setup:
- Click the Remote Access tab in FortiClient
- Click the + icon to add a new VPN connection
- Choose SSL-VPN or IPsec VPN (ask your IT team which type you need)
- Enter the Remote Gateway (your VPN server address, e.g., vpn.yourcompany.com)
- Enter your username , leave the password field blank if your org uses multi-factor authentication
- Click Save, then Connect
- Enter your password and complete MFA if prompted
Verifying the Installation is Successful
- The FortiClient dashboard shows a green/healthy status for all enabled modules
- VPN connects without errors, and you can access internal resources
- System tray/menu bar icon is present (shield icon)
- On Windows: Open Services (services.msc) and confirm FortiClient Service is running
- On macOS: Check System Settings → VPN , FortiClient profile appears
- On Linux: sudo systemctl status forticlient shows active (running)
Updating FortiClient
Windows/macOS: FortiClient will notify you of updates via the dashboard. Click Update when available. For EMS-managed deployments, updates September be pushed automatically.
Linux:
# Ubuntu/Debian , download new .deb and reinstall
sudo dpkg -i forticlient_7.4.x_amd64.deb
# RHEL/CentOS , download new .rpm and upgrade
sudo rpm -Uvh forticlient_7.4.x.x86_64.rpm
Troubleshooting Common Installation Problems
Problem: Installer Fails or Gets Stuck
Symptoms: Progress bar freezes, installer exits with error code, or shows “Installation failed.”
Solutions:
- Run the installer as Administrator (right-click → Run as administrator)
- Disable antivirus temporarily during installation
- Check for a previous failed FortiClient install: run the FortiClient Cleanup Tool (available from Fortinet Support Portal) before reinstalling
- Check Windows Event Viewer → Application logs for the specific error code
Problem: “Insufficient Privileges” Error
Symptoms: Error message about permissions or admin rights
Solutions:
- Confirm your Windows account is in the local Administrators group
- If on a corporate machine where you lack admin rights, contact your IT helpdesk , they’ll need to install it for you or push it via management tools
Problem: Conflicts With Other VPN or Security Software
Symptoms: Installation completes, but VPN fails to connect; network adapter errors; BSOD (rarely)
Solutions:
- Uninstall competing VPN clients before installing FortiClient: Cisco AnyConnect, Palo Alto GlobalProtect, Pulse Secure, OpenVPN TAP adapter
- On Windows, check Device Manager for yellow exclamation marks on network adapters
- Remove orphaned VPN TAP adapters: open Device Manager → View → Show Hidden Devices → Network Adapters → uninstall any TAP-Windows Adapter
Problem: macOS “System Extension Blocked” Cannot Be Cleared
Symptoms: The Allow button is greyed out, or clicking Allow does nothing
Solutions:
- On Apple Silicon Macs enrolled in MDM, system extensions require IT admin approval
- Contact your IT admin , they need to allow Fortinet’s extension via MDM (Jamf, Intune, etc.)
- If on a personal Mac: reboot into Recovery Mode and adjust the security policy to allow kernel extensions from identified developers
Problem: FortiClient Service Fails to Start on Linux
Symptoms: systemctl status forticlient shows a failed or stopped state
Solutions:
# Check detailed error logs
journalctl -u forticlient -n 50
# Verify required dependencies
sudo apt-get install libglib2.0-0 libgtk-3-0 libwebkit2gtk-4.0-37
# Reinstall cleanly
sudo dpkg –purge forticlient
sudo dpkg -i forticlient_7.4.x_amd64.deb
Problem: VPN Connects, but No Traffic Flows
Symptoms: VPN shows “Connected,” but internal websites or resources are unreachable
Solutions:
- Check your split tunneling configuration , your VPN September only route corporate traffic
- Confirm DNS is resolving internal names: nslookup internal-server.company.com
- On macOS: ensure the VPN profile has “Send all traffic over VPN” enabled (or the correct setting per your admin’s instructions)
- Try disabling any local firewall software temporarily to isolate the issue
Advanced Tips for IT Administrators
Pre-Configured Silent Deployment with EMS Auto-Enrollment
Create a deployment package that silently installs FortiClient and auto-enrolls to EMS:
msiexec /i FortiClientSetup_7.4.x.msi /quiet /norestart ^
FORTICLIENTEMS_SERVER=”ems.yourcompany.com” ^
FORTICLIENTEMS_PORT=”8013″ ^
/log “C:\Logs\fc_install.log”
The EMS enrollment token can also be embedded in a forticlient.xml configuration file and bundled with the installer for zero-touch provisioning.
Customizing the Installer with the FortiClient Configurator Tool
Fortinet provides the FortiClient Configurator Tool (Windows-only, free from the Support Portal) that lets you:
- Pre-configure VPN connection profiles (server addresses, usernames, tunnel type)
- Pre-set feature selection (enable/disable specific modules)
- Embed a license key or EMS enrollment token
- Generate a custom .msi that deploys with your settings baked in
This is the recommended method for enterprise rollouts where you want to minimize user interaction.
Best Practices for Enterprise Rollouts
- Version control: Standardize on a single FortiClient version across your fleet. Use EMS to enforce minimum version requirements.
- Staged deployment: Roll out to a pilot group of 10–20 users before deploying to all endpoints.
- Test compatibility: Before any major OS upgrade (e.g., Windows 10 to 11, or macOS version bump), test your current FortiClient version in a lab environment.
- Document your VPN profiles: Keep a record of all VPN server addresses, authentication methods, and tunnel modes used in your organization.
- Use EMS compliance rules: Configure posture checks (OS version, patch level, disk encryption status) to automatically enforce security standards.
Conclusion
FortiClient is a reliable, enterprise-grade endpoint agent when installed correctly. Here’s a quick summary of the best approach for each scenario:
- Home user / VPN-only: Download the free VPN-only installer from Fortinet’s official site, run as administrator, reboot, and configure your VPN profile manually.
- macOS user: Follow the exact same steps, but pay special attention to allowing the system extension in Privacy & Security , this is the single most common failure point.
- Linux user: Use the .deb or .rpm package matching your distribution, install via the package manager, and start the FortiClient service.
- IT administrator: Use the MSI with silent switches for automated deployment. Consider the FortiClient Configurator Tool for pre-built, customized installers.
- Enterprise (EMS): Enroll devices using the EMS server address or invitation token after installation. Let EMS handle policy and centrally update management.
If you continue to experience issues after following this guide, contact your organization’s IT helpdesk or reach Fortinet’s official support.
Frequently Asked Questions
Can I install FortiClient without admin rights?
No. FortiClient installs kernel-level VPN drivers and system services that require administrator (Windows) or sudo (Linux/macOS) privileges. If you’re on a managed corporate device without admin rights, ask your IT team to deploy it for you.
What is the difference between the standalone and EMS-managed versions of FortiClient?
The standalone (free) version provides VPN connectivity only , no antivirus, web filter, or central management. EMS-managed FortiClient includes full endpoint protection features and is centrally configured and monitored by your IT team via FortiClient EMS.
How do I reinstall FortiClient?
Uninstall the existing version first: go to Settings → Apps (Windows) or drag to Trash (macOS), then download a fresh installer from Fortinet’s official site and follow the installation steps. On Windows, run the FortiClient Cleanup Tool from the Fortinet Support Portal if a standard uninstall leaves residual files.
Is FortiClient safe to install?
Yes , when downloaded from the official Fortinet website only. FortiClient is a well-established enterprise security product. Never download it from third-party sites, file-sharing platforms, or unofficial mirrors.
How do I uninstall FortiClient?
Windows: Settings → Apps → FortiClient → Uninstall (or use msiexec /x for silent uninstall). macOS: Drag FortiClient from Applications to Trash, then remove residual files from ~/Library and /Library. Linux: sudo dpkg –purge forticlient (Debian/Ubuntu) or sudo rpm -e forticlient (RHEL/CentOS). After uninstalling, remove any leftover VPN profiles from System Settings.
Which version of FortiClient should I install?
Install the version that matches your organization’s FortiGate firmware or EMS server version. Your IT team will specify this. If you’re a standalone user, install the latest 7.x release. Check the Fortinet compatibility matrix for version pairing requirements.
Can FortiClient run on Apple Silicon (M1/M2/M3)?
Yes. FortiClient 7.2 and later include native Apple Silicon support. Older versions September run under Rosetta 2, but for best performance and stability, use the Universal or Apple Silicon-native build.
Why does FortiClient show as “unregistered” or “unlicensed”?
The free standalone version is unlicensed by design , it only supports VPN. If your organization requires full features (antivirus, web filter, etc.), your IT team needs to connect the client to a FortiClient EMS server with a valid license.
Can I run FortiClient alongside other security software?
FortiClient can coexist with Windows Defender (Microsoft’s built-in AV). However, running two third-party antivirus products simultaneously is not supported and will cause conflicts. Disable or uninstall conflicting third-party AV before installing FortiClient’s antivirus module.
What should I do if my VPN worked before but stopped connecting after a Windows or macOS update?
Operating system updates sometimes break VPN drivers or system extensions. First, check if a newer version of FortiClient is available , Fortinet typically releases compatibility updates alongside major OS releases. If no update is available, try reinstalling your current FortiClient version to repair the drivers.
