
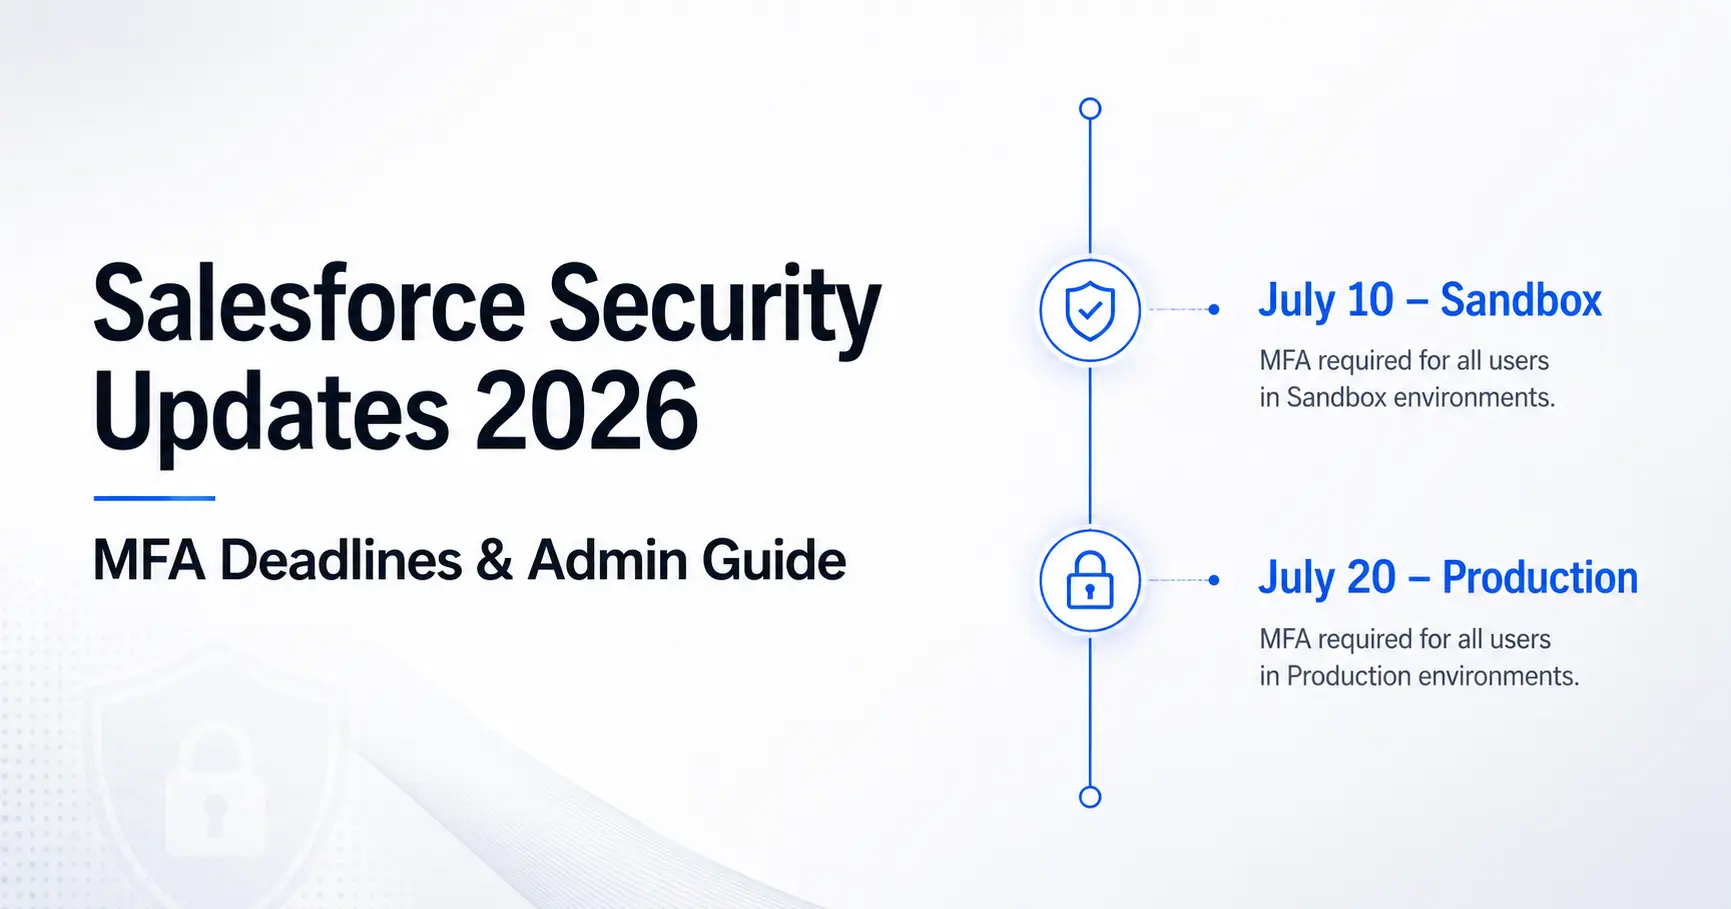
Salesforce security updates 2026 enforce multi-factor authentication for all employee users and phishing-resistant MFA for privileged users. Sandbox enforcement began July 10, 2026; production starts July 20, 2026 (staggered by release group). Additional controls cover email domain verification, step-up authentication on reports, and Transaction Security Policy enhancements. This article lists every control and exact date from the official Salesforce security roadmap, explains the July 10 revision, and gives admins a prioritized checklist to prevent lockouts.
Who is affected: All Salesforce orgs. Admins and privileged users face the strictest requirements; every internal user must complete MFA.
Key Security Controls & Exact Timelines
The official Salesforce security roadmap lists these controls with their published timelines. Many are staggered by release group, consult the linked Prepare articles for your org’s specific dates.
| Security Control | Sandbox Timeline | Production Timeline | Status/Notes |
|---|---|---|---|
| Email Domain Verification – Phase 1 (New & Existing Domains) | March 24 – April 25, 2026 | May 5 – June 1, 2026 | Required to send email |
| Email Domain Verification – Phase 2 (Allowlisted Domains) | June 29 – July 27, 2026 | June 29 – July 27, 2026 | Enforcement phase |
| Preventing Connections from Anonymizing VPNs, Proxies and High-Risk IP Addresses | Applied starting April 24, 2026 (Connected App or API usage) | Applied starting April 24, 2026 | Already in effect |
| Extended Login Anomaly Detections and Containment | Early April 2026 | Early April 2026 | Already applied |
| Step-up Auth for Report Activities (Time-Based Session Level Policy) | Available: starting May 27, 2026 (staggered ≈7 days); Enforced: starting June 17, 2026 (staggered ≈7 days) | Available: starting May 27, 2026 (staggered ≈15 days); Enforced: starting July 1, 2026 (staggered ≈30 days) | Applies to report actions |
| Transaction Security Policy Enhancements | Available: starting June 1, 2026; Enforced: starting June 22, 2026 | Available: starting June 15, 2026; Enforced: starting July 13, 2026 | See Prepare article for details |
| Step-up Authentication for Anomalous Behavior | June 29, 2026 | July 13, 2026 | Anomalous report export detection |
| Phishing-Resistant MFA Enforcement for Privileged Users, Including Admins | Starting July 10, 2026 | Starting July 20, 2026 | Refer to Release Group Enforcement Schedule in the Prepare article |
| MFA Enforcement for All Employee Users | Starting July 10, 2026 | Starting July 20, 2026 | Refer to Release Group Enforcement Schedule in the Prepare article |
These dates are taken directly from the July 10, 2026 revision of the official roadmap.
See also: Email Domain Verification release note
What Changed in the Latest Update (July 10, 2026)
On July 10, 2026, Salesforce revised the security roadmap with an important adjustment to sandbox enforcement for two controls:
- Phishing-Resistant MFA Enforcement for Privileged Users, Including Admins
- MFA Enforcement for All Employee Users
Sandbox enforcement for the Sandbox [Preview] Release Group moved to July 10, 2026 (from the prior July 6–8 window). The change followed reports that some users could not log in after MFA was applied. Salesforce stated that the “Create a Passkey” prompts were expected behavior under the improved passkey registration experience and were not a product defect.
Earlier change-log entries note a temporary hold on July 1, 2026, followed by a resumption announcement on July 2 that set production enforcement to begin July 20, 2026 (staggered). The July 10 update also confirmed that detailed Release Group Enforcement Schedules now appear in the respective Prepare knowledge articles.
All other controls retained their previously published dates. The roadmap remains a living document focused on reducing risk from phishing, data exfiltration, and account takeover.
Impact on End Users (Non-Admins)
Starting in summer 2026, non-admin users encounter two main changes drawn from the official article:
Multi-factor authentication (MFA) is required to log in.
MFA requires a second verification method in addition to username and password.
- Users logging in directly without a registered method are prompted to register one after login.
- Users logging in via single sign-on (SSO) should contact their admin; Salesforce may still require its own verification step.
- Preparation: Register an MFA verification method and confirm permitted methods with an admin.
Step-up authentication is required for report actions.
Step-up authentication is an extra identity check for sensitive actions such as viewing or exporting reports.
- Salesforce may prompt the user to re-verify even after a recent login.
- SSO users who completed MFA at the identity provider cannot automatically reuse a non-Salesforce method for step-up; a Salesforce method or a phone/email code is needed.
- Preparation: Register an MFA method and keep phone number and email address current.
These requirements protect accounts and company data. Most standard users can use either phishing-resistant or standard verification methods.
Action Checklist for Salesforce Admins
Prioritized by urgency and outcome. Complete the highest-priority items first to prevent lockouts.
Immediate – Prevent Privileged-User Lockouts
- Identify all users who will be subject to phishing-resistant MFA (see Expert Admin Notes below for criteria).
- Confirm that Identity Verification settings allow built-in authenticators and/or physical security keys.
- Ensure privileged users have registered at least one phishing-resistant method.
- For SSO environments, verify that the identity provider transmits supported authentication signals.
Before July 20, 2026 – Complete Production Readiness
- Test login and report-export flows in a sandbox that has already received July 10 enforcement.
- Communicate the exact production start date for your release group to all affected users and supply registration steps.
- Confirm phone numbers and email addresses are accurate for users who may need verification codes for step-up authentication.
- Review Transaction Security Policy behavior if your org uses Shield or Event Monitoring.
Ongoing – Maintain Compliance
- Monitor Salesforce Help for further revisions to the roadmap and Release Group schedules.
- Include phishing-resistant MFA registration in the onboarding process for any new privileged users.
- Re-audit elevated permissions periodically.
- Bookmark the official roadmap article; treat it as a living resource.
Admins planning beyond the 2026 security changes should also review the upcoming Salesforce 2027 certification retirements and their impact on certification paths.
Expert Admin Notes (Additional Guidance Beyond the Core Roadmap)
These practical details are widely referenced in Salesforce Help and admin guidance but are not listed inside the primary roadmap table itself:
- Privileged users typically include those with the System Administrator profile or the permissions Modify All Data, View All Data, Customize Application, or Author Apex.
- The “Waive Multi-Factor Authentication for Exempt Users” permission no longer exempts interactive logins after enforcement; legitimate cases require a Support request.
- In Setup → Identity Verification, enable the built-in authenticator and security-key options; optionally turn on passwordless login with passkeys.
- For SSO, confirm the identity provider sends supported AMR or ACR signals so privileged users meet the phishing-resistant requirement without a second challenge.(see Added, Removed, and Reclassified Single Sign-On Authentication Signals)
Official Resources
Key Salesforce Help articles linked from the official roadmap:
- Security-Related Product Updates to the Salesforce Platform: User Identity, Data Protection, and Access Controls
- Prepare for Phishing-Resistant MFA Enforcement for Privileged Users, Including Admins
- Prepare for MFA Enforcement for All Employee Users
- Prepare for the upcoming Step-up Authentication requirements on Report Actions
- Prepare for Step-up Authentication in Anomalous Report Export
- Prepare for Transaction Security Policy Enhancements
- Mandatory Sending-Email Domain Verification Timeline
- Preventing Connections from Anonymizing VPNs, Proxies and High-Risk IP Addresses
- Extended Login Anomaly Detections and Containment
Always check the Release Group Enforcement Schedules inside the two primary Prepare articles for your exact production window.
Conclusion
Salesforce security updates 2026 have moved MFA for all employee users and phishing-resistant MFA for privileged users into active enforcement. Sandboxes began on July 10, 2026; production begins July 20, 2026 and continues on a staggered release-group schedule. Parallel controls for Salesforce email domain verification, step-up authentication, anomalous-behavior detection, and Transaction Security Policy enhancements are already live or imminent.
Admins who finish the Immediate checklist items this week, complete production testing before their July 20 window, and keep the official roadmap bookmarked will avoid lockouts and keep their orgs aligned with Salesforce’s strengthened security posture. End users need only register a verification method and keep contact details current.
Prepare now, before the next enforcement windows close.
Frequently Asked Questions
When does MFA become mandatory for all Salesforce users in 2026?
Sandbox enforcement started July 10, 2026. Production enforcement begins July 20, 2026 and is staggered by release group. Check the official Prepare for MFA Enforcement article for your org’s exact dates.
When does phishing-resistant MFA become required for Salesforce admins and privileged users?
Sandbox: starting July 10, 2026. Production: starting July 20, 2026 (staggered). Privileged users must use phishing-resistant methods such as passkeys or security keys.
What is step-up authentication in the Salesforce security updates 2026?
It is an extra identity verification required for sensitive actions such as viewing or exporting reports, even if the user recently logged in.
Does MFA enforcement apply to both direct logins and SSO?
Yes. The requirement covers direct UI logins and single sign-on logins for all employee users.
What happens if a user has not registered an MFA method by the enforcement date?
They will be prompted to register one. After full enforcement they cannot complete login without a valid method.
Is Salesforce email domain verification part of the 2026 security roadmap?
Yes. Phase 1 ran March–June 2026; Phase 2 enforcement for allowlisted domains runs June 29–July 27, 2026 in both sandboxes and production.
Where can I find the exact production date for my Salesforce org?
Locate your instance, map it to a release group, and consult the Release Group Enforcement Schedule published in the relevant Prepare knowledge articles.
