
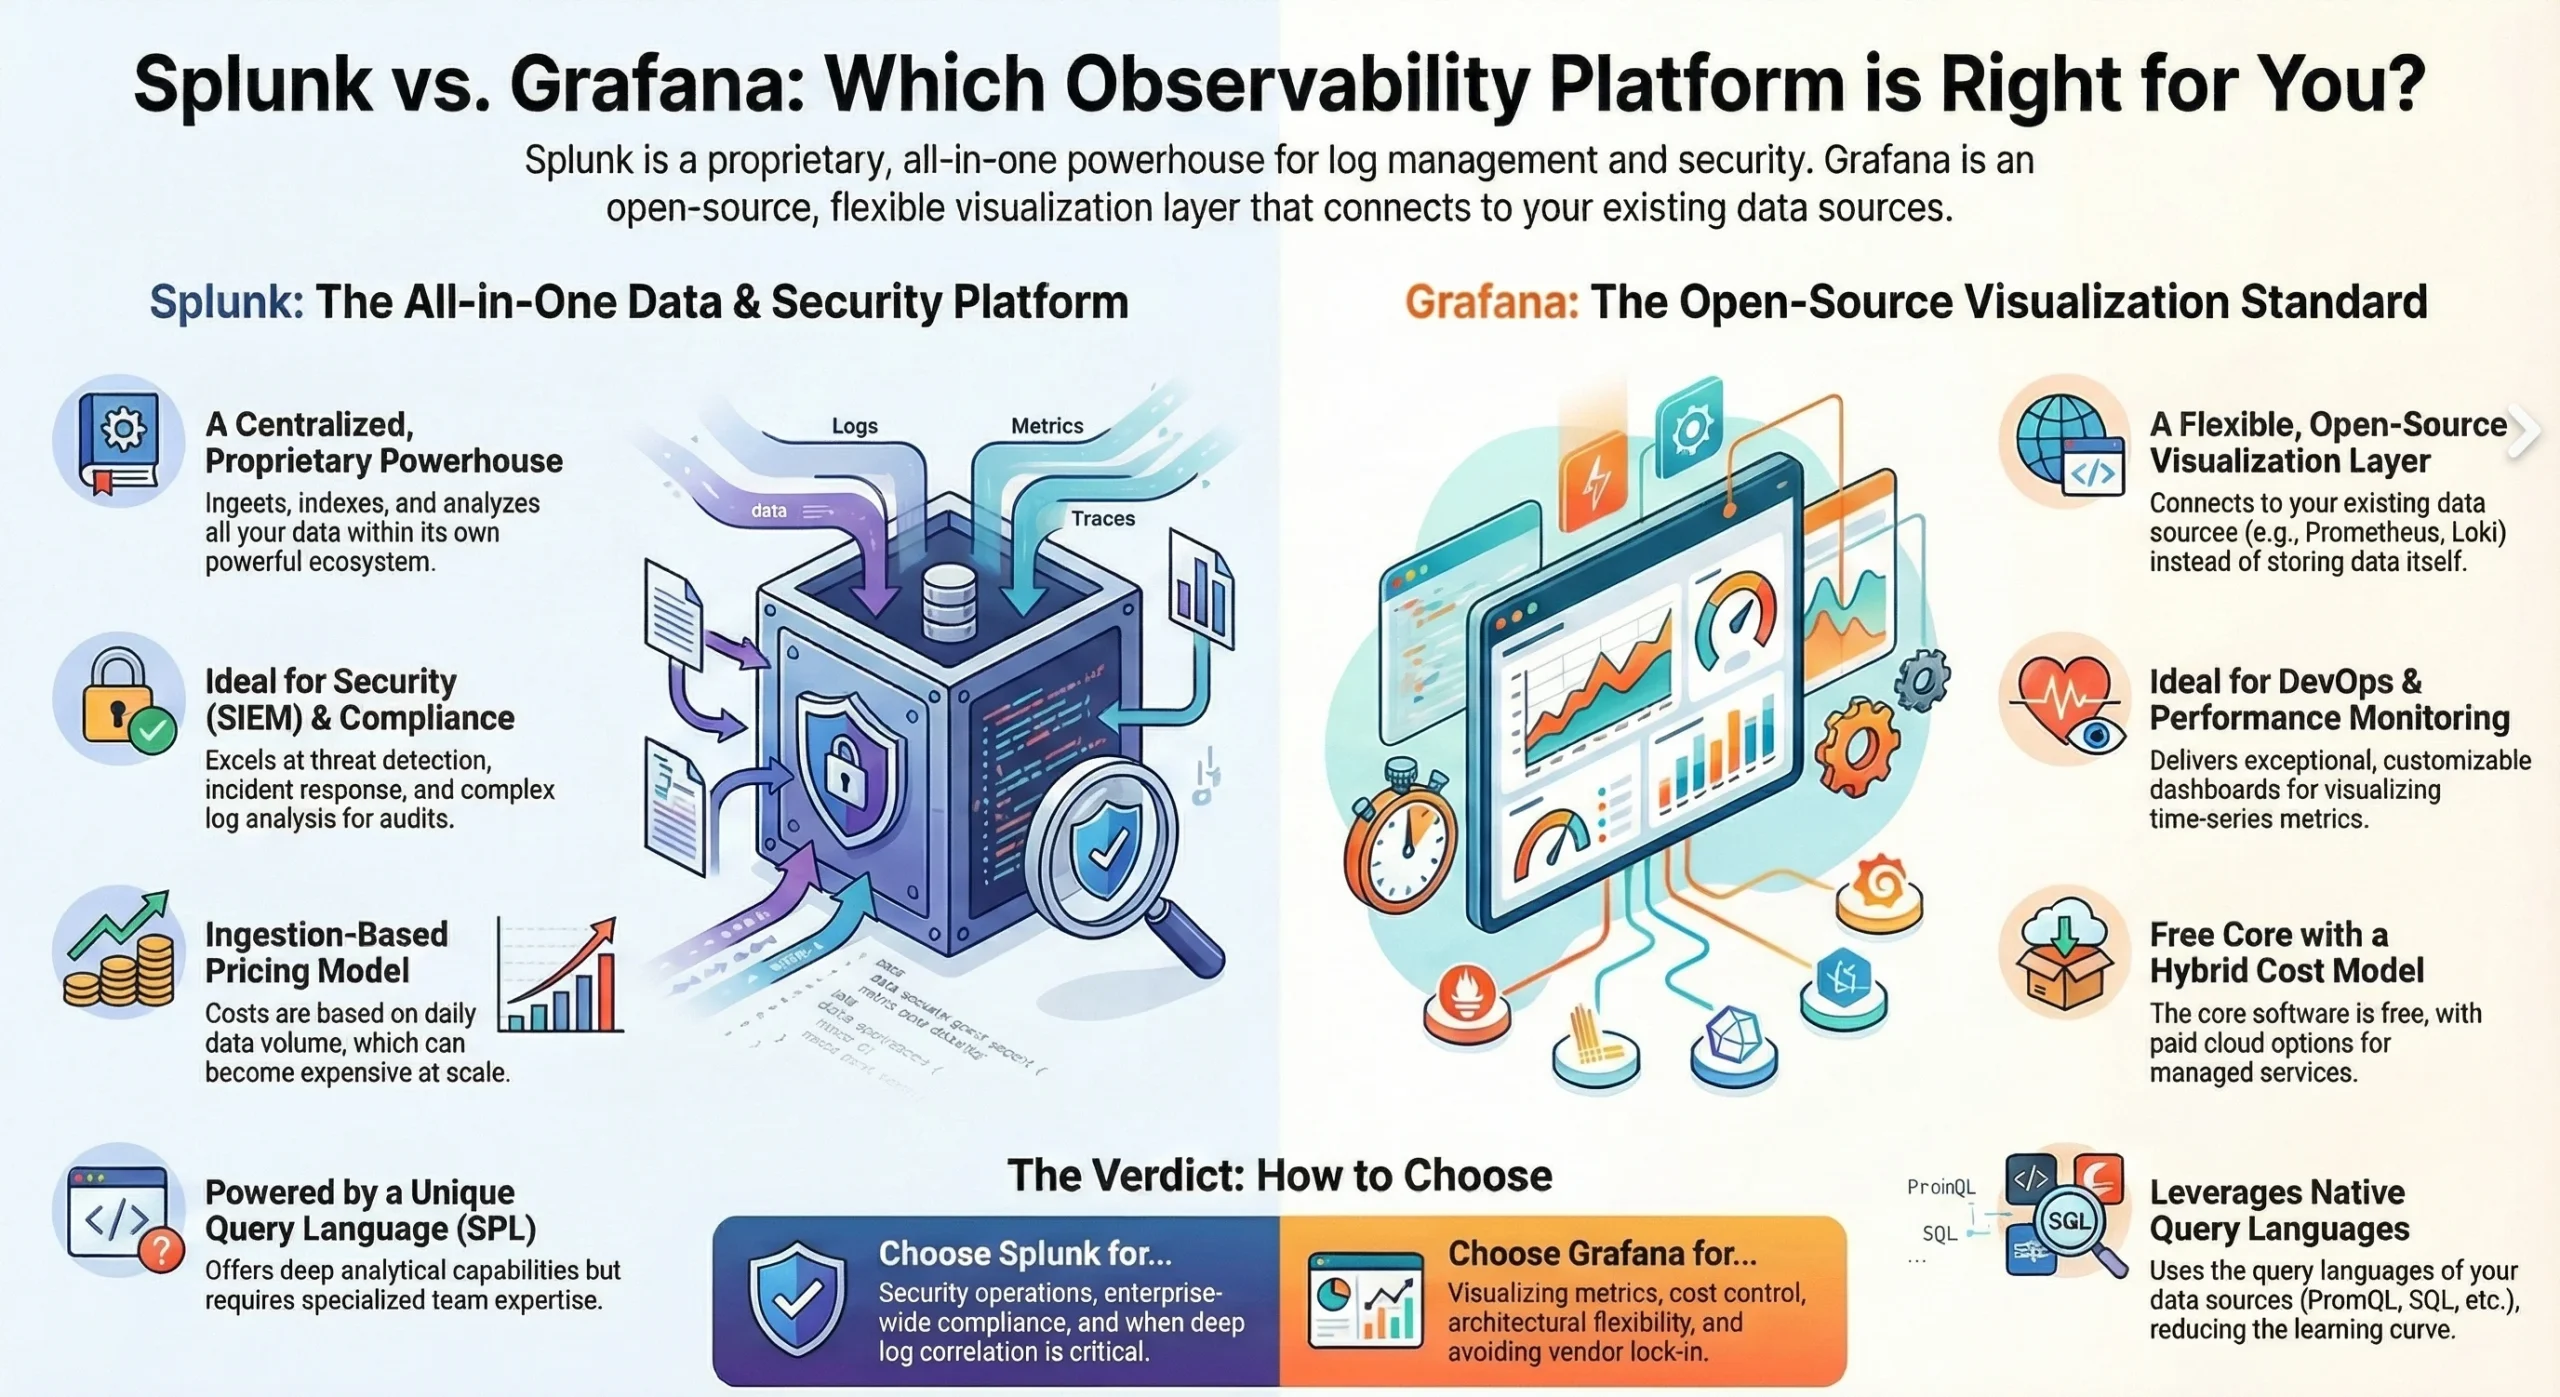
Making smart observability decisions in 2026 means understanding what you’re actually paying for. Splunk and Grafana dominate conversations about monitoring and log analysis, but they approach the problem from completely different angles. One is a proprietary powerhouse built for enterprise security and compliance, while the other champions open-source flexibility and visualization excellence.
Understanding the Observability Landscape: Metrics, Logs, and Traces
Modern observability platforms need to handle three critical data types. Metrics provide numeric measurements of system behavior over time think CPU usage or request rates. Logs capture discrete events with detailed context about what happened and when. Traces follow individual requests as they move through distributed systems, showing exactly where bottlenecks occur.
The challenge isn’t collecting this data. It’s making sense of it at scale without burning through your budget or drowning your team in complexity. Your observability stack needs to correlate these signals, surface actionable insights, and stay maintainable as your infrastructure grows. Both Splunk and Grafana tackle this challenge, but their approaches reflect fundamentally different philosophies about data ownership, vendor lock-in, and cost structures.
Defining Splunk: The Log Management and SIEM Powerhouse
Splunk built its reputation on one core strength: turning machine-generated data into searchable, analyzable intelligence. Organizations running large-scale infrastructure trust Splunk for real-time monitoring, security analytics, and compliance reporting. The platform excels at ingesting massive data volumes from virtually any source, indexing everything for rapid search, and providing sophisticated tools for threat detection and incident response. Splunk Enterprise Security transforms raw logs into actionable security intelligence, making it the go-to choice for SOC teams and security-focused organizations.
Defining Grafana: The Data Visualization and Monitoring Standard
Grafana started as a visualization layer and evolved into a complete observability platform. Unlike Splunk’s all-in-one approach, Grafana connects to your existing data sources whether that’s Prometheus, InfluxDB, Elasticsearch, or dozens of others and creates stunning dashboards that make complex data comprehensible. The open-source nature means zero licensing costs for the core product, with Grafana Cloud offering managed services for teams that want convenience without infrastructure overhead. Grafana’s strength lies in flexibility: it adapts to your architecture instead of forcing you to adapt to it.
Deep Dive into Key Capabilities: Search, Visualization, and Analytics
The technical differences between Splunk and Grafana reveal themselves most clearly in how each platform handles core observability workflows. These distinctions directly impact your team’s productivity, your infrastructure costs, and how quickly you can resolve incidents.
Data Ingestion and Architecture (Open Source Plugins vs. Proprietary Indexing)
Splunk’s architecture revolves around its proprietary indexing engine. Data flows through forwarders into indexers that parse, structure, and store everything in a searchable format. This centralized approach delivers blazing-fast search performance and powerful correlations, but it requires everything to live within Splunk’s ecosystem. You pay for every byte that gets indexed, which creates interesting economics when dealing with high-volume data streams.
Grafana takes the opposite approach. It doesn’t ingest or store data directly instead, it queries your existing data sources in real-time. This decoupled architecture means you can keep your metrics in Prometheus, your logs in Loki, and your traces in Tempo, all visualized through a unified Grafana interface. The plugin ecosystem supports over 50 data sources, from cloud providers to custom applications. This flexibility reduces storage costs but shifts the performance optimization burden to your data layer.
The practical difference? Splunk provides predictable query performance because everything lives in its optimized index. Grafana’s performance depends on your backend systems, which means you maintain more control over costs and architecture but need stronger infrastructure expertise. For teams already invested in Prometheus, InfluxDB, or other time-series databases, Grafana integrates seamlessly. For organizations building from scratch or consolidating scattered logs, Splunk’s unified ingestion simplifies deployment.
Read more: Splunk vs Elastic: The Ultimate Comparison
Dashboarding and Data Visualization Excellence (Customizability vs. Integrated Tools)
Grafana built its reputation on visualization, and it shows. The platform offers extensive customization options, from pixel-perfect dashboard layouts to complex panel configurations that combine multiple data sources. You can create interactive visualizations that drill down into specific metrics, overlay different data types, and adapt dynamically based on variables. The templating system lets you build reusable dashboards that work across environments. Community-contributed dashboards provide battle-tested templates for common monitoring scenarios, from Kubernetes clusters to PostgreSQL performance.
Splunk provides robust visualization through its Dashboard Studio, offering drag-and-drop dashboard building with pre-built visualizations for common use cases. The visualizations integrate tightly with SPL queries, enabling complex aggregations and statistical analysis directly within dashboard panels. Splunk’s strength lies in its ability to visualize security events, compliance data, and operational metrics within the same interface. The dashboards support real-time updates and can trigger alerts based on visual thresholds.
Here’s the practical trade-off: Grafana delivers superior visual flexibility and aesthetics, making it ideal for monitoring dashboards that teams watch constantly. Splunk’s visualizations prioritize functional depth over form, excelling at complex analytical workflows where the query language matters more than pixel-perfect design. For teams focused on application performance monitoring and infrastructure observability, Grafana typically provides better out-of-box experiences. For security operations centers analyzing log patterns and threat intelligence, Splunk’s integrated approach delivers faster time-to-insight.
Alerting and Notifications: Granular Control vs. Advanced Management Features
Both platforms take alerting seriously, but they implement it differently. Grafana’s alerting operates at the dashboard panel level, giving you precise control over individual metrics. You define alert rules using the same query languages your data sources support PromQL for Prometheus, SQL for databases, and so on. Alerts route through notification channels including Slack, PagerDuty, email, webhooks, and more. The unified alerting system in Grafana Cloud provides centralized management across multiple Grafana instances.
Splunk’s alerting ties directly to its search capabilities. You create alerts by saving searches with trigger conditions when a search returns specific results or crosses thresholds, Splunk fires notifications. This approach excels for pattern-based alerting, like detecting unusual spikes in failed authentication attempts or correlating events across multiple data sources. Splunk Enterprise Security includes pre-built correlation searches for common security scenarios. The alert actions extend beyond notifications to automated responses, integrating with SOAR platforms for incident orchestration.
The distinction matters for operational maturity. Grafana’s alerting works well for straightforward threshold-based monitoring and metric-driven scenarios. Teams familiar with their query languages can quickly configure sophisticated alerts. Splunk’s alerting shines in complex correlation scenarios where you need to detect patterns across disparate log sources or implement compliance-driven monitoring requirements. The learning curve is steeper, but the capabilities for advanced threat detection and anomaly identification justify the investment for security-focused teams.
Total Cost of Ownership (TCO): Analyzing Pricing Models and Hidden Costs
Cost conversations around observability tools get complicated quickly. List prices tell one story, actual spending tells another. Understanding the economic models behind Splunk and Grafana helps you forecast costs accurately and avoid surprise bills.
Splunk’s Ingestion-Based Pricing: Forecasting High-Volume Data Costs
Splunk’s pricing model centers on daily data ingestion volume. The entry point starts around $1,800 annually for 1GB per day, scaling up to $18,000 or more depending on features and support levels. For enterprise deployments, costs quickly escalate organizations with 200 hosts face list prices around $116,200, though negotiated discounts typically bring real costs to $60,300-$83,600.
The challenge with ingestion-based pricing lies in forecasting growth. Expanding your monitoring coverage or increasing log verbosity directly impacts your monthly bill. Splunk measures usage using a high-water mark system that looks at your peak daily ingestion, which means brief spikes can drive costs for entire months. Organizations frequently architect around Splunk’s pricing by filtering logs before ingestion, selectively indexing high-value data, and implementing data routing strategies.
Splunk has begun testing new pricing models that separate ingestion from analytics, potentially lowering unit prices for data management. According to recent announcements, the new pilot program will provide cost management features mapping spending to specific services and allowing more predictable spending allocation. This shift acknowledges customer frustration with pure volume-based pricing, but the new model remains in testing.
Grafana’s Hybrid Model: Maximizing Value from the Open-Source Version
Grafana’s economics work differently. The core product remains free and open-source, with self-hosted deployments costing only your infrastructure and maintenance overhead. Grafana Cloud introduces usage-based pricing for managed services, but with more granular controls than Splunk’s model.
Grafana Cloud offers an actually useful free tier, with paid plans starting at $8 per active user per month for basic features or $55 per user monthly for enterprise plugins. The Cloud Pro plan includes generous free allowances 10,000 active series for metrics, 50GB of logs, and 50GB of traces before usage charges kick in. Additional metrics cost based on active series and data points per minute, while logs and traces bill on actual ingestion.
For organizations willing to self-host, Grafana’s costs stay remarkably low. You provision your own data stores (Prometheus, Loki, Tempo), run Grafana instances on your infrastructure, and pay nothing for software licenses. This approach requires engineering investment in maintenance and updates but provides complete control over infrastructure spending. Many teams start with self-hosted Grafana and migrate to Grafana Cloud selectively as they scale or need managed services for specific workloads.
The Hidden Cost of Complexity: Comparing Required Expertise and Management Overhead
Licensing costs represent only part of total ownership expenses. The expertise required to operate these platforms effectively adds substantial hidden costs that many organizations underestimate.
Splunk demands significant specialized knowledge. The Splunk Processing Language (SPL) requires training for effective use. Indexer sizing, forwarder configuration, and search head clustering all require Splunk-specific expertise. Organizations typically need dedicated Splunk administrators or rely on consultants for implementation and optimization. Training costs for new team members add up comprehensive SPL training and certification programs represent meaningful investments. However, once teams master Splunk, the platform’s consistency and integrated tooling can improve productivity.
Grafana’s operational overhead depends heavily on your architecture choices. Self-hosted deployments require expertise in whatever data stores you choose Prometheus, Loki, InfluxDB, or others. Each backend brings its own operational requirements, query languages, and scaling considerations. This distributed complexity means your team needs broader skills across multiple systems. However, this knowledge often overlaps with existing infrastructure skills, particularly for cloud-native teams already running Prometheus for Kubernetes monitoring.
The learning curve shapes team productivity directly. Grafana’s gentler onboarding lets engineers create basic dashboards quickly, but advanced use cases require understanding each data source’s query language. Splunk’s steeper initial curve pays dividends for complex analytical workflows, where SPL’s power becomes essential. Budget for training, whether that means official courses, consultant time, or the opportunity cost of engineers climbing learning curves instead of shipping features.
Scalability, Performance, and Query Language Complexity
Technical capabilities matter most when systems hit production scale. How these platforms perform under load, their query language capabilities, and their enterprise-grade security features determine whether they’ll meet your needs at scale.
Query Language Mastery: Comparison of Splunk SPL vs. Grafana’s Multi-Query Support (PromQL/SQL)
Splunk Processing Language (SPL) represents a complete domain-specific language built for log analysis. SPL commands chain together using pipe syntax, enabling sophisticated data transformations, statistical analysis, and pattern matching. The language excels at text parsing, field extraction, and temporal analysis. Commands like stats, timechart, and transaction provide powerful aggregation capabilities. For security analysts investigating incidents or compliance teams building audit reports, SPL’s expressiveness directly translates to productivity.
The downside? SPL is proprietary and Splunk-specific. Your team’s SPL expertise doesn’t transfer to other platforms. Query optimization requires deep understanding of how Splunk’s indexers process searches, which field extractions happen at index time versus search time, and how to structure searches for performance. Complex SPL queries can become difficult to maintain as they grow more sophisticated.
Grafana takes a different approach by supporting each data source’s native query language. Working with Prometheus means writing PromQL queries that leverage Prometheus’s time-series database capabilities. Connecting to SQL databases uses standard SQL. This flexibility means your queries align with how each backend optimizes data retrieval. For teams already skilled in PromQL, SQL, or other query languages, Grafana requires no retraining.
The practical trade-off centers on consistency versus flexibility. Splunk provides one powerful language for everything. Grafana requires learning multiple query languages but lets you leverage each data store’s strengths. For organizations consolidating diverse data sources, Grafana’s approach can simplify migration existing Prometheus queries work unchanged. For teams building unified observability from scratch, Splunk’s single language reduces cognitive overhead.
Scalability for Enterprise Data Volumes (Distributed Architecture vs. Plugin-Based)
Splunk’s distributed architecture scales horizontally through indexer clustering and search head clustering. Indexer clusters provide data replication and load distribution, ensuring both availability and query performance. Search head clusters distribute user searches across multiple nodes. This architecture handles petabytes of data across thousands of forwarders. Splunk’s proven scalability makes it the standard for large enterprises processing massive log volumes from complex infrastructure.
The downside of Splunk’s scaling approach lies in cost and complexity. Adding indexer capacity means licensing more ingestion volume. Search head clusters require careful sizing and maintenance. Storage costs compound as you retain more data for compliance or analytical purposes. Many organizations struggle to balance retention requirements against storage economics.
Grafana’s scalability depends entirely on your backend choices. Prometheus scales through federation and remote storage backends. Loki scales using object storage and horizontal query scaling. This distributed approach means different components scale independently based on their specific requirements. You can optimize costs by choosing appropriate storage tiers, implementing data retention policies per data type, and scaling compute resources separately from storage.
The architectural differences shape operational models fundamentally. Splunk provides predictable scaling with known cost curves more data means more licensing and storage. Grafana offers optimization opportunities but requires more architectural planning. For organizations with cloud-native infrastructure already running distributed data stores, Grafana integrates naturally. For enterprises needing turnkey scalability with vendor support, Splunk’s integrated approach reduces operational complexity.
Security, Compliance, and Access Control (SIEM Focus vs. Standard RBAC)
Splunk Enterprise Security positions the platform as a complete SIEM solution. Pre-built correlation searches detect common attack patterns. Threat intelligence feeds integrate directly into security workflows. The platform provides audit trails, data masking, and compliance reporting frameworks for regulations like PCI DSS, HIPAA, and GDPR. Role-based access controls extend to granular data permissions, letting you restrict which users can see specific sensitive logs.
For security teams, Splunk’s compliance-focused features justify its cost. The platform streamlines SOC operations by correlating security events across infrastructure, applications, and network devices. Incident investigation workflows integrate directly with SOAR platforms. The machine learning toolkit helps identify anomalous behavior patterns that manual analysis might miss.
Grafana provides standard enterprise security features through role-based access control, team management, and organization structures. You control dashboard access, data source permissions, and user roles. However, Grafana isn’t positioned as a security analytics platform it’s a monitoring and visualization tool. Security-specific use cases require integration with dedicated security platforms or building custom workflows.
The distinction matters for regulatory environments. Organizations in finance, healthcare, or government sectors with strict compliance requirements often choose Splunk because its security features and audit capabilities align with regulatory frameworks. For engineering teams focused on application performance and infrastructure monitoring without heavy compliance burdens, Grafana’s standard security features suffice.
Read More: QRadar vs. Splunk which on is best in 2026?
Choosing the Right Tool: Use Case Alignment and Top Alternatives
The right observability platform depends on your specific requirements, team capabilities, and budget constraints. Understanding where each tool excels helps you match capabilities to needs.
When Should You Choose Splunk? (Focus on Security and Compliance)
Splunk makes sense for organizations where security operations, threat detection, and compliance drive observability requirements. If you operate a SOC, need sophisticated correlation across diverse log sources, or must maintain detailed audit trails for regulatory purposes, Splunk’s SIEM capabilities justify the investment. The platform excels when log analysis complexity matters more than cost sensitivity.
Choose Splunk when you need unified visibility across security, operations, and compliance from a single platform. The integrated approach simplifies workflows for teams juggling multiple responsibilities. Organizations with dedicated Splunk expertise or budget for specialized training get maximum value from the platform’s advanced capabilities.
Financial services firms, healthcare organizations, government agencies, and enterprises in regulated industries represent Splunk’s sweet spot. These organizations value Splunk’s audit capabilities, compliance frameworks, and security analytics despite higher costs. The platform’s ability to demonstrate compliance through detailed reporting often outweighs licensing expenses.
When Should You Choose Grafana? (Focus on Visualization and Time-Series Metrics)
Grafana excels for teams prioritizing application performance monitoring, infrastructure observability, and DevOps workflows. If your primary need involves visualizing metrics from Prometheus, monitoring Kubernetes clusters, or creating real-time dashboards that engineering teams watch constantly, Grafana delivers exceptional value.
Choose Grafana when you want flexibility and cost control. The open-source foundation lets you start small, scale gradually, and migrate to managed services only when complexity justifies the convenience. Teams comfortable managing distributed systems and multiple backend stores get maximum leverage from Grafana’s plugin ecosystem.
Cloud-native organizations, startups optimizing burn rates, and engineering-focused teams represent Grafana’s core audience. These teams value architectural flexibility, beautiful visualizations, and avoiding vendor lock-in. The ability to self-host eliminates licensing costs entirely, making Grafana attractive for budget-conscious organizations willing to invest engineering time in platform operations.
Top Alternatives for Unified Observability: Datadog, SigNoz, and Uptrace
The observability landscape extends beyond Splunk and Grafana. Several alternatives deserve consideration based on specific requirements.
Datadog provides unified observability combining APM, infrastructure monitoring, log management, and security monitoring in a single platform. The extensive integration library supports hundreds of technologies out-of-box. However, Datadog’s multi-dimensional usage-based pricing model can lead to unpredictable bills that are difficult to forecast and control. Organizations frequently report surprise invoices as their monitoring coverage expands. Datadog suits enterprises valuing comprehensive features and vendor-managed simplicity despite higher costs.
SigNoz offers an open-source alternative built on OpenTelemetry. The platform provides APM, logs, traces, metrics, exceptions, and alerts in a single tool, using ClickHouse as its datastore for fast query performance. SigNoz provides both self-hosted and cloud options, with transparent pricing at $0.10 per million samples for metrics. The OpenTelemetry-native approach avoids vendor lock-in while providing modern observability features. SigNoz works well for teams wanting unified observability without Datadog’s pricing complexity or Grafana’s distributed architecture.
Uptrace focuses on distributed tracing and performance monitoring, also built on OpenTelemetry. The platform specializes in deep insights into application latency, error rates, and system bottlenecks. Uptrace’s simplicity makes it attractive for teams primarily concerned with application performance rather than comprehensive infrastructure monitoring. The open-source nature and straightforward architecture provide cost-effective observability for development teams.
Final Verdict: Aligning Your Observability Stack with Business Goals
Your observability platform choice cascades through your organization’s technical capabilities, operational costs, and incident response effectiveness. Neither Splunk nor Grafana represents the universally “better” choice each excels in different contexts.
Choose Splunk when security, compliance, and enterprise-scale log analysis justify premium pricing. Choose Grafana when visualization excellence, architectural flexibility, and cost optimization matter most. Consider alternatives like SigNoz or Datadog when you need unified observability without the trade-offs inherent in either platform.
Start by mapping your actual requirements: What data sources need monitoring? What compliance obligations constrain your choices? What expertise does your team possess? What budget constraints guide decisions? These practical questions reveal which platform aligns with your reality better than any feature comparison chart.
The most successful observability strategies often combine tools strategically. Many organizations use Grafana for operational dashboards while maintaining Splunk for security analytics. Others start with open-source Grafana and migrate selectively to managed services as complexity grows. Your observability stack should evolve with your organization, not constrain it.
Frequently Asked Questions
Q: What is the core difference between Splunk and Grafana?
Splunk is a comprehensive, proprietary platform excelling at log management, real-time analytics, and SIEM capabilities. The platform ingests, indexes, and analyzes data from diverse sources through a unified interface. Grafana is primarily an open-source data visualization and monitoring tool, specializing in displaying metrics from various data sources through interactive dashboards. Grafana doesn’t ingest data directly but connects to existing data stores like Prometheus, InfluxDB, or Elasticsearch.
Q: Can Grafana be used alongside Splunk?
Yes, many organizations use Grafana alongside Splunk to leverage Grafana’s superior visualization capabilities while still benefiting from Splunk’s powerful data management and analysis features. Teams commonly pull data from Splunk into Grafana dashboards, combining Splunk’s indexing and search capabilities with Grafana’s flexible visualization layer. This hybrid approach lets you optimize costs by using each tool for its strengths.
Q: How does the pricing of Splunk and Grafana compare?
Splunk’s pricing is complex and based on data ingestion volume per day, making it expensive for large enterprises with high-volume logging needs. Costs start around $1,800 annually for 1GB daily ingestion but scale significantly with volume. Grafana is open-source and free for basic use, with optional paid versions (Grafana Cloud) offering additional enterprise features and support. Grafana Cloud starts at $8 per active user monthly, with substantial free-tier allowances for metrics, logs, and traces.
Q: Which tool is more suitable for large-scale enterprise deployments?
Splunk is often preferred for large-scale enterprise deployments due to its robust data management, proven scalability, strong compliance features, and ability to handle complex data analysis needs. The platform’s integrated architecture simplifies operations at scale, though costs increase substantially with data volume. Grafana can also scale to enterprise requirements but requires more architectural planning and expertise in managing distributed data stores. The choice depends on whether centralized control or architectural flexibility matters more for your organization.
Q: Does Grafana handle data ingestion directly?
No, Grafana does not handle data ingestion directly. Instead, it relies on connectors and plugins to pull data from a wide range of external sources such as Prometheus, InfluxDB, Elasticsearch, and cloud providers. This decoupled architecture means you manage data storage and ingestion separately, using Grafana purely as a visualization and monitoring layer. This approach provides flexibility but requires maintaining additional data infrastructure.
Q: What is the primary query language used by Splunk?
Splunk uses its custom Search Processing Language (SPL), optimized for searching, analyzing, and visualizing large volumes of machine-generated data. SPL provides powerful capabilities for text parsing, field extraction, statistical analysis, and temporal correlation. The language uses pipe syntax to chain commands together, enabling sophisticated data transformations. While powerful, SPL requires dedicated training and expertise, as it’s specific to the Splunk platform.
Q: Which tool is considered easier to use for beginners?
Grafana generally has a more user-friendly interface and simpler setup process, making it more accessible to users with varying levels of technical expertise. The intuitive dashboard editor and familiar query languages (like SQL or PromQL) reduce the learning curve. Splunk often has a steeper learning curve due to SPL complexity and the platform’s extensive feature set, though this depth enables more sophisticated analysis once mastered.
Q: Is Splunk an open-source product?
No, Splunk is proprietary, closed-source commercial software requiring paid licenses based on data ingestion volume. Grafana, in contrast, is an open-source project available under the AGPLv3 license, with optional commercial offerings like Grafana Cloud and Enterprise plugins. This fundamental difference affects cost structures, vendor lock-in concerns, and community contribution opportunities.
Q: How do the alerting capabilities compare between the two?
Splunk excels in advanced alert management and monitoring, offering comprehensive tracking and triggers based on complex search results and correlation patterns. The alerting integrates tightly with SPL, enabling sophisticated pattern detection and automated responses. Grafana provides robust alerting with precise control over alerting rules at the individual dashboard panel level, supporting multiple notification channels and flexible threshold configurations. Grafana’s alerting works well for metric-driven scenarios, while Splunk’s approach suits complex correlation and security-focused use cases.
Q: Which tool is recommended if visualization is the main priority?
If visualization is the primary focus, creating insightful dashboards, and leveraging existing data sources, Grafana stands out as the robust choice due to its exceptional visualization capabilities and data source flexibility. The platform was built with visualization as its core strength, offering extensive customization options, beautiful default themes, and an intuitive dashboard editor. While Splunk provides capable visualizations, its primary strengths lie in log analysis and security operations rather than visual excellence.
