
The STRIDE threat model is a structured framework for identifying security threats in software systems. STRIDE is an acronym for six threat categories: Spoofing, Tampering, Repudiation, Information Disclosure, Denial of Service, and Elevation of Privilege.
Who created STRIDE?
Praerit Garg and Loren Kohnfelder, both Microsoft engineers, developed STRIDE in 1999 as part of Microsoft’s internal security engineering process. It was later popularized through the Microsoft Security Development Lifecycle (SDL) and remains one of the most widely taught threat modeling methodologies in the world.
Why STRIDE still matters in 2026:
- It’s the default entry point for threat modeling education, still referenced in OWASP, NIST, and vendor security training.
- Cloud-native architectures (microservices, serverless, containers) have expanded, not shrunk, the attack surface STRIDE was built to map.
- AI agents and LLM-integrated applications introduce new trust boundaries that STRIDE’s per-element analysis handles better than ad hoc review.
- Regulatory frameworks (SOC 2, ISO 27001, PCI DSS 4.0) increasingly expect documented threat modeling, and STRIDE is the fastest framework to operationalize.
This guide covers the full STRIDE threat modeling framework, also written as stride threat modeling in UK/international usage, including definitions, threat modeling STRIDE methodology, a worked STRIDE threat model example, a ready-to-use STRIDE threat model template, tool recommendations including the Microsoft Threat Modeling Tool, and comparisons against the DREAD threat model and PASTA threat modeling. Whether you call it threat model STRIDE or the Microsoft STRIDE threat model, the underlying framework is identical.
What Is the STRIDE Threat Model?
STRIDE is a threat classification framework used during the design phase of the software development lifecycle (SDLC) to systematically identify potential security threats by mapping them against six categories, each corresponding to the violation of a specific security property.
STRIDE is the most widely used model for threat modeling. STRIDE-style analysis, a repeatable method for asking “what can go wrong here?” about every component in a system, rather than relying on ad hoc guesswork. It is often simply called the Microsoft STRIDE threat model, since Microsoft both created and continues to maintain tooling around it.
STRIDE Threat Model Full Form
| Letter | Threat Category | Security Property Violated |
|---|---|---|
| S | Spoofing | Authentication |
| T | Tampering | Integrity |
| R | Repudiation | Non-repudiation |
| I | Information Disclosure | Confidentiality |
| D | Denial of Service | Availability |
| E | Elevation of Privilege | Authorization |
History of STRIDE
STRIDE grew out of Microsoft’s internal security checklists in the late 1990s and was folded into the Microsoft Security Development Lifecycle by 2002. Adam Shostack later formalized the practice in his 2014 book Threat Modeling: Designing for Security, still a canonical reference. Unlike attack-tree or asset-centric approaches, STRIDE is element-centric, applied per component (processes, data stores, data flows, external entities) on a Data Flow Diagram, which is why it’s stayed repeatable and tool-friendly through 25+ years of architectural change, from monoliths to AI agents
How STRIDE Maps to Security Properties
Each STRIDE category is the negation of a core security property:
- Authentication → broken by Spoofing
- Integrity → broken by Tampering
- Non-repudiation → broken by Repudiation
- Confidentiality → broken by Information Disclosure
- Availability → broken by Denial of Service
- Authorization → broken by Elevation of Privilege
This mapping is why STRIDE is described as a mnemonic for threats to security properties, it converts abstract security goals into concrete, testable threat questions per system component.
The Six Categories of the STRIDE Threat Model Explained
Comparison Table: The 6-Pillars Of STRIDE
| Category | Definition | Violates | Applies To | Example Attack |
|---|---|---|---|---|
| Spoofing | Impersonating a user, device, or system component | Authentication | External entities, processes | Fake login page, IP spoofing |
| Tampering | Unauthorized modification of data or code | Integrity | Data stores, data flows, processes | Modifying a cookie, SQL injection to alter records |
| Repudiation | Denying an action without proof it occurred | Non-repudiation | Processes | Deleting logs after fraud, denying a transaction |
| Information Disclosure | Exposing data to unauthorized parties | Confidentiality | Data stores, data flows | Leaking PII via misconfigured S3 bucket |
| Denial of Service | Degrading or blocking legitimate access to a service | Availability | Processes, data flows | DDoS attack, resource exhaustion |
| Elevation of Privilege | Gaining capabilities beyond what’s authorized | Authorization | Processes | Privilege escalation via unpatched kernel bug |
Spoofing (Authentication)
An attacker pretends to be someone or something they’re not, a user, a device, a server, or an API client.
Real-world examples:
- Phishing pages that spoof legitimate login portals
- DNS spoofing redirecting users to malicious sites
- Spoofed API keys or JWTs with forged claims
- MAC/IP address spoofing on internal networks
Common attack scenarios:
- Credential stuffing against a login endpoint with no MFA
- Session token theft followed by replay
- Spoofed service identity in a microservices mesh with no mutual TLS
Mitigations:
- Multi-factor authentication (MFA)
- Strong password/credential policies + breach-password checks
- Mutual TLS (mTLS) for service-to-service auth
- Digital signatures and certificate pinning
- Anti-spoofing DNS controls (DNSSEC)
Tampering (Integrity)
Unauthorized alteration of data at rest, in transit, or in code.
Real-world examples:
- SQL injection modifying database records
- Man-in-the-middle attacks altering payloads in transit
- Supply chain attacks injecting malicious code into build pipelines (e.g., SolarWinds-style compromise)
- Tampering with client-side parameters (price manipulation in e-commerce)
Common attack scenarios:
- Modifying a hidden form field to change a price or role
- Altering firmware/binary integrity on IoT devices
- Injecting malicious commits into a CI/CD pipeline
Mitigations:
- Input validation and parameterized queries
- Cryptographic hashing and digital signatures (code signing)
- TLS everywhere, including internal service traffic
- File and database integrity monitoring
- Immutable infrastructure and signed container images
Repudiation (Non-repudiation)
A user or system denies performing an action, and there’s insufficient evidence to prove otherwise.
Real-world examples:
- An insider deletes financial records and denies involvement
- A user disputes a purchase with no audit trail to verify it
- An admin makes an unauthorized config change with no attribution
Common attack scenarios:
- Attacker clears or disables logging before performing a malicious action
- Shared service accounts used to obscure individual accountability
- Missing timestamps or unsigned logs that can be altered post hoc
Mitigations:
- Centralized, tamper-evident logging (write-once, hash-chained logs)
- Digital signatures on critical transactions
- Strong audit trails with user-level attribution (no shared accounts)
- Secure time-stamping (NTP integrity, signed timestamps)
Information Disclosure (Confidentiality)
Exposure of sensitive information to individuals or systems not authorized to see it.
Real-world examples:
- Misconfigured cloud storage buckets exposing customer PII
- Verbose error messages leaking stack traces or DB schema
- Unencrypted data in transit intercepted via packet sniffing
- API endpoints returning excess data fields (over-fetching)
Common attack scenarios:
- Directory traversal exposing server files
- Insecure direct object references (IDOR) leaking other users’ data
- Side-channel attacks (timing, cache) leaking cryptographic keys
Mitigations:
- Encryption at rest and in transit (AES-256, TLS 1.3)
- Least-privilege access controls and data minimization
- Proper error handling (generic messages to users, detailed logs internally)
- Data classification and DLP (data loss prevention) tooling
Denial of Service (Availability)
Actions that degrade, disable, or block legitimate access to a system or resource.
Real-world examples:
- Volumetric DDoS attacks against public endpoints
- Application-layer resource exhaustion (e.g., regex denial of service / ReDoS)
- Account lockout abuse to lock legitimate users out
Common attack scenarios:
- Flooding an API with expensive queries to exhaust compute
- Exploiting unbounded loops or recursive parsing
- Amplification attacks via misconfigured protocols (DNS, NTP)
Mitigations:
- Rate limiting and throttling
- Auto-scaling and load balancing
- Web Application Firewalls (WAF) and CDN-based DDoS protection
- Circuit breakers and graceful degradation patterns
- Input size and complexity limits
Elevation of Privilege (Authorization)
An attacker gains higher-level permissions than intended, often moving from limited access to full administrative control.
Real-world examples:
- Exploiting unpatched OS/kernel vulnerabilities for root access
- Broken access control allowing a standard user to reach admin APIs
- Container escape vulnerabilities granting host-level access
Common attack scenarios:
- Horizontal privilege escalation (accessing another user’s data)
- Vertical privilege escalation (user to admin)
- Misconfigured IAM roles granting excess cloud permissions
Mitigations:
- Principle of least privilege (PoLP) across all identities
- Role-based access control (RBAC) and attribute-based access control (ABAC)
- Regular patching and vulnerability management
- Just-in-time (JIT) privileged access and periodic access reviews
- Sandboxing and container hardening
How STRIDE Works – The Threat Modeling Process
What Are the 5 Steps of Threat Modeling?
Most threat modeling methodologies, including STRIDE-based approaches, follow this general sequence:
- Define security objectives: What are you protecting, and against what compliance/business requirements?
- Create an application overview / decompose the application: Build a Data Flow Diagram (DFD) with trust boundaries.
- Identify threats: Apply STRIDE to each element of the DFD.
- Mitigate threats: Rank and address findings, often scored with DREAD or CVSS.
- Validate: Review, test, and document that mitigations are in place.
Step-by-Step STRIDE Tutorial
Step 1: Decompose the Application
Break the system into its constituent parts using a Data Flow Diagram (DFD). A DFD typically uses four element types:

| DFD Element | Symbol | Description |
|---|---|---|
| External Entity | Rectangle | Users, external systems (outside your control) |
| Process | Circle/Rounded Rectangle | Code that transforms or handles data |
| Data Store | Parallel Lines | Databases, files, caches |
| Data Flow | Arrow | Movement of data between elements |
| Trust Boundary | Dashed Line | Where trust level or privilege changes |
Trust boundaries are critical, they mark points where data crosses from one privilege/trust zone to another (e.g., internet → DMZ, or user tier → admin tier). Threats concentrate at trust boundaries because that’s where assumptions about “who can be trusted” are tested.
Step 2: Apply STRIDE Per Element
Not every STRIDE category applies to every DFD element type. Use this mapping to scope your analysis efficiently:

Step 3: Score with DREAD
Once threats are identified, prioritize them. DREAD is the classic companion scoring model to STRIDE, rating each threat 1–10 (or High/Medium/Low) across five factors:
| DREAD Factor | Question |
|---|---|
| Damage | How bad would the impact be? |
| Reproducibility | How easily can the attack be repeated? |
| Exploitability | How much effort/skill is required? |
| Affected Users | How many users/systems are impacted? |
| Discoverability | How easily can the flaw be found? |
Average the five scores to get an overall risk rating per threat. (Many teams today substitute CVSS or a custom Likelihood × Impact matrix, more on this in the comparison section.)
Step 4: Prioritize & Mitigate
- Rank threats by DREAD/risk score.
- Map each threat to a mitigation category: Redesign, Mitigate control, Accept risk, Transfer risk (insurance/vendor), or Eliminate feature.
- Assign owners and deadlines, a threat model without accountability doesn’t reduce risk.
Step 5: Document & Review
- Store the DFD, threat list, DREAD scores, and mitigations in a living document (not a one-time PDF).
- Re-run STRIDE whenever architecture changes materially (new trust boundary, new external integration, new data store).
- Review at least once per release cycle or quarterly for high-risk systems.
STRIDE Threat Model Template & Tools
Ready-to-Use STRIDE Threat Model Template
Use this table structure for every system you model:
| ID | Element | STRIDE Category | Threat Description | DREAD Score | Mitigation | Owner | Status |
|---|---|---|---|---|---|---|---|
| T-001 | Login API | Spoofing | Credential stuffing due to no MFA | 8/10 | Enforce MFA | AppSec Team | Open |
| T-002 | User DB | Information Disclosure | Unencrypted PII at rest | 9/10 | Enable AES-256 encryption | DBA Team | In Progress |
| T-003 | Order Service | Elevation of Privilege | IDOR on /orders/{id} | 7/10 | Add ownership check | Backend Team | Open |
Threat Modeling Checklist
- DFD created with all external entities, processes, data stores, and data flows
- Trust boundaries clearly marked
- STRIDE applied to every applicable element
- Each threat scored (DREAD or equivalent)
- Mitigations mapped and assigned to owners
- High/critical threats have remediation deadlines
- Threat model reviewed by someone outside the dev team
- Document stored in version control alongside architecture docs
- Re-review scheduled (quarterly or per major release)
Tools for STRIDE Threat Modeling
| Tool | Type | Best For |
|---|---|---|
| Microsoft Threat Modeling Tool | Free, DFD-based, auto-generates STRIDE threats | Teams standardizing on Microsoft’s methodology |
| OWASP Threat Dragon | Free, open-source, web/desktop | Open-source teams wanting DFD + STRIDE built in |
| IriusRisk | Commercial | Enterprise-scale automated threat modeling with SDLC integration |
| Threagile | Open-source, YAML-based | Threat-modeling-as-code / CI pipeline integration |
| STRIDE GPT | AI-assisted | Rapid draft threat models from architecture descriptions |
The Microsoft Threat Modeling Tool remains the most-cited free tool: it lets you draw a DFD, auto-suggests STRIDE-categorized threats per element based on its stencil library, and exports reports. It’s Windows-based and best suited to teams already in the Microsoft security ecosystem.
Practical Examples

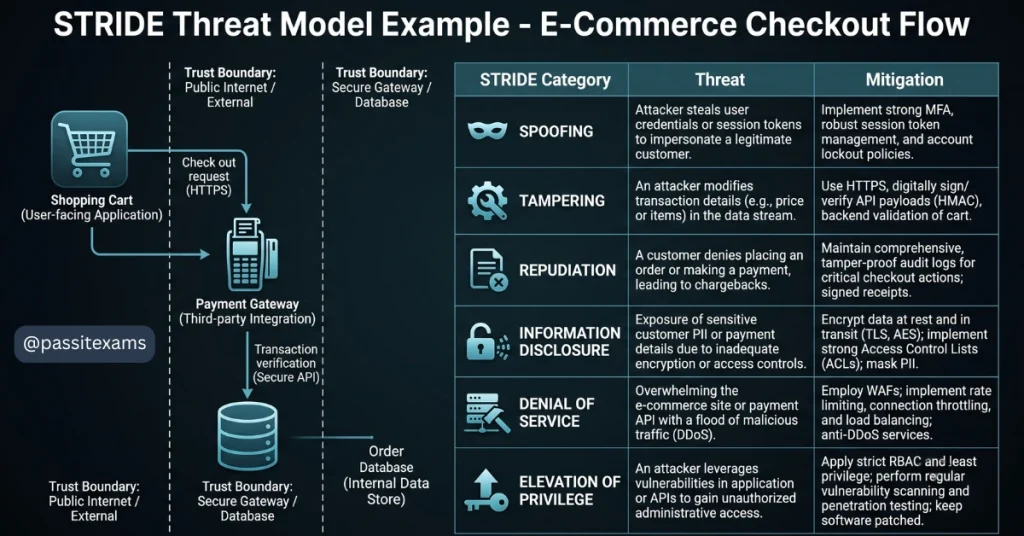
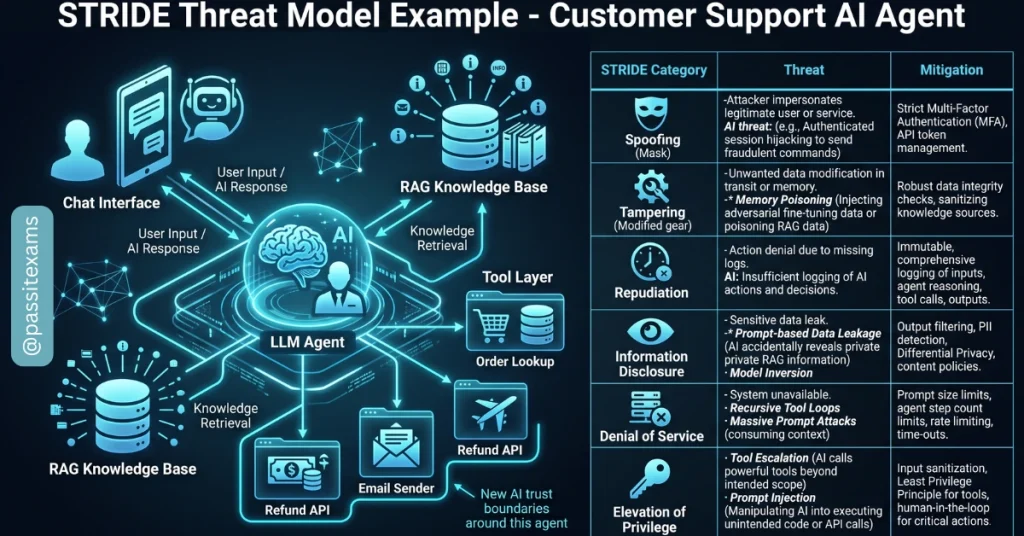
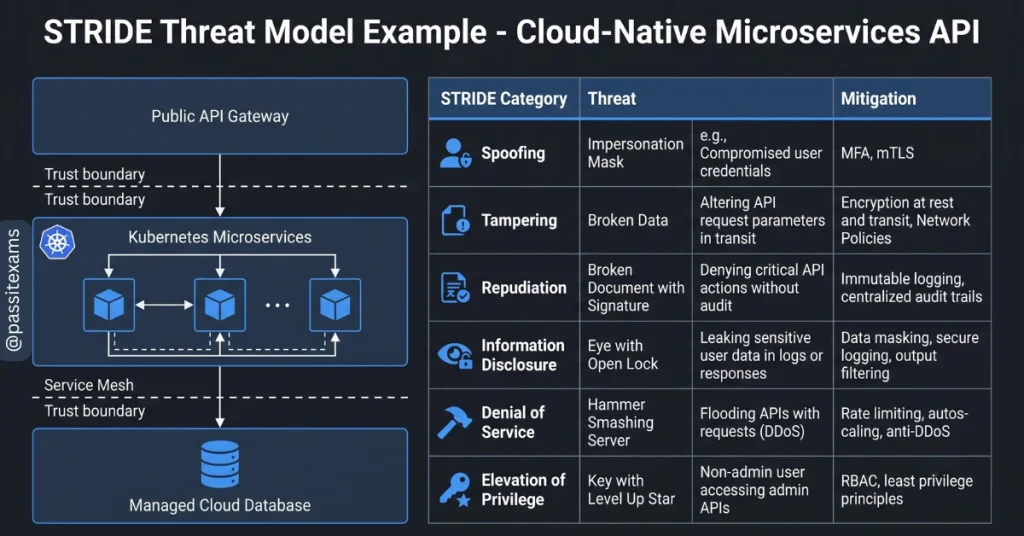
Benefits of the STRIDE Threat Model
Top Benefits
- Structured, repeatable coverage, no threat category is forgotten because the mnemonic forces systematic review.
- Design-phase risk reduction, threats found before code is written cost far less to fix than post-deployment vulnerabilities.
- Common language across teams, developers, architects, and security teams speak the same STRIDE vocabulary.
- Tool ecosystem maturity, 25+ years of tooling (Microsoft Threat Modeling Tool, OWASP Threat Dragon, IriusRisk) reduces adoption friction.
- Compliance alignment, supports SOC 2, ISO 27001, and PCI DSS 4.0 requirements for documented risk assessment.
- Scales from monoliths to microservices, the DFD/trust-boundary approach adapts naturally to distributed systems.
Why Design-Phase Threat Modeling Pays Off: The Data
STRIDE’s core value proposition, catching threats before code ships, is backed by independent cost data, not just Microsoft’s own marketing:
| Source | Finding |
|---|---|
| IBM Systems Sciences Institute | Fixing a defect found in production costs roughly 100x more than fixing the same defect during the design phase, a multiplier that climbs progressively: ~1x at design, ~6.5x at implementation, ~15x at testing, up to 100x post-release. |
| NIST (Economic Impacts of Inadequate Infrastructure for Software Testing) | Vulnerabilities fixed in production cost roughly 30x more than fixing the same issue during development. |
| Security Compass (Security by Design research) | Organizations that build security in at the design stage (the same principle STRIDE operationalizes) cut vulnerabilities by up to 79% compared to bolt-on, post-release remediation. |
| IEEE Computer Society | The average cost to repair a single vulnerability during the design phase is under $500, versus tens of thousands of dollars once it reaches production. |
Microsoft has stated publicly that its Security Development Lifecycle, with STRIDE-based threat modeling as a mandatory design-phase gate since 2004, has measurably reduced vulnerability counts in shipped products, though Microsoft does not publish an exact percentage figure. The design-phase cost multipliers above are the reason threat modeling frameworks like STRIDE exist in the first place: the earlier a threat is found, the cheaper it is to fix, and STRIDE is the fastest structured method for finding threats at design time.
STRIDE for Cloud Security
Cloud environments multiply trust boundaries: IAM roles, cross-account access, shared responsibility boundaries between cloud provider and tenant, and multi-tenant data stores. STRIDE applied to cloud architecture diagrams surfaces misconfigurations (a leading cause of cloud breaches) before they reach production, particularly Information Disclosure (public buckets) and Elevation of Privilege (over-permissioned IAM roles).
STRIDE and Zero Trust
Zero Trust architecture assumes no implicit trust based on network location. STRIDE complements this directly:
- Spoofing mitigations (mTLS, strong identity verification) are foundational to Zero Trust’s “verify explicitly” principle.
- Elevation of Privilege mitigations (least privilege, JIT access) map to Zero Trust’s “least privilege access” pillar.
- Trust boundary mapping in STRIDE’s DFD process is functionally identical to identifying Zero Trust segmentation points.
STRIDE Integration in the SDLC
| SDLC Phase | STRIDE Activity |
|---|---|
| Requirements | Define security objectives and compliance drivers |
| Design | Build DFD, apply STRIDE, score with DREAD |
| Development | Implement mitigations, secure coding aligned to identified threats |
| Testing | Validate mitigations via penetration testing / abuse-case testing |
| Deployment | Re-verify trust boundaries in production configuration |
| Maintenance | Re-run STRIDE on architecture changes; continuous review |
STRIDE vs Other Frameworks
STRIDE vs DREAD
STRIDE and DREAD are complementary, not competing, STRIDE identifies threats, DREAD scores them.
| Aspect | STRIDE | DREAD |
|---|---|---|
| Purpose | Threat identification/classification | Threat risk scoring |
| Output | List of categorized threats | Numeric risk score per threat |
| Used When | Design/architecture phase | After threats are identified, for prioritization |
| Created By | Microsoft (1999) | Microsoft (early 2000s) |
| Current Status | Widely used | Largely deprecated at Microsoft in favor of a simplified High/Medium/Low bug bar, though still taught and used elsewhere |
| Best Paired With | DFDs, trust boundary analysis | STRIDE output, CVSS as an alternative |
STRIDE vs PASTA Threat Modeling
| Aspect | STRIDE | PASTA (Process for Attack Simulation and Threat Analysis) |
|---|---|---|
| Approach | Element-centric (per DFD component) | Risk-centric, attacker-simulation-driven |
| Steps | Typically 5 (decompose, apply, score, mitigate, review) | 7 formal stages |
| Focus | Technical threat coverage | Business impact and attacker motivation |
| Complexity | Lower, good for individual features/services | Higher, suited to enterprise-wide risk programs |
| Output | Categorized threat list | Risk-prioritized attack scenarios tied to business impact |
| Best For | Dev teams, feature-level design reviews | Security teams doing organization-wide risk assessment |
STRIDE vs Other Frameworks (Quick Reference)
| Framework | Type | Strength | When to Use Instead of/With STRIDE |
|---|---|---|---|
| DREAD | Scoring | Simple prioritization | Use alongside STRIDE for ranking |
| PASTA | Risk-centric, 7-stage | Business-risk alignment | Use for enterprise risk programs |
| VAST | Scalable, Agile-friendly | Integrates with Agile/DevOps at scale | Use for large orgs needing automation across hundreds of teams |
| Attack Trees | Visual attack path modeling | Deep single-scenario analysis | Use to drill into a specific high-risk threat found via STRIDE |
| OCTAVE | Asset-centric, org-wide | Organizational risk management | Use for enterprise security strategy, less for single-app design |
| LINDDUN | Privacy-focused | Privacy threat modeling | Use alongside STRIDE when privacy/GDPR is a primary concern |
When to combine frameworks: Use STRIDE to identify and categorize threats at the design level, DREAD or CVSS to score them, and PASTA (or a business-impact overlay) when you need to justify security investment to executives in business terms.
Advanced Topics & Modern Applications
STRIDE in Cloud-Native and Container Environments
Modern applications require extending classic DFDs to represent:
- Kubernetes namespaces and pod-to-pod trust boundaries
- Service mesh identity (SPIFFE/SPIRE, mTLS certificates)
- Infrastructure-as-Code (IaC) misconfigurations as a Tampering/Information Disclosure surface
- Serverless function triggers as new “external entity” equivalents
Applying Classic STRIDE to LLMs and AI Agents
2026’s biggest shift in threat modeling practice is applying STRIDE to systems where a component can reason, plan, call tools, and act autonomously, something the original 1999 framework never anticipated. Classic STRIDE still works as a starting point, but it needs deliberate adaptation. Here’s how to apply it in practice.
Step 1: Add AI-specific elements to your DFD. Treat each of the following as a distinct element requiring its own STRIDE pass, not as a black box inside a single “AI process” bubble:
| New DFD Element | What It Is | STRIDE Categories Most at Risk |
|---|---|---|
| Prompt/context window | The instructions and conversation history fed to the model | Spoofing, Tampering |
| Tool-calling interface | The mechanism the agent uses to invoke external functions/APIs | Elevation of Privilege, Tampering |
| Memory / vector store (RAG) | Long-term or retrieval-augmented data the agent reads from | Tampering, Information Disclosure |
| Agent-to-agent channel | Communication between multiple cooperating agents | Spoofing, Repudiation |
| Model output / action executor | The step where the agent’s decision becomes a real-world action | Elevation of Privilege, Denial of Service |
Step 2: Map STRIDE categories to concrete LLM/agent threats.
| STRIDE Category | Classic Threat | LLM/Agent-Specific Equivalent |
|---|---|---|
| Spoofing | Fake login credentials | Indirect prompt injection, a malicious document, email, or webpage the agent reads impersonates a trusted instruction source |
| Tampering | Modifying a database record | Memory/RAG poisoning, injecting false data into a vector store the agent later retrieves and trusts as fact |
| Repudiation | Denying a transaction | Agent takes an autonomous action (e.g., sends an email, executes a trade) with no attributable, tamper-evident action log |
| Information Disclosure | Leaking a database | Agent leaks its system prompt, other users’ conversation history, or credentials embedded in its tool configuration through crafted queries |
| Denial of Service | Flooding an API | Resource-exhaustion via recursive tool calls or adversarial inputs that force excessively long reasoning chains, spiking compute cost |
| Elevation of Privilege | Exploiting a kernel bug | The “confused deputy” problem, an agent with broad tool access is manipulated into using its own legitimate permissions to perform an action the user never authorized (the single most-cited agentic AI risk in 2026 security research) |
Step 3: Know when classic STRIDE needs a companion framework. Independent research has confirmed STRIDE’s limits here directly. A 2025 peer-reviewed study (Zambare, Thanikella, and Liu, Texas Tech University) found that STRIDE “does not model emergent behavior, cognitive reasoning of AI agents very well,” and the OWASP Agentic Security Initiative reached the same conclusion. In response, two frameworks have emerged as STRIDE companions rather than replacements:
- CSA MAESTRO (Cloud Security Alliance), a seven-layer reference architecture (Foundation Models, Data Operations, Agent Frameworks, Deployment & Infrastructure, Evaluation & Observability, Security/Compliance, Agent Ecosystem) purpose-built for agentic AI. MAESTRO doesn’t discard STRIDE, it applies STRIDE-style categorization within each layer while adding agent-specific concerns STRIDE alone misses: goal misalignment, multi-agent collusion, and autonomous decision drift.
- ATFAA (Advanced Threat Framework for Autonomous AI Agents), an academic extension that explicitly maps its 9-threat taxonomy back onto the six STRIDE categories, then adds agent-specific domains around identity coherence (keeping agent, user, and system identities cryptographically distinct to prevent spoofing-style impersonation) and governance scalability.
Practical guidance for 2026 teams: Run classic STRIDE first, it will catch the majority of infrastructure-level threats (API security, data storage, network exposure) around your AI system exactly as it would for any other application. Then layer MAESTRO or ATFAA on top specifically for the reasoning, memory, and multi-step tool-execution surfaces that STRIDE’s static, per-element model wasn’t designed to capture. Treat this as STRIDE-plus, not STRIDE-replaced.
AI-assisted tooling: Tools like STRIDE GPT and similar LLM-assisted threat modeling assistants take an architecture description as input and auto-generate a draft STRIDE threat list, accelerating the decomposition step from hours to minutes. Human review remains essential, these tools can miss context-specific trust boundaries or generate generic, low-value threats if the architecture description is vague.
Limitations of STRIDE (and How to Overcome Them)
| Limitation | Why It Matters | How to Overcome |
|---|---|---|
| Doesn’t prioritize by business impact | STRIDE finds threats but doesn’t rank by cost to the business | Pair with DREAD/CVSS or a PASTA-style business impact overlay |
| Can be time-consuming at scale | Manually modeling hundreds of microservices is slow | Use automation (Threagile, IriusRisk, STRIDE GPT) and threat-modeling-as-code |
| Requires DFD accuracy | Outdated or incomplete diagrams produce incomplete threat models | Keep DFDs in version control, auto-generate from IaC where possible |
| Not privacy-specific | STRIDE doesn’t deeply cover privacy harms (e.g., linkability, unawareness) | Combine with LINDDUN for privacy-sensitive systems |
| Analyst experience-dependent | Junior analysts may miss subtle threats | Use checklists, peer review, and AI-assisted drafting as a baseline, not a replacement |
Implementation Guide
Integrating STRIDE into the SDLC
- Mandate threat modeling at design review, no architecture gets approved without a STRIDE pass for any new external-facing component or trust boundary change.
- Automate where possible, generate DFDs from IaC/Terraform where feasible; use threat-modeling-as-code (Threagile) in CI pipelines for continuous validation.
- Track threats as first-class backlog items, feed high/critical STRIDE findings directly into the engineering backlog with the same rigor as bugs.
- Re-trigger on architectural drift, new third-party integration, new data store, new trust boundary = re-run STRIDE for the affected components.
Best Practices
- Keep DFDs at the right altitude, too detailed becomes unmaintainable, too abstract misses real threats.
- Involve both developers and security engineers; developers know implementation details security teams miss.
- Time-box each STRIDE session (60–90 minutes per component) to avoid analysis paralysis.
- Always assign an owner and deadline to every identified threat, an unowned threat is a threat that never gets fixed.
- Re-review threat models at least quarterly for high-risk systems, and after every major release for all systems.
Common Mistakes
| Mistake | Consequence | Fix |
|---|---|---|
| Treating STRIDE as a one-time exercise | Threat model goes stale, misses new risks | Schedule recurring reviews tied to release cycles |
| Skipping DREAD/prioritization | Team fixes low-impact issues while critical ones sit open | Always score and rank before assigning remediation |
| Modeling too late (post-deployment) | Expensive redesigns instead of cheap design fixes | Embed STRIDE at the design review stage |
| No ownership assigned to findings | Threats identified but never remediated | Every threat gets an owner and a due date |
| Ignoring trust boundaries in cloud/IAM | Misses cross-account and privilege-escalation threats | Explicitly diagram IAM roles and cross-account trust |
When to Hire Professionals
Consider bringing in dedicated threat modeling or application security consultants when:
- You’re threat modeling a system handling regulated data (health, financial, government) for the first time
- Internal teams lack threat modeling experience and need to establish a repeatable internal process
- You’re preparing for a compliance audit requiring documented, expert-reviewed threat models
- The system is business-critical and a flawed threat model carries outsized financial/reputational risk
Frequently Asked Questions FAQ’s
What is the STRIDE threat model?
STRIDE is a threat classification framework created by Microsoft that identifies six categories of security threats, Spoofing, Tampering, Repudiation, Information Disclosure, Denial of Service, and Elevation of Privilege, applied to elements of a system’s data flow diagram.
What does STRIDE stand for?
Spoofing, Tampering, Repudiation, Information Disclosure, Denial of Service, Elevation of Privilege.
Who created the STRIDE threat model?
Praerit Garg and Loren Kohnfelder, Microsoft engineers, created STRIDE in 1999.
What are the six components of the STRIDE threat model?
Spoofing (authentication), Tampering (integrity), Repudiation (non-repudiation), Information Disclosure (confidentiality), Denial of Service (availability), and Elevation of Privilege (authorization).
How is STRIDE applied to a system?
By building a Data Flow Diagram of the system, identifying trust boundaries, and asking which of the six STRIDE threats could apply to each process, data store, data flow, and external entity.
What is the difference between STRIDE and DREAD?
STRIDE identifies and categorizes threats; DREAD scores and prioritizes them by Damage, Reproducibility, Exploitability, Affected users, and Discoverability. They are typically used together.
What is the difference between STRIDE and PASTA threat modeling?
STRIDE is element-centric and technical, applied per system component. PASTA is a 7-stage, risk-centric methodology that ties threats to business impact and simulates attacker behavior, better suited to enterprise-wide risk assessment.
Is there a free STRIDE threat model template?
Yes, use a table with columns for Element, STRIDE Category, Threat Description, DREAD Score, Mitigation, Owner, and Status (see the template section above), or use the free Microsoft Threat Modeling Tool or OWASP Threat Dragon.
What is the Microsoft Threat Modeling Tool?
A free tool from Microsoft that lets you draw a Data Flow Diagram and automatically generates STRIDE-categorized threat suggestions per element, with exportable reports.
Can STRIDE be used for cloud security?
Yes. STRIDE applies directly to cloud architectures by treating IAM roles, cross-account boundaries, and managed services as DFD elements with their own trust boundaries, it’s especially effective at surfacing Information Disclosure (misconfigured storage) and Elevation of Privilege (over-permissioned roles) risks.
How does STRIDE apply to AI agents and LLM applications?
Extensions like ASTRIDE apply STRIDE to AI-specific components, the agent’s reasoning loop, tool-calling interface, and memory/RAG store, to catch threats like prompt injection (Spoofing), memory poisoning (Tampering), and excessive tool-call permissions (Elevation of Privilege).
What are the 5 steps of the threat modeling process?
- Define security objectives, 2) Decompose the application (DFD + trust boundaries), 3) Identify threats (apply STRIDE), 4) Mitigate threats (score and prioritize), 5) Validate and document.
Is STRIDE still relevant in 2026?
Yes. Despite being 25+ years old, STRIDE remains the most widely taught and tool-supported threat modeling framework, and it adapts well to cloud-native, Zero Trust, and AI agent architectures.
What are the limitations of STRIDE?
It doesn’t inherently prioritize threats by business impact, can be slow at scale without automation, depends on accurate DFDs, and isn’t privacy-specific (pair with LINDDUN for privacy threats).
Where can I get a STRIDE threat model PDF for reference?
Export a report directly from the Microsoft Threat Modeling Tool or OWASP Threat Dragon after completing your model, both tools generate shareable PDF/document reports suitable for audit and compliance evidence.
Conclusion & Next Steps
STRIDE remains the fastest, most teachable way to systematically find design-level security threats, from a simple login form to a fleet of AI agents with tool access. Its strength is coverage: six categories, mapped to six security properties, applied consistently across every component of your system.
Actionable checklist to get started this week:
- Pick one system (start with something internet-facing) and build its Data Flow Diagram.
- Mark every trust boundary explicitly.
- Apply STRIDE to each process, data store, data flow, and external entity.
- Score findings with DREAD (or CVSS if your org already uses it).
- Assign owners and deadlines to every High/Critical threat.
- Use the Microsoft Threat Modeling Tool or OWASP Threat Dragon to formalize and export the model.
- Schedule a recurring review, quarterly, or on every major architecture change.
Threat modeling isn’t a one-time compliance checkbox, it’s a design discipline. Build it into your SDLC now, and STRIDE will keep paying off as your architecture, and your threat surface, keeps evolving.
