
The Nmap Scripting Engine (NSE) turns a basic port scanner into a full vulnerability-discovery platform. If you’re preparing for OSCP, running a bug bounty engagement, or doing internal network assessments, a small set of NSE scripts will do most of the heavy lifting. This guide breaks down the 10 most valuable ones, with exact commands and sample output.
The 10 Scripts You Need
| # | Script | What It Does |
|---|---|---|
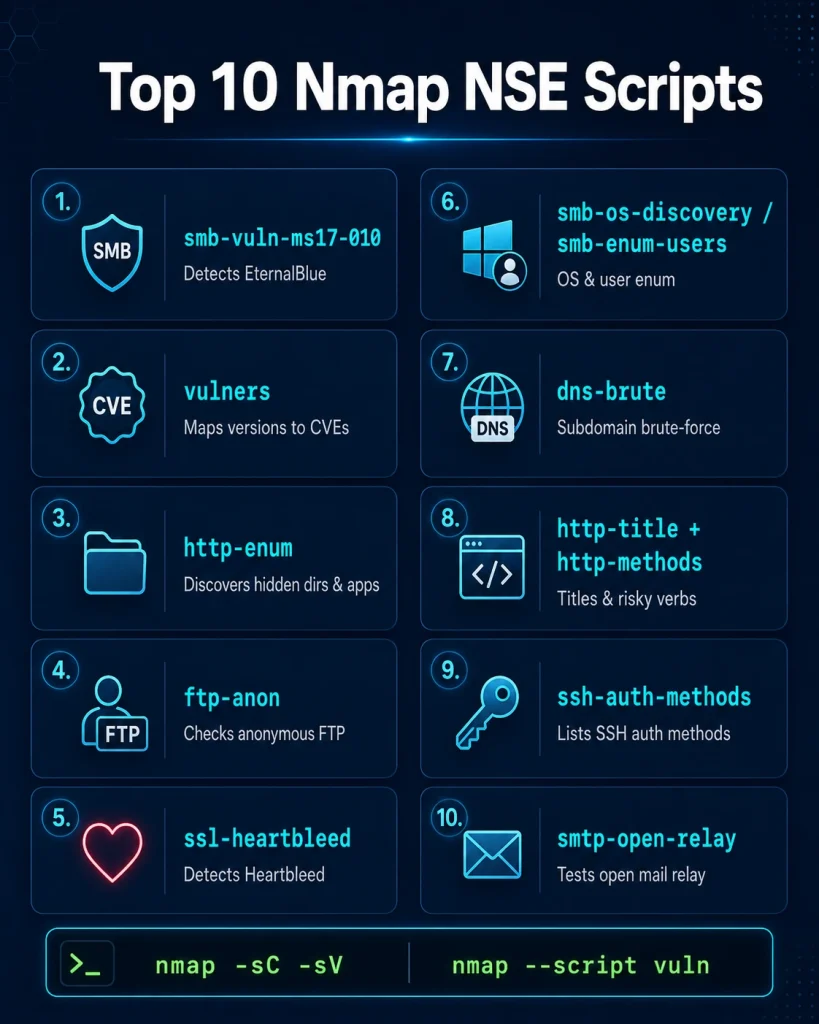
| 1 | smb-vuln-ms17-010 | Detects EternalBlue (MS17-010) SMB vulnerability |
| 2 | vulners | Maps detected service versions to known CVEs |
| 3 | http-enum | Discovers hidden directories, files, and web apps |
| 4 | ftp-anon | Checks for anonymous FTP login access |
| 5 | ssl-heartbleed | Detects the Heartbleed OpenSSL flaw (CVE-2014-0160) |
| 6 | smb-os-discovery / smb-enum-users | Fingerprints OS and enumerates SMB user accounts |
| 7 | dns-brute | Brute-forces subdomains via DNS |
| 8 | http-title + http-methods | Grabs page titles and reveals risky HTTP verbs |
| 9 | ssh-auth-methods | Lists supported SSH authentication methods |
| 10 | smtp-open-relay | Tests if a mail server allows open relaying |
Before diving into specific NSE scripts, it’s useful to have a solid command reference for Nmap itself. A complete overview of flags, scan types, timing options, and output formats is available in this detailed Nmap cheat sheet.
What Is the Nmap Scripting Engine (NSE)?
The Nmap Scripting Engine is a framework built into Nmap that runs Lua scripts to automate tasks beyond basic port scanning. It can detect vulnerabilities, enumerate services, brute-force credentials, and gather detailed intelligence during reconnaissance.
NSE scripts are grouped into categories, including:
- auth: authentication-related checks
- vuln: vulnerability detection
- discovery: service and network enumeration
- brute: brute-force login testing
- safe: scripts unlikely to crash or disrupt a target
- intrusive: scripts that may impact target stability
Nmap ships with over 600 NSE scripts, stored by default in /usr/share/nmap/scripts/ on Linux systems.
How to Run NSE Scripts
Basic Syntax
nmap --script <script-name> <target>Multiple scripts can be combined with commas:
nmap --script http-enum,ftp-anon <target>Running by Category
nmap --script vuln <target>-sC vs –script vuln
This is a common point of confusion for OSCP students:
- -sC runs Nmap’s default script set (the “safe” category)’, lightweight, low-risk, good for initial recon.
- –script vuln runs the full vulnerability-detection category, slower, more intrusive, and designed to actively identify exploitable flaws.
Use -sC for a fast first pass. Use –script vuln when you need deeper, authorization-backed vulnerability confirmation.
Authorization Warning: Intrusive and vuln-category scripts can crash unstable services or trigger alerts on monitored networks. Only run these against systems you are explicitly authorized to test.
Understanding how TCP connections are established helps interpret scan results more accurately. A clear breakdown written for security professionals is available here: TCP/IP handshakes.
The Top 10 NSE Scripts Every Pentester Should Know
1. smb-vuln-ms17-010 (EternalBlue)
What it does: smb-vuln-ms17-010 checks whether a Windows SMBv1 service is vulnerable to MS17-010, the flaw exploited by EternalBlue and the WannaCry ransomware outbreak.
Why it matters: Even in 2026, unpatched legacy Windows systems, especially in industrial, healthcare, and government networks, still show up vulnerable to this exact flaw during real assessments.
Command:
nmap -p445 --script smb-vuln-ms17-010 <target>Sample output:
PORT STATE SERVICE
445/tcp open microsoft-ds
Host script results:
| smb-vuln-ms17-010:
|   VULNERABLE:
|   Remote Code Execution vulnerability in Microsoft SMBv1 servers (ms17-010)
|     State: VULNERABLE
|     IDs:  CVE:2017-0143
|_    Risk factor: HIGH
Pro tip: A positive result here is a critical finding, flag it immediately. Pair it with Metasploit‘s exploit/windows/smb/ms17_010_eternalblue for exploitation during an authorized engagement.
2. vulners (or –script vuln)
What it does: The vulners NSE script cross-references detected service banners and version numbers against the Vulners.com CVE database, returning matching known vulnerabilities with CVSS scores.
Why it matters: It automates what used to take hours of manual searchsploit and CVE lookups, giving you a prioritized vulnerability list straight from a version scan.
Command:
nmap -sV --script vulners <target>Sample output:
PORT STATE SERVICE VERSION
22/tcp open ssh OpenSSH 7.2p2
| vulners:
|   cpe:/a:openbsd:openssh:7.2p2:
|       CVE-2018-15473    5.3   https://vulners.com/cve/CVE-2018-15473
|_      CVE-2016-10009    7.5   https://vulners.com/cve/CVE-2016-10009
Pro tip: vulners requires an internet connection and -sV version detection to work. It’s most reliable on well-known services like SSH, Apache, and MySQL.
3. http-enum
What it does: http-enum scans a web server for known directories, files, admin panels, and common web application fingerprints using a large built-in signature database.
Why it matters: It’s one of the fastest ways to identify forgotten admin panels, backup files, and outdated CMS installs, a frequent initial-access vector in web app pentests.
Command:
nmap -p80,443 --script http-enum <target>Sample output:
PORT STATE SERVICE
80/tcp open http
| http-enum:
|   /admin/: Possible admin folder
|   /backup/: Backup folder
|   /wp-login.php: WordPress login page
|_  /phpinfo.php: Possible information file
Pro tip: Follow up manually on every hit, automated enumeration finds candidates, not confirmed vulnerabilities.
4. ftp-anon
What it does: ftp-anon tests whether an FTP server allows anonymous login without valid credentials.
Why it matters: Anonymous FTP is a classic, still-common misconfiguration that can expose sensitive files, credentials, or provide a foothold for further attacks.
Command:
nmap -p21 --script ftp-anon <target>Sample output:
PORT STATE SERVICE
21/tcp open ftp
| ftp-anon: Anonymous FTP login allowed (FTP code 230)
|_drwxr-xr-x    2 ftp   ftp    4096 backup
Pro tip: Combine with ftp-syst and manual ls -la after login to catalog exposed files quickly.
5. ssl-heartbleed
What it does: ssl-heartbleed detects the Heartbleed vulnerability (CVE-2014-0160) in OpenSSL, which allows attackers to read protected memory, potentially leaking private keys and session data.
Why it matters: Despite being over a decade old, Heartbleed still turns up on unpatched legacy appliances, embedded devices, and neglected internal servers.
Command:
nmap -p443 --script ssl-heartbleed <target>Sample output:
PORT STATE SERVICE
443/tcp open https
| ssl-heartbleed:
|   VULNERABLE:
|   The Heartbleed Bug is a serious vulnerability in OpenSSL
|     State: VULNERABLE
|_    IDs: CVE:2014-0160
Pro tip: Never run active Heartbleed memory-dump exploitation against production systems without explicit written authorization, it can leak sensitive live data.
When investigating SSL/TLS issues or unusual network behavior discovered during NSE scans, packet analysis becomes essential. A practical reference for filters and shortcuts is available in this Wireshark cheat sheet.
6. smb-os-discovery / smb-enum-users
What it does: smb-os-discovery fingerprints the target’s OS version, hostname, and workgroup via SMB. smb-enum-users enumerates local user accounts when null sessions or weak permissions allow it.
Why it matters: These scripts give attackers (and defenders) a fast OS fingerprint and a potential username list for later password-spraying or brute-force attacks.
Command:
nmap -p445 --script smb-os-discovery,smb-enum-users <target>Sample output:
Host script results:
| smb-os-discovery:
|   OS: Windows Server 2016 Standard 14393
|   Computer name: FILESRV01
|_  Workgroup: CORP
| smb-enum-users:
|   CORP\Administrator
|_  CORP\backup_svc
Pro tip: Enumerated usernames become the input list for a follow-up crackmapexec or hydra password-spray attempt.
7. dns-brute
What it does: dns-brute brute-forces subdomains against a target domain using a built-in wordlist, revealing DNS records that aren’t publicly advertised.
Why it matters: Discovering forgotten subdomains (dev, staging, vpn, admin) frequently uncovers unpatched or unmonitored assets, prime bug bounty targets.
Command:
nmap --script dns-brute --script-args dns-brute.domain=<domain> <target>Sample output:
| dns-brute:
|   DNS Brute-force hostnames:
|     dev.example.com - 203.0.113.45
|     staging.example.com - 203.0.113.46
|_    vpn.example.com - 203.0.113.47
Pro tip: Cross-reference results with amass or subfinder for broader coverage, dns-brute is fast but not exhaustive.
8. http-title + http-methods
What it does: http-title grabs the <title> tag from a web page for quick service identification. http-methods lists which HTTP verbs (GET, POST, PUT, DELETE, TRACE) a server accepts.
Why it matters: Page titles help you triage hundreds of web hosts quickly, while exposed methods like PUT or TRACE can indicate file-upload or cross-site tracing vulnerabilities.
Command:
nmap -p80,443 --script http-title,http-methods <target>Sample output:
| http-title: Employee Portal - Login
| http-methods:
|   Supported Methods: GET HEAD POST PUT OPTIONS
|_  Potentially risky methods: PUT
Pro tip: A PUT method allowed on a misconfigured server can sometimes let you upload a web shell directly, verify manually before reporting.
9. ssh-auth-methods
What it does: ssh-auth-methods lists the authentication methods (password, publickey, keyboard-interactive) an SSH server accepts.
Why it matters: Knowing whether password authentication is enabled tells you immediately whether brute-force or credential-stuffing attacks are even feasible against that host.
Command:
nmap -p22 --script ssh-auth-methods --script-args="ssh.user=root" <target>Sample output:
PORT STATE SERVICE
22/tcp open ssh
| ssh-auth-methods:
|   Supported authentication methods:
|     publickey
|_    password
Pro tip: If only publickey is listed, don’t waste time on password brute-forcing, pivot to other attack vectors instead.
10. smtp-open-relay
What it does: smtp-open-relay tests whether a mail server is misconfigured to relay email from unauthenticated third parties, a setup that lets attackers send spoofed or spam email through the target’s domain.
Why it matters: Open relays damage domain reputation, enable phishing campaigns under a trusted name, and remain a surprisingly common finding in internal mail server assessments.
Command:
nmap -p25 --script smtp-open-relay <target>Sample output:
PORT STATE SERVICE
25/tcp open smtp
| smtp-open-relay: Server is an open relay (14/16 tests)Pro tip: Report this as a high-priority finding, open relays are trivial for attackers to abuse for large-scale phishing.
Recommended Powerful Scan Combinations
| Goal | Command |
|---|---|
| Fast initial recon | nmap -sC -sV <target> |
| Full vulnerability sweep | nmap -sV –script vuln <target> |
| Web app recon | nmap -p80,443 –script http-enum,http-title,http-methods <target> |
| SMB security audit | nmap -p445 –script smb-vuln-ms17-010,smb-os-discovery,smb-enum-users <target> |
| Mail server audit | nmap -p25 –script smtp-open-relay <target> |
After identifying vulnerabilities with NSE scripts such as smb-vuln-ms17-010 or vulners, the next step is often exploitation. Keep a ready Metasploit cheat sheet open for quick module searches, payload selection, and Meterpreter commands.
How to Update the NSE Script Database and Find More Scripts
Keep your script database current before every engagement:
nmap --script-updatedbTo browse all installed scripts:
ls /usr/share/nmap/scripts/ | less
To search for scripts by keyword:
ls /usr/share/nmap/scripts/ | grep smb
The official Nmap NSE documentation at nmap.org also maintains a full, searchable script index with usage details for every script.
The best way to master these NSE scripts is in an isolated lab environment. You can follow a complete step-by-step guide on how to set up a penetration testing lab or build a more detailed home penetration testing lab using VirtualBox or VMware.
Frequently Asked Questions FAQ’s
What is the best NSE script for finding vulnerabilities?
vulners and –script vuln are the best general-purpose options because they cross-reference live service versions against current CVE databases.
Is smb-vuln-ms17-010 still relevant in 2026?
Yes. Legacy Windows systems in industrial control, healthcare, and government networks are still regularly found vulnerable to MS17-010 during real-world assessments.
What’s the difference between -sC and –script vuln?
-sC runs Nmap’s default, low-risk “safe” script set for quick recon. –script vuln runs the full intrusive vulnerability-detection category and takes longer but finds more.
Are NSE vulnerability scripts safe to run on production systems?
Not always. Vuln and intrusive-category scripts can crash unstable services. Always get written authorization and consider running them during a maintenance window.
How do I run multiple NSE scripts at once?
Separate script names with commas: nmap –script script1,script2 <target>, or use a category name like –script vuln.
Where are NSE scripts stored on my system?
By default, at /usr/share/nmap/scripts/ on Linux. Run nmap –script-updatedb regularly to keep the database current.
Can NSE scripts be used for bug bounty hunting?
Yes, especially dns-brute for subdomain discovery and http-enum for finding exposed directories and admin panels, both are staples in bug bounty recon workflows.
Do I need Lua programming knowledge to use NSE scripts?
No. You only need Lua knowledge if you want to write custom scripts. Using the built-in library requires nothing more than standard nmap –script syntax.
Mastering these 10 NSE scripts gives you a fast, repeatable workflow for nearly any penetration test, OSCP lab, or bug bounty recon phase. Bookmark the command table above, practice each script in a lab environment like Hack The Box or TryHackMe, and build your own custom scan combinations as you gain experience.
