
Cybersecurity certifications remain the fastest and most measurable way to demonstrate security skills to employers. With 3.5 million unfilled cybersecurity positions globally and certified professionals earning 11–30% salary premiums over uncertified peers, the right credential accelerates hiring and pay.
Why Pursue Cybersecurity Certifications? Current Job Market Demand
Job market snapshot (2026):
- 3.5 million unfilled cybersecurity roles worldwide; 457,000+ open positions in the US alone.
- National average US cybersecurity salary: $138,800/year, more than double the US median income.
- CISSP certification correlates with a 22% salary premium; CompTIA Security+ adds 11%; cloud security certs add up to 25%.
- $200,000+ salaries are achievable in roles such as CISO ($200K–$275K), cloud security architect, and senior security engineer, typically after 8–15+ years of experience and stacked certifications (e.g., CISSP + CISM).
- Companies hiring certified professionals at scale: banks, hospitals, federal agencies/contractors, MSSPs, cloud providers (AWS, Microsoft, Google), and any enterprise with compliance obligations (HIPAA, PCI-DSS, FedRAMP).
- Average cost of a data breach: $4.88 million (IBM Cost of a Data Breach Report), driving sustained employer investment in certified security staff.
Why certifications matter specifically:
- They function as a resume filter, many ATS and HR systems search for credential acronyms (CISSP, CEH, Security+) before a human reviews the application.
- The U.S. Department of Defense Directive 8140.03 (formerly 8570) legally requires specific certifications for DoD and federal contractor cybersecurity roles, making certs non-optional in that segment.
- No four-year degree is required for most entry and mid-level roles, certifications substitute for formal education in the eyes of most employers.
Top 10 Cybersecurity Certifications for 2026
Ranked by combined weight of employer recognition, job-posting frequency, and salary impact:
- CISSP (ISC2): gold-standard senior/leadership credential
- CompTIA Security+: most widely required entry-level credential
- CISM (ISACA): top credential for security management/GRC leadership
- CEH (EC-Council): most recognized offensive-security name, strong DoD/HR keyword match
- CompTIA CySA+: leading SOC analyst/threat-detection credential
- OSCP+ (OffSec): most rigorous hands-on penetration testing credential
- CISA (ISACA): top IT audit and assurance credential
- CCSP (ISC2): leading cloud security architecture credential
- ISC2 CC: top free/low-cost entry point for absolute beginners
- CompTIA PenTest+: accessible mid-level penetration testing credential
Types of Cybersecurity Certifications
Certifications fall into four structural categories:
| Type | Description | Examples |
|---|---|---|
| Vendor-neutral | Cover concepts/skills independent of any product | CompTIA Security+, CISSP, CISM, CySA+ |
| Vendor-specific | Tied to a platform’s tools and architecture | AWS Security Specialty, Microsoft SC-200, Cisco CCNP Security |
| Role-based / practical | Test hands-on ability via simulated environments | OSCP+, CEH Practical, GIAC GPEN |
| Governance/compliance | Focused on audit, risk, and regulatory frameworks | CISA, CRISC, CGEIT |
What Is a Level 1 Certificate in Cybersecurity?
“Level 1” generally refers to entry-level/foundational certifications with no experience prerequisite, ISC2 CC, CompTIA Security+, and CompTIA ITF+ fall into this tier. They validate baseline knowledge rather than specialized or managerial competency.
Is CISA a cybersecurity certification?
Yes: CISA (Certified Information Systems Auditor), issued by ISACA, is a cybersecurity-adjacent certification focused on IT audit, control, and assurance, distinct from CISSP’s broader security focus and CISM’s management focus. It targets auditors, compliance officers, and risk professionals, not purely technical security roles.
Cybersecurity Certifications for Beginners (Including Free Options)
ISC2 Certified in Cybersecurity (CC)
- Status in 2026: The free “One Million Certified in Cybersecurity” enrollment program closed to new participants on September 20, 2026, after surpassing its goal of 1 million enrollments (65,000+ certified holders). Candidates with an unexpired exam code September still schedule and sit the exam through September 31, 2026.
- Cost after program closure: $199 exam fee + $50 annual maintenance fee (AMF).
- Domains: Security Principles, Business Continuity/DR/Incident Response, Access Controls Concepts, Network Security, Security Operations.
- Format: Computerized Adaptive Testing (CAT), 100–125 questions, 2 hours, passing score 700/1000.
- Prerequisites: None. Minimum age 16.
- Outline update: A refreshed exam outline takes effect September 1, 2026, verify which version applies before scheduling.
- Best for: Complete beginners, career changers, students testing interest in cybersecurity before committing further.
CompTIA Security+ (SY0-701)
- Cost: $439 exam voucher (US list price; figures of $439–$579 also circulate depending on source and timing, confirm current price at CompTIA.org before purchasing). CompTIA offers academic discounts through SheerID verification. Eligible students can view discounted pricing after their student status is approved. CompTIA does not publicly disclose the discount amount, so pricing is only visible to verified students during checkout.
- Domains: General Security Concepts, Threats/Vulnerabilities/Mitigations, Security Architecture, Security Operations, Security Program Management, and Oversight.
- Format: Up to 90 questions (multiple choice + performance-based), 90 minutes, passing score 750/900.
- Prerequisites: None official; CompTIA recommends Network+ and 2 years of IT admin experience with a security focus.
- Renewal: Every 3 years via 50 CEUs or a $150 total maintenance fee ($50/year); automatically renews on passing CySA+, CASP+, or SecurityX.
- Salary impact: Holders typically land $75K–$120K+, depending on role and experience; adds roughly 11% salary premium over uncertified peers.
- Best for: The standard first cybersecurity credential for IT professionals; required for many DoD 8140 IAT Level II roles.
Other Free/Low-Cost Beginner Options
| Google Cybersecurity Certificate (Coursera) | $49/month subscription typically $147–$294 total strong for absolute beginners with no IT background. |
| CompTIA ITF+ (IT Fundamentals) | cost= $209 useful pre-Security+ step for candidates with zero technical background. |
| Cybrary, TryHackMe free tiers | Free hands-on labs (not certifications, but build practical skill before paid exams). |
Free Cybersecurity Certifications Online
| Option | Vendor | Truly Free? | Status (2026) |
|---|---|---|---|
| Fortinet NSE 1–3 | Fortinet | Yes | Free training + exam, no paid voucher required |
| Cisco Intro to Cybersecurity | Cisco | Yes | Free badge-level course |
| CISA FedVTE | US CISA | Yes | Free, publicly accessible courses |
| AWS/Microsoft Learn badges | AWS, Microsoft | Yes | Free skill badges, not full certifications |
| Google Cybersecurity Certificate | Google/Coursera | Conditional | $49/month unless financial aid is approved |
| Cybrary, TryHackMe, Professor Messer | Various | Yes | Free training/labs only, not certifications |
Mid-Level Cybersecurity Certifications (Most Popular)
| Certification | Issuer | Cost | Focus |
|---|---|---|---|
| CompTIA CySA+ | CompTIA | $439–$580 | Threat detection, SOC analysis, and incident response |
| CEH (Certified Ethical Hacker) | EC-Council | $1,199 (exam) / $1,899–$3,499 (training bundle) | Offensive security concepts, hacking methodology |
| CompTIA PenTest+ | CompTIA | $439-$579 (depending on the vouchers) | Intermediate penetration testing |
| CCNA Security / Cisco certs | Cisco | $300 or Cisco Credits | Network security infrastructure |
What are the most popular cybersecurity certifications?
By job-posting frequency and name recognition: CompTIA Security+, CySA+, CEH, and CISSP dominate US job listings, per CyberSeek and labor market analytics data, as of 2026.
CySA+ specifics:
- Domains: Network Security and Operations, Vulnerability Management, Incident Response, Reporting, and Communication.
- Format: Up to 85 questions, 165 minutes, passing score 750/900.
- Prerequisites: None official; CompTIA recommends Security+ and Network+ plus 3–4 years of hands-on experience.
- Salary: typical range of $75,000–$110,000; some sources report a 31% salary boost over non-certified peers.
CEH specifics:
- Format: 125 multiple-choice questions, 4 hours (CEH ANSI); separate hands-on CEH Practical exam (6 hours, 20 challenges, 70% passing).
- Prerequisites: 2 years of information security work experience, or completion of official EC-Council training.
- Note: More theoretical than OSCP+; valued primarily for DoD 8570/8140 compliance and HR keyword matching rather than hands-on rigor.
Advanced Cybersecurity Certifications
CISSP, The Highest Standard in Cybersecurity Certifications
Certified Information Systems Security Professional, issued by ISC2, is widely regarded as cybersecurity’s gold-standard credential for senior and leadership roles.
- Cost: $749 exam fee (Americas/APAC); total investment with training typically $1,200–$5,500.
- Domains: 8 domains spanning Security and Risk Management, Asset Security, Security Architecture and Engineering, Communication and Network Security, Identity and Access Management, Security Assessment and Testing, Security Operations, and Software Development Security.
- Format: Computerized Adaptive Testing, 100–150 questions, up to 4 hours.
- Prerequisites: 5 years of cumulative paid work experience across 2+ of the 8 domains (1-year waiver available with an approved degree or credential, ISC2 cut its waiver-qualifying credential list from 50 to 25 effective September 1, 2026, removing CEH, CISA, CRISC, and OSCP+ from the waiver list).
- Associate of ISC2 pathway: Candidates without the required experience can pass the exam and hold “Associate of ISC2” status for up to 6 years while accruing experience.
- Renewal: 3-year cycle, 120 CPE credits, $125/year AMF.
- Salary: Average US salary $120,552; correlates with a $30K–$35K annual premium and roughly 3–4 month payback period on certification cost.
CISM, Certified Information Security Manager (ISACA)
- Cost: $575 (ISACA members) / $760 (non-members); annual maintenance $45–$85.
- Domains: 4 domains, Information Security Governance, Information Security Risk Management, Information Security Program, and Incident Management.
- Format: 150 questions, 4 hours, scaled passing score of 450/800.
- Prerequisites: 5 years of information security experience, including 3 years in security management (waivers up to 2 years available for CISA/CISSP holders or relevant postgraduate degrees).
- Salary: ISACA’s own 2025 global salary survey reports an average of $149,000; other sources report figures in the $95K–$135K range, depending on region and methodology, geography and role title materially affect this number.
- Best for: Security management, governance, and GRC-track professionals rather than purely technical roles.
CISA, Certified Information Systems Auditor (ISACA)
- Focus: IS auditing, control, and assurance, not general security architecture.
- Prerequisites: 5 years of relevant experience (with partial waivers available).
- Salary: Roles citing CISA/CRISC average $80,000–$125,000.
- Best for: GRC, audit, and compliance career tracks.
OSCP+, Offensive Security Certified Professional
- Cost: $1,699 (course + exam bundle through OffSec’s PEN-200).
- Format: A grueling 24-hour hands-on hacking exam against live machines, plus a 24-hour report-writing window.
- Prerequisites: None official, but strong networking/Linux fundamentals expected; 4–6 months prep typical for IT backgrounds, up to 12 months for non-technical candidates.
- Renewal: OSCP+ expires after 3 years from the date of certification
- Salary: $90,000–$130,000 for entry pen-test roles with 1–2 years experience; commands a $20K–$30K premium over CEH in pure pen-testing roles.
- Best for: The most rigorous, hands-on, validated offensive security credential available; preferred over CEH by technical hiring managers.
Highest-Paying Cybersecurity Certifications
Ranked by the reported average/top-end US salary association:
| Certification | Salary Association | Why |
|---|---|---|
| CISM | $149,000 avg (ISACA survey); $170K+ combined with CISSP | Management premium is scarce due to the experience requirement |
| CISSP | $120,552 avg; up to $200K+ at CISO/architect level | Broadest senior-role recognition, $30K–$35K salary lift |
| CCSP | $130,000–$168,000 | Cloud security architecture demand |
| OSCP+ | $90,000–$130,000 entry; up to $205,000 senior red team | Hands-on rigor commands a $20K–$30K premium over CEH |
| CISA | $80,000–$125,000 | Audit/GRC leadership track |
| CEH | $75,000–$125,000 | Strong recognition but multiple-choice format caps premium |
| CompTIA CySA+ | $75,000–$110,000 | 31% boost over non-certified SOC analysts |
| CompTIA Security+ | $55,000–$120,000 | 11% premium; widest entry-level reach |
| ISC2 CC | $50,000–$75,000 | Floor-level credential is best as a stepping stone |
Key pattern: the highest-paying certifications are management/leadership credentials (CISM, CISSP) rather than the most expensive ones, OSCP+ costs more than CISM but pays less, because CISM targets roles that are inherently higher-paid.
CISSP vs. CISM: Quick Comparison
| Factor | CISSP | CISM |
|---|---|---|
| Focus | Broad technical + managerial security | Security management/governance |
| Issuer | ISC2 | ISACA |
| Cost | $749 | $575–$760 |
| Experience required | 5 years, 2+ domains | 5 years, 3 in security management |
| Avg. US salary | $120,552 | $149,000 (ISACA survey) |
| Best for | Architects, engineers, senior technical leads | CISOs, security program managers, GRC leads |
Combining both: a CISM + CISSP holder averages $170,000+, making the pairing one of the highest-value combinations in the field.
Specialized Cybersecurity Certifications
| Specialization | Key Certifications | Notes |
|---|---|---|
| Cloud security | CCSP (ISC2, $599), AWS Security Specialty ($300), Azure SC-200 ($165) | The CCSP experience requirement is fully satisfiable via an existing CISSP |
| AI security | ISC2 AI security workshops/certificates (emerging in 2026) | No single dominant “AI cybersecurity certification” yet exists; ISACA and ISC2 are both expanding offerings as AI governance/security demand grows |
| Penetration testing | OSCP+, CEH, GPEN, PNPT, CRTP | OSCP+ for rigor; CEH for HR/DoD keyword matching |
| Compliance/GRC | CISA, CRISC, CGEIT | Audit and regulatory framework focused |
| Security operations | CySA+, Splunk Certified Cybersecurity Defense Analyst ($130) | SOC analyst and threat-hunting roles |
AI cybersecurity certification status (2026):
While interest in the best AI cybersecurity certifications continues to grow, no single AI security credential has yet to achieve the market dominance of the CISSP or Security+. ISACA and ISC2 have both signaled “big, bold initiatives” in this space for 2026, but broad-scale standalone AI-security certifications have not yet emerged. For now, vendor-specific AI security credentials and badges from Microsoft, Google, and AWS should be viewed as supplementary rather than primary cybersecurity certifications.
Cybersecurity Certifications Roadmap
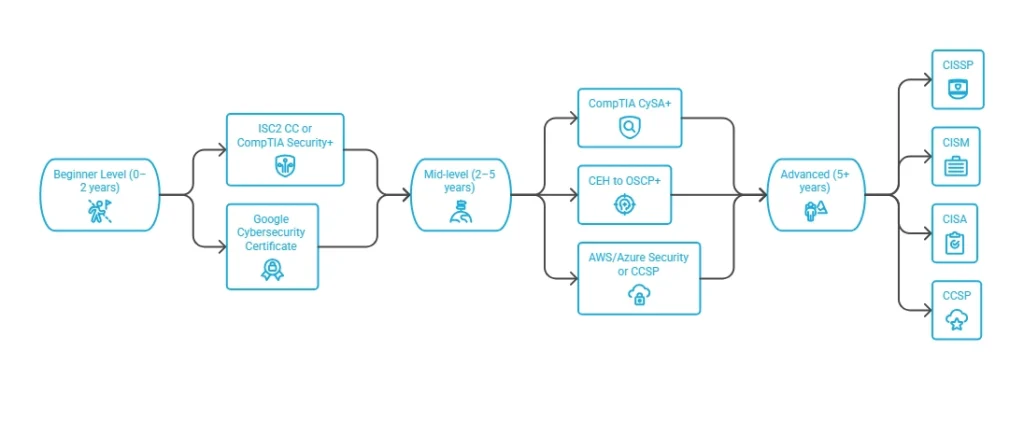
Beginner (0–2 years):
- ISC2 CC (if still eligible) or CompTIA Security+, 2–3 months, 80–120 study hours
- Optional: Google Cybersecurity Certificate as a structured on-ramp
Mid-level (2–5 years): 3. CompTIA CySA+ (blue team) or CEH → OSCP+ (offensive track), 3–6 months additional 4. Optional specialization entry: AWS/Azure security badge, CCSP groundwork
Advanced (5+ years): 5. CISSP (technical/architecture leadership track) or CISM (management/GRC track), 3–6 months study plus the multi-year experience prerequisite 6. Optional stacking: CISA for audit-heavy environments, CCSP for cloud-focused leadership
Duration: Full beginner-to-job-ready path (CC/Security+) ≈ 6 months. Reaching CySA+/OSCP+ adds 3–6 months. CISSP/CISM require 3–6 months of study layered on top of the 5-year experience clock, this is the long pole, not the studying.
Is 26 too late to start a cybersecurity career?
No, Absolutely Not. Most cybersecurity professionals enter the field via a career change, often in their late 20s to 40s, from IT support, networking, the military, or unrelated fields. Experience requirements for CISSP/CISM can be met through any qualifying full-time security work, age is not a structural barrier.
What certification should I do first?
- No IT background → ISC2 CC or Google Cybersecurity Certificate
- Some IT background → CompTIA Security+
- 1–2 years security experience, analyst track → CySA+
- 1–2 years security experience, offensive track → OSCP+ (skip CEH unless a specific job requires it)
- 5+ years, technical leadership → CISSP
- 5+ years, management/GRC → CISM or CISA
How to Choose the Right Cybersecurity Certification
Decision framework:
- Match the cert to the target role, not the most prestigious name. A GRC analyst gains little from CEH; a pentester gains little from CISA.
- Check experience prerequisites first, CISSP and CISM both require 5 years; don’t pay for an exam you can’t yet sit for credibly.
- Verify employer/DoD requirements, under DoDM 8140.03, specific certs (Security+, CISSP, CEH, CASP+/SecurityX) are mandatory for designated federal roles. Confirm before choosing a substitute.
- Budget realistically, factor training and retake costs, not just the exam voucher; total cost is typically 2–4x the voucher price.
- Avoid jumping straight to CISSP/OSCP+ without foundations, under-prepared attempts waste both money and the mandatory retake waiting periods (CISSP: 30/90/180 days for 2nd/3rd/4th+ attempts).
Are there other cybersecurity certifications out there?
Yes, GIAC/SANS certifications (GSEC,>$949, GPEN, GCIH) offer deep technical rigor at premium prices (often $2,000+ with training bundles), Splunk and vendor-specific SIEM/cloud certs serve niche toolchains, and CRISC/CGEIT extend the ISACA governance track beyond CISA/CISM. Evaluate any unlisted cert against the same framework above: does it match a specific job requirement or skill gap you actually have?
Comprehensive Comparison Table
| Certification | Level | Cost | Prep Time | Renewal | Salary Range | Best For |
|---|---|---|---|---|---|---|
| ISC2 CC | Beginner | $199 | 40–80 hrs | $50/yr | $50K–$75K | Career starters, no experience |
| CompTIA Security+ | Beginner | $439-$579 | 80–120 hrs | $150/3yr | $55K–$120K | Standard entry credentials, DoD roles |
| CompTIA CySA+ | Intermediate | $439-$579 | 150–250 hrs | $150/3yr | $75K–$110K | SOC analyst, threat detection |
| CEH | Intermediate | $1,199–$3,499 | 60–150 hrs | 3yr cycle | $75K–$125K | Offensive security entry, DoD/HR keyword match |
| OSCP+ | Intermediate–Advanced | $1,699 | 4–12 months | Never expires | $90K–$205K | Hands-on pentesting, red team |
| CISA | Advanced | $575–$760 | 3–6 months | 3yr/CPE | $80K–$125K | IT audit, compliance |
| CISM | Advanced | $575–$760 | 3–6 months | 3yr/CPE | $95K–$170K+ | Security management, GRC leadership |
| CISSP | Advanced | $749 | 3–6 months | 3yr/CPE | $120K–$200K+ | Senior technical/architecture leadership |
| CCSP | Specialized | $599 | 3–4 months | 3yr/CPE | $130K–$168K | Cloud security architecture |
Preparation, Costs, and Realities
How much does CompTIA Security+ cost?
$439 for the exam voucher alone (US list price). Total realistic budget including study materials: $600–$1,000 for self-study, $1,500–$3,500 for bootcamp training. Retakes cost the full $425 again, no discount, so quality first-attempt preparation has a direct ROI.
General preparation cost patterns across certifications:
- Self-study: Cheapest path; requires discipline; relies on free/low-cost resources (Professor Messer, official study guides, practice tests).
- Online courses: $150–$800; structured but self-paced.
- Bootcamps: $1,500–$5,000+; highest pass rates, fastest timeline, often employer-sponsored.
- Academic/military discounts: Up to 10% off CompTIA exams with a valid .edu email; DoD tuition assistance and GI Bill benefits often cover the costs of Security+ and CISSP for active-duty service members and veterans.
Is a Certificate in Cybersecurity Worth It?
For the ISC2 CC specifically: yes, when free or low-cost, ISC2 survey data shows 65% of CC holders work in cybersecurity roles and another 22% work in IT, with most using it as a stepping stone rather than a terminal credential. As a paid $199 entry point after September 2026, it remains worthwhile primarily for candidates who lack any existing IT credentials or experience to point to.
For certifications broadly: yes, when matched correctly to career stage. The data consistently shows payback periods of weeks to months relative to salary increases, particularly for CISSP and CCSP. The risk is not the certification’s value, it’s choosing the wrong one for your current experience level.
Frequently Asked Questions FAQ’s
What is a CISSP salary?
The average US CISSP salary is $160,000+/year, with a documented $30,000–$35,000 annual premium over non-certified peers. Senior CISSP-holding roles, security architect, CISO, security director, range from $150,000 to $275,000+, depending on seniority, location, and whether it’s paired with CISM.
What’s the best AI cybersecurity certification?
No single AI-security certification has reached CISSP- or Security+-level market dominance yet. ISACA and ISC2 have both signaled major AI-security initiatives for 2026, but haven’t released a flagship standalone credential at scale. Until one emerges, the most practical options are vendor AI-security badges from Microsoft, Google, and AWS, used as a supplement to, not a replacement for, a core credential like Security+, CISSP, or CCSP.
Which certificate is best for cybersecurity?
There is no single “best”, it depends on career stage. Best overall entry point: CompTIA Security+. Best overall advanced credential: CISSP. Best for management: CISM. Best for hands-on technical proof: OSCP+.
Can I make $200,000 a year in cybersecurity?
Yes, but typically only with 8+ years of experience, an advanced certification (CISSP and/or CISM), and a leadership or specialized title, CISO, principal security architect, or senior cloud security architect roles in major metro areas regularly list $200K–$275K.
Is CISSP worth it in 2026?
Yes, for professionals with 4–5+ years of qualifying experience. It remains the most universally recognized senior credential, with 9,400+ active CISSP-requiring job listings and a documented $30K–$35K average salary premium.
Is the ISC2 CC still free?
No, new enrollments in the free program closed September 20, 2026. Anyone holding an unexpired exam code from before that date can still test through September 31, 2026. After that, CC costs $199 plus the $50 annual maintenance fee.
CompTIA Security+ or ISC2 CC first?
If you can no longer access a free CC voucher, go straight to Security+, it carries more weight with employers and satisfies DoD 8140 requirements that CC does not.
Do certifications expire?
Yes, Most do (OSCP+, CompTIA, ISC2, and ISACA credentials renew every 3 years via CPEs/CEUs and maintenance fees).
CEH or OSCP+ for penetration testing?
OSCP+ for actual technical credibility and red-team hiring; CEH only if a specific job posting or DoD contract explicitly requires it, CEH is multiple-choice and tests knowledge, not hands-on exploitation skill.
Do I need a college degree for cybersecurity certifications?
No. None of the major certifications covered here, Security+, CySA+, CEH, CISSP, CISM, CISA, OSCP+, require a degree. CISSP and CISM allow a relevant degree to substitute for part of the experience requirement, but it’s a waiver, not a requirement.
